15 - Introduction to computer security
Class: CSCE-313
Notes:
Intro to Computer Security
Is computer security necessary?
- Because a lot of money is handled by computers.
- Because a lot of important information is stored on and handled by computers.
- Would you want someone to find out your GPA, SAT, or GRE scores?
- How about your "credit", or "medical" history?
- There needs to be a mechanism to control sharing of information.
- Because society is increasingly dependent on the correct operation of computers.
Notes:
- The amount of money you won at a bank account is really just a number stored in someone else's computer
- Money is represented in some form inside a computer
- Securing computers is then important
- All of your educational scores are basically some digitization of your scores in some computer system
- Traditionally we understood security in terms of confidentiality, but that is not the only thing within security
- But integrity is another thing, they may be able to change info without actually able to see what it is
Examples of security problems
- The Internet Worm c1988 (buffer overflow).
- Spread over the Internet to many sites.
- Around 6000 sites were shut down to get rid of it.
[rtm]
- Virus Attacks.
- Denial of Service Attacks.
- Flooding of web servers with enormous rate of requests.
- Flooding networks enroute the target.
- Exploiting target TCP state machines.
Notes:
- Guy called Robert Morris
- Grad student at Cornell
- He wrote the Internet Worm
- It exploited techniques of buffer overflow that even the designers of Vax at that time, were stunned at what he had done
- This classic buffer overflow
- 20,725 results for "buffer overflow" in the CVE database
- They have found many many ways of doing it
- A worm is an independent thing
- Could actually connect to other hosts, and would look at what hosts you are connected to
- Then it would exploit that and propagate itself
- Virus infect an executable and live in there
- But they need a host in order to exists and depend on the file being run to proceed
- Denial of Service is a different kind of attack
- Preventing the good guy to access a service
Rewritten notes:
- Worms vs. Viruses: It is important to distinguish between these two threats. A virus requires a host executable to live inside of; it depends on that host file being run to do its damage. A worm, however, is completely independent. It can actively search for connected hosts, exploit vulnerabilities, and propagate itself across the network.
- The Morris Worm (1988): A classic example of a worm was created by Cornell grad student Robert Morris. It exploited buffer overflow vulnerabilities so effectively that it stunned system designers and shut down around 6,000 sites across the early internet.
- Denial of Service (DoS): Unlike a virus or worm that tries to infect or steal data, a DoS attack has a different goal: preventing legitimate users from accessing a service (like flooding Amazon.com so real customers give up and go elsewhere).
Buffer Overflow in a Nutshell
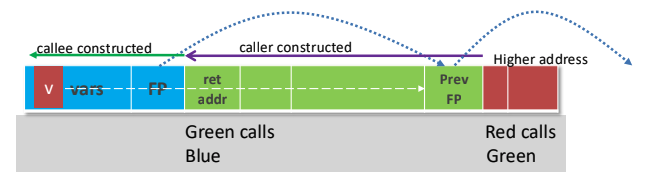
Notes:
- Stack grows towards the left
- Green function calls the blue function
- The calling convention is that the green function will push the return address
- The address that the blue function must return when it finishes
- The blue function allocates space on the stack for its local variables
- Array boundaries are not checked in C
- Reads input from the client and assigns it to V
- V is growing in the opposite direction of the stack
- If your attacker is very smart, he will make you overwrite the return address, once you have overwritten it, instead of returning where you would return, in the earliest simple case, you will actually return to the code you pushed on the stack (the malicious code)
- This sorts of attacks do not work now, but when they came out, they were an amazing thing
Rewritten notes:
- The Stack Layout: When one function calls another, the system pushes a return address onto the stack. This tells the program exactly where to resume execution once the called function finishes. The called function then allocates space on the stack for its own local variables (like an array).
- The Vulnerability: The C programming language does not automatically check array boundaries. If a program reads input from a user and blindly writes it into a local array, a smart attacker can provide an oversized input.
- The Hijack: Because the local array grows towards the return address on the stack, the overflowing data will literally overwrite that return address. When the function finishes, instead of returning to the legitimate program, it returns to an address chosen by the attacker—typically pointing to malicious code the attacker hid inside the overflowing data
Denial of Service
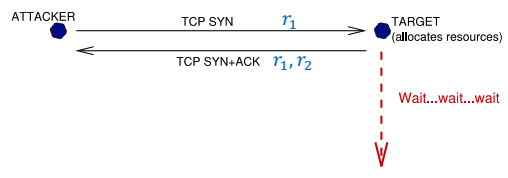
Notes:
- Bad guys push so much traffic to amazon.com that you cannot get to that destination
- The way that TCP/IP works is that if it detects a lot of traffic, it starts slowing down its transmission rate
- After a few minutes you will place your order not at amazon.com but somewhere else
- This is what they want you to move to as a client
- Attacker will pretend like it is doing a real TCP handshake
- The attacker sends the first packet and proposes a random number
- The server allocates resources necessary for that connection (i.e. sockets, buffers)
- Then the server sends a reply to the attacker, and the attacker never completes the TCP handshake, so the allocated resources stay in the server
Rewritten notes:
- Resource Exhaustion: A DoS attack works by pushing so much traffic that the server gets overwhelmed. Because TCP/IP is designed to slow down its transmission rate when it detects heavy congestion, the entire service grinds to a halt for normal users.
- Exploiting the TCP Handshake: A very common DoS technique exploits the TCP state machine.
- The attacker pretends to start a real connection by sending the first handshake packet with a random number.
- The server receives it, strictly allocates the necessary system resources (like sockets and memory buffers) for the pending connection, and sends a reply.
- The attacker never completes the handshake.
- The Result: The server is left holding those allocated resources open indefinitely. If the attacker does this millions of times, the server completely runs out of resources and crashes or freezes.
What is computer security?
Computer security is the protection given to an information system to preserve its "CIA"!
- Confidentiality
[they want your data]. Assets of a computing system are accessible only to "authorized" parties. - Includes reading, printing, or even testing for existence of an object.
- What if I saw an ambulance parked in the opposite lane at 5am on Sunday?
- Integrity. Assets can be modified only by authorized parties.
- In security, usually distinct from structural integrity (well formedness).
- Availability
[they want your bandwidth, cpu, disk]. Assets are accessible to authorized parties.
Notes:
Why is security hard?
- It's often a tradeoff between "convenience" and "security", or between "performance" and "security".
- Wily human/AI opponents seek to outwit us. Must assume that the opponent will attack the weakest point.
- Must get everything right-any mistake is an opportunity for the opponent.
- Bug-free software?
Notes:
- Security is often a tradeoff with convenience
- It is hard to remember usernames and passwords
- There is also the performance aspect
- If you have security measures in place, you pay a price in performance
- The other problem is that we are very smart opponents
- Your opponent will find the weakest link in your chain
- You cannot afford to relax in a point
- You must get everything right in a complex system that is already very difficult
- Bug-free software?
- If it is not bug-free, the attacker may be able to exploit this bug and use it to gain control of your system
- Today we even see AI opponents outperforming humans in detecting vulnerabilities or exploiting them
1. Confidentiality
Confidentiality: Encryption
Encryption is the transformation of information using a secret (encryption key), so that the transformed information can only be read using another secret, (decryption key).
The decryption key in many cases is the same as the encryption key.
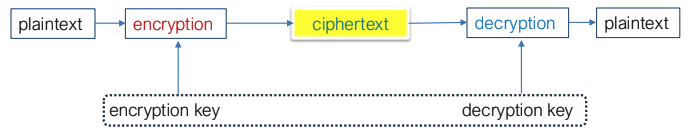
Notes:
- The Core Concept: Encryption is the process of transforming readable information (plaintext) into unreadable garbage (ciphertext) using a secret encryption key. To read the information again, it must be transformed back using a decryption key.
- Hiding Redundancy: Natural human language has a lot of predictability and redundancy (e.g., if you see "I'd like fries and a...", you can guess the next word is "burger"). A good encryption algorithm scrambles this predictability so the ciphertext reveals no clues.
- Symmetric vs. Asymmetric:
- Symmetric Encryption: Uses the exact same key to both encrypt and decrypt the data.
- Asymmetric Encryption: Uses different keys for the encrypting and decrypting processes.
- Basic Example: The ROT1 (Caesar) cipher simply shifts every letter by one position in the alphabet, turning "ATTACK" into "BUUBDL".
Encryption ~ Speaking
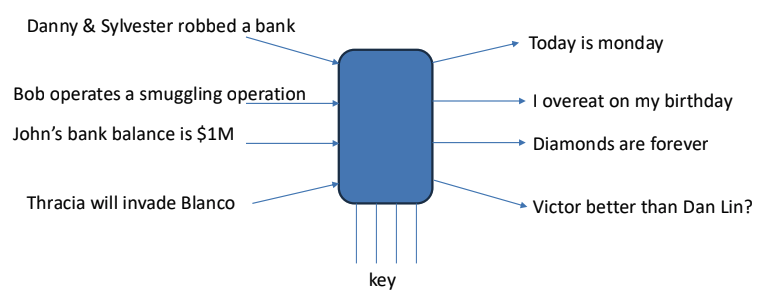
Notes:
- The Permutation Model: You can think of encryption as a mathematical mapping between an input space and an output space. If you have 4 possible messages and 16 different keys, picking a specific key (like
0110) locks in a specific "permutation" (or wiring) of how those inputs translate to the outputs. - Kerckhoffs's Principle (Kirkoff's Law): This is a fundamental rule of cryptography. It states that you must assume a smart attacker knows everything about how your encryption algorithm (the "black box") works. The security of the system must never rely on keeping the algorithm a secret; it must rely entirely on keeping the key a secret.
Confidentiality: access control
Access control is a set of rules and policies that limit access to confidential information to those people or systems with a "need to know."
This need to know can be determined:
- by identity, such as a person's name or a computer's serial number, or
- by role that a person has, such as being a manager or a computer security specialist.
Notes:
- The "Need to Know": While encryption protects data while it is sitting at rest, Access Control uses rules and physical policies to physically or digitally limit access to information only to those who have a strict "need to know".
- Authentication vs. Authorization: Access control breaks down into two distinct steps:
- Authentication: Proving who you are (e.g., holding a specific company badge proves "I am Jack Smith").
- Authorization: Determining what you are allowed to do now that your identity is proven.
- Identity vs. Role-Based Access:
- Identity-Based Access: Grants permissions based on a specific person's name or a machine's serial number. This is often too granular and difficult to manage in large organizations.
- Role-Based Access Control (RBAC): Grants permissions based on the capacity in which someone acts (e.g., "Manager" or "Instructor"). If a user assumes the role of an instructor, they are authorized to see student grades, making their actual underlying identity less important for the policy.
- Look at Access Control Models
Confidentiality: Authentication
Authentication is the determination of the identity or role that someone has. This determination can be done based on a combination of items.
- An item that the person has: smart card, key fob
- An item that the person knows: password
- An feature that the person is: fingerprint
Notes
- Proving Identity: Authentication answers the question, "Who are you?" It is the process of verifying the identity or role that someone claims to have.
- The Three Classic Factors: Authentication is traditionally determined by combining three categories of evidence:
- Something you have: A physical object in your possession, such as a smart card, a physical key, or an RFID fob. The system assumes that if you possess the key, you are the authorized user.
- Something you know: A secret piece of information, like a password or a PIN.
- Something you are: A unique physical or biometric feature, such as a fingerprint or a retinal scan.
Confidentiality: Authorization
Authorization is the determination of whether a person or system is allowed access to resources, based on an access control policy or not.
Such authorizations should prevent an attacker from tricking the system into letting him have access to protected resources.
Notes:
- Granting Permissions: Once you are authenticated, authorization answers the question, "What are you allowed to do?" It determines if a person or system is permitted to access specific resources based on established access control policies. A strong authorization system prevents an attacker from tricking the system into granting access to protected data.
- Static vs. Dynamic Policies:
- Static Policies: Traditional systems, like the UNIX file system, evaluate access using simple, static rules (e.g., checking if your user ID matches the file's read/write permissions).
- Dynamic Policies: Modern systems often require complex, dynamic rules. For example, a financial system might allow a user to view the balance sheet of any company, but the moment they view Company A's sheet, the policy dynamically updates to forbid them from viewing a competitor's sheet to prevent conflicts of interest. Evaluating these dynamic policies is computationally complex.
Confidentiality: Physical Security
Physical security is the establishment of physical barriers to limit access to protected computational resources.
E.g.: Locks on cabinets, computers, windowless rooms, sound dampening materials, walls with copper meshes (called Faraday cages) so that electromagnetic signals cannot enter or exit the enclosure.
The only truly secure system is one that is powered off, cast in a block of concrete and sealed in a lead-lined room with armed guards - and even then I have my doubts.
Notes:
- The Physical Barrier: Cybersecurity is useless if someone can just walk away with your server. Physical security establishes tangible barriers to limit access to computational resources.
- Protection Techniques: This includes putting locks on server cabinets, using windowless rooms so attackers cannot read monitors from 200 meters away with binoculars, and using sound-dampening materials.
- Faraday Cages: To protect against wireless attacks (like someone stealing your RFID card credentials via electromagnetic signals), highly secure rooms use copper meshes called Faraday cages, which completely block electromagnetic signals from entering or exiting.
- The Ultimate Truth: As the quote highlights, absolute security is practically impossible. The only truly secure system is one that is powered off, cast in concrete, and sealed in a lead-lined room with armed guards—and even then, it's not guaranteed.
2. Integrity
Integrity-the property that information has not been altered in an unauthorized way. Integrity is a separate property than Confidentiality.
- It protects the data from tampering.
Notes:
- If you have 50 root certs in your browser, you can't really trust
- If I could add my own root cert in your browser, then I can send you off to my site, and I can make it so nice that you won't be able to tell the difference
- The problem is that if I can change something for you, I can compromise it
Integrity: checksum
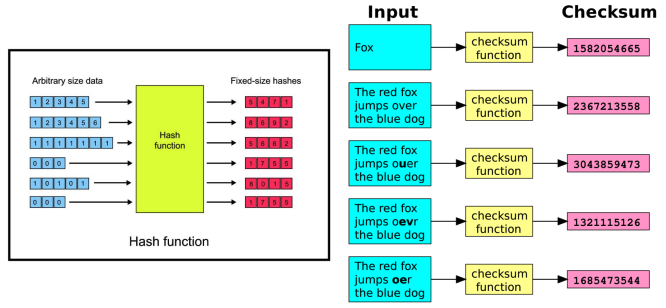
A checksum is a function that maps data to a numerical value.
A checksum function depends on the entire data and is designed in a way that even a small change to the input (such as flipping a single bit) is highly likely to result in a different output value.
Notes:
- Takes an arbitrary-sized data and hashes it into a fixed length numerical value
- One way to check if your files have changed is basically to duplicate the data and check for differences, but this can be very expensive
- You can instead transform your data into a constant-size output, and then compare that to the original hash of the data, this is much easier
For example:
$ cat foo
ATTACK AT DAWN
- If I am able to change it to
ATTACK AT MOON, that would be bad enough
$ sha1sum foo
0806b996cbad73b0f5e0f68898d3c80eaea27bcf  foo
But when we do
$ cat foo
ATTACK AT MOON
$ sha1sum foo
ee6f10e08c5a841ccd2a5261d0326623855fd3a3  foo
- The hash changed!
Integrity: error correcting codes
Error correcting codes are methods for storing data in such a way that small changes can be easily detected and automatically corrected.
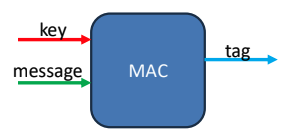
A MAC is like a private hash function that only you can compute because you know the key.
Notes:
- Error Correcting Codes (ECC): While standard checksums or hashes can only tell you if data has been tampered with, error correcting codes go a step further. They are specialized data storage methods designed so that if small changes or corruptions occur, the system can not only easily detect them but also automatically correct them back to their original state.
- MAC (Message Authentication Code): You can think of a MAC as a "private" hash function. It takes the concept of a standard checksum and specializes it by injecting a secret cryptographic key into the mathematical process.
- The Security Advantage: This secret key ensures that the resulting checksum is completely unique to that specific key. This solves a major vulnerability: an attacker might easily alter a file and compute a new standard checksum to trick the system. However, they absolutely cannot compute a valid MAC to cover their tracks unless they know the secret key.
3. Availability
Availability is the property that information is accessible in a timely fashion by those authorized to do so.
Computational redundancy consists of computers and storage devices that serve as a fallback in the case of failures.
Notes:
- Basically that an attacker is not able to degrade your access to the service or the information
- Usually the technique to handle this is to have redundancy
- Multiple copies of the data
- Break data into multiple shares and re-combine them, etc.
Design Principles for Secure Systems
- Economy of
[protection]mechanism. Keep the design as simple and small as possible. - Fail-safe defaults. Base access decisions on permission rather than exclusion.
- Complete mediation. Every access to every object must be checked for authorization.
- Open design. Security through obscurity is not.
- Separation of privileges. Two locks are better than one!
- Least privilege. Operate using the least privileges necessary to complete job.
- Least common mechanism. Minimize the amount of mechanism common to more than one user and depended on by all users.
- If
glibcis huge and everyone uses on it, then bugs in the library are more likely and affect more! boringsslvsopenssl
- If
- Acceptability. Human interface should be easy to use.
Notes:
- If you follow these, you will have a more secure system
- Economy of protection mechanism
- Keep it simple and stupid (KISS) principle
- Fail-safe defaults
- By default everything should be denied, and should expressively permit someone to do something
- Again the tradeoff between convenience and security hits
- Complete mediation
- You want security to check every access to every object
- Open design
- Goes back to kirkoffs law
- People have spent billions of dollars believing that if they could make that hardware secure, and no-one would be able to reverse engineer the hardware, they will be secure
- The only security that you should have should be that key, not the entire system
- Go in the forward direction, not in the backward
- Separation of privileges
- You need two people to insert the key at the same time to launch the nuke
- Least privilege
- Do you need to be root if you just need to troubleshoot networking?
- No, you should only be given the privilege you need
- Least common mechanism
- You do not want a common mechanism to become so large so that it satisfies a large set of users, because it can become liable
- If there is a single bug somewhere, somebody else that is not using that particular thing can see the effects
- For example:
boringsslis more boring, but more secure by removing old deprecated encryption methods
- Acceptability
- No matter how secure a system is, if it is difficult to use, people will find ways to break it
Questions
A Unix file system checks permissions on every file access - not just when a file is first opened/ Even if a process has already read from a file, each subsequent read is re-checked against the current ACL.
Answer: Complete mediation
- Every access to every object must be checked
A new employee at a hospital is given read/write access to all patient records, billing, HR files, and the pharmacy system - 'just in case they need it later.'
Answer: Least privilege
- You only want to give the privileges that they need to do their job
A bank's wire-transfer system requires both a manager's password and a hardware token before a large transfer would be approved
Answer: Separation of privileges
An operating system's kernel is kept as small as possible, with only the most essential functions inside it. Everything else runs in user space.
Answer: Economy of [protection] mechanism
- KISS principle
An operating system's kernel security system requires users to enter a 47-step authentication ritual before they can access their own calendar. Most users end up writing their password on a sticky note.
Answer: Acceptability
- This is not acceptable
- We want systems to work with people