02 - Data Acquisition
Class: CYBR-405
Notes:
Cyber History
- 'Cyber' is from the Greek word for navigator
- Dr. Norbert Wiener coined 'cybernetics' around 1948
- Cybernetics - the science of communications and automatic control systems in both machines and living things
What is Cybersecurity?
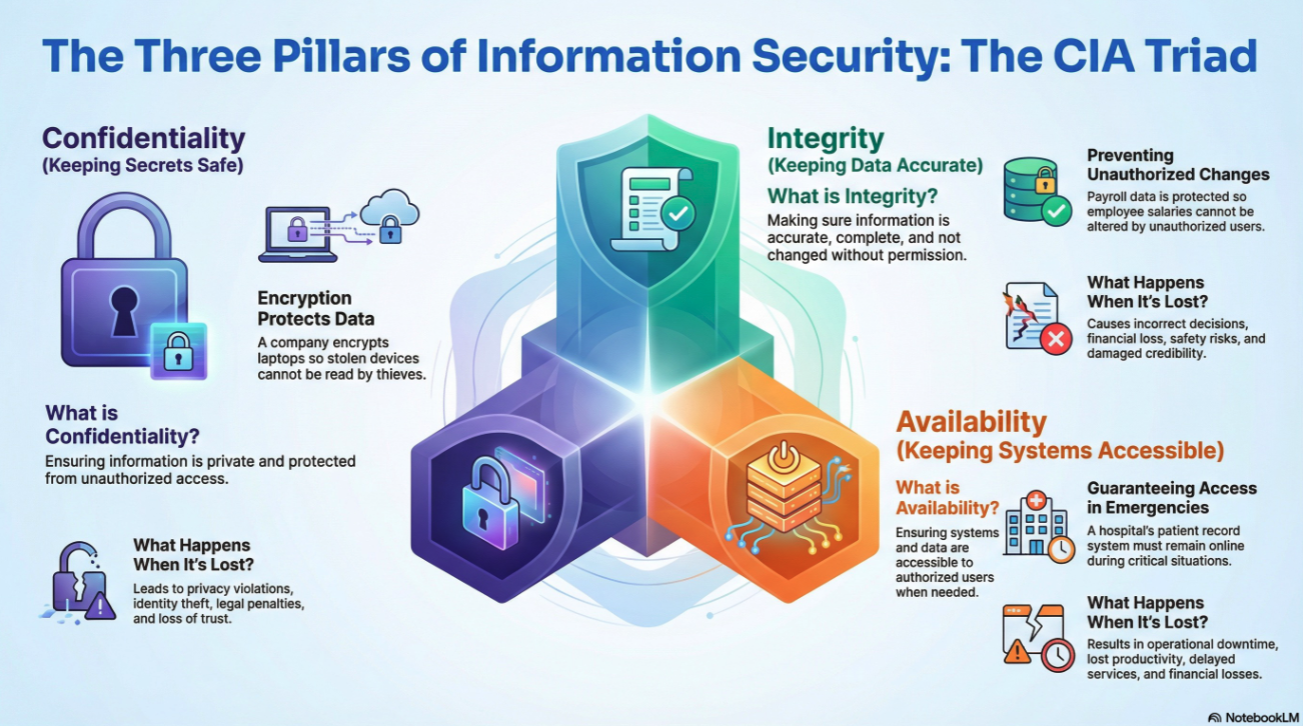
Computer security, physical security, information security
- Hardware
- Software
- Policies / procedures
- Plans
- Training
- Physical security (controlled access, locked equipmenu)
- Personnel security (screening process, background checks)
- 3rd Party Access security - Pivoting
Cybersecurity Umbrella
| GRC | Prevention | Defense |
|---|---|---|
| Policy/Procedures | Firewalls/IAM/Technical | SoC |
| Business Continuity | Vulnerability Mgmt | Threat Hunters |
| Information Assurance | Penetration Testing | Threat Intel |
| Risk Assessment | Security Researchers | Incident Response |
| Security Audits | Backups | Digital Forensics |
The Right Mindset
Cybersecurity is about much more than IT.
- Business Management / Risk Management
- Preserving trust
- Creating a culture
- Assumption an attack will occur
Develop an Acquisition Plan
- Create a general action plan and include the following:
- Resources required
- An outline showing how the acquisition will be executed
- Preservation of the evidence
- Security of the evidence before, during, and after the acquisition
- If possible, review any available technical specification about a disk drive's data storage media before you arrive
Understanding Storage Formats for Digital Evidence
- Data in a forensics acquisition tool is stored as an image file
- Three formats
- Raw format
- Proprietary formats
- Advanced Forensics Format (AFF)
Raw Format
- Makes it possible to write bit-stream data to files
- Advantages
- Fast data transfers
- Ignores minor data read errors on source drive (why could this be a problem?)
- Most computer forensics tools can read raw format
- Disadvantages
- Requires as much storage as original disk or data
- Tools might not collect marginal (bad) sectors (why could this be a problem?)
Proprietary Formats
- Most forensics tools have their own formats
- Features offered
- Option to compress or not compress image files (can you compress compress?)
- Can split an image into smaller segmented files
- Can integrate metadata into the image file
- Disadvantages
- Inability to share an image between different tools
- File size limitation for each segmented volume (most are 650 MB to 2 GB because of old FAT)
- WHAT IS FAT? https://youtu.be/V2Gxqv3bJCk?t=40
- The Expert Witness Compression format is unofficial standard
Advanced Forensics Format
- https://www.aff4.org/
- Developed by Dr. Simson L. Garfinkel as an open-source acquisition format
- Design goals
- Provide compressed or uncompressed image files
- No size restriction for disk-to-image files
- Provide space in the image file or segmented files for metadata
- Simple design with extensibility
- Open source for multiple platforms and Oss
- Internal consistency checks for self-authentication
- File extensions include
.afdfor segmented image files and.afmfor AFF metadata - AFF is open source
Determining the Best Acquisition Method
-
Types of acquisitions
- Static acquisitions and live acquisitions
-
Four methods of data collection
- Creating a disk-to-image file
- Creating a disk-to-disk
- Creating a logical disk-to-disk or disk-to-data file
- Creating a sparse data copy of a file or folder
-
Determining the best method depends on the circumstances of the investigation
-
Creating a disk-to-image file
- Most common method and offers most flexibility
- Can make more than one copy
- Copies are bit-for-bit replications of the original drive
- Compatible with many commercial forensics' tools
-
Creating a disk-to-disk
- When disk-to-image copy is not possible
- Tools can adjust disk's geometry configuration
-
Logical acquisition or sparse acquisition
- Can take several hours; use when your time is limited
- Logical acquisition captures only specific files of interest to the case
- Sparse acquisition collects fragments of unallocated (deleted) data
- For large disks
- PST or OST mail files, RAID servers
-
When making a copy, consider:
- Size of the source disk
- Lossless compression might be useful
- Use digital signatures for verification
- When working with large drives, an alternative is using lossless compression
- Whether you can retain the disk
- Time to perform the acquisition
- Where the evidence is located
- Size of the source disk
It's Just Data...Right?
- It's EVIDENCE!
- Collected data may be used as evidence of a cybercrime so the data has to be properly preserved so it can be authenticated.
Rule 901. Authenticating or Identifying Evidence
(a) In General. To satisfy the requirement of authenticating or identifying an item of evidence, the proponent must produce evidence sufficient to support a finding that the item is what the proponent claims it is.
Best Evidence Rule says a copy can be used in place of the original but it has to be properly authenticated.
Validating Data Acquisitions
- Validating evidence may be the most critical aspect of computer forensics
- Requires using a hashing algorithm utility
- Validation techniques
- CRC-32, MD5, and SHA-1 to SHA-512
Windows Validation Methods
- Commercial computer forensics programs also have built-in validation features
- Each program has its own validation technique
- Raw format image files don't contain metadata
- Separate manual validation is recommended for all raw acquisitions
RAID
R - Redundant
A - Array
I - Independent
D - Disks
Performing RAID Data Acquisitions
- What is RAID: https://www.youtube.com/watch?v=eE7Bfw9lFfs
- Acquisition of RAID drives can be challenging and frustrating because of how RAID systems are
- Designed
- Configured
- Sized
- Size is the biggest concern
- Many RAID systems now have exabytes of data
Understanding RAID
- Redundant array of independent disks (RAID)
- Computer configuration involving two or more disks
- Originally developed as a data-redundancy measure
- RAID 0
- Provides rapid access and increased storage
- Biggest disadvantage is lack of redundancy
- RAID 1
- Designed for data recovery
- More expensive than RAID 0
- RAID 2
- Similar to RAID 1
- Data is written to a disk on a bit level
- Has better data integrity checking than RAID 0
- Slower than RAID 0
- RAID 3
- Uses data stripping and dedicated parity
- Requires at least three disks
- RAID 4
- Similar to RAID 3
- Data is written in blocks
- RAID 5
- Similar to RAIDs 0 and 3
- Places parity recovery data on each disk
- RAID 6
- Redundant parity on each disk
- RAID 10(1+0), or mirrored striping
- Combination of RAID 1 and RAID 0
- Provides fast access and redundancy
- RAID 15(1+5)
- Combination of RAID 1 and RAID 5
- More costly option
Acquiring RAID Disks
-
Address the following concerns:
- How much data storage is needed?
- What type of RAID is used?
- Do you need to have all drives connected?
- Do you have the right acquisition tool?
- Can the tool read a forensically copied RAID image?
- Can the tool read split data saves of each RAID disk?
-
Copying small RAID systems to one large disk is possible
-
Vendors offering RAID acquisition functions
- Guidance Software EnCase
- X-Ways Forensics
- AccessData FTK
- Runtime Software
- R-Tools Technologies
-
Occasionally, a RAID system is too large for a static acquisition
- Retrieve only the data relevant to the investigation with the sparse or logical acquisition method