Chapter 5 - Network Access Control and Cloud Security
Network Access Control (NAC)
- An umbrella term for managing access to a network
- Authenticates users logging into the network and determines what data they can access and actions they can perform
- Also (sometimes) examines the health of the user’s computer or mobile device
NAC systems deal with three categories of components:
-
Access requester (AR)
- Node that is attempting to access the network and may be any device that is managed by the NAC system, including workstations, servers, printers, cameras, and other IP-enabled devices
- Also referred to as supplicants, or clients
-
Policy server
- Determines what access should be granted
- Based on actual supplicant and sometimes health of supplicant
- Often relies on backend systems (next slide)
-
Network access servers (NAS)
- Consists of more services (next slide)
- Functions as an access control point for users in remote locations connecting to an enterprise’s internal network
- May include its own authentication services or rely on a separate authentication service from the policy server
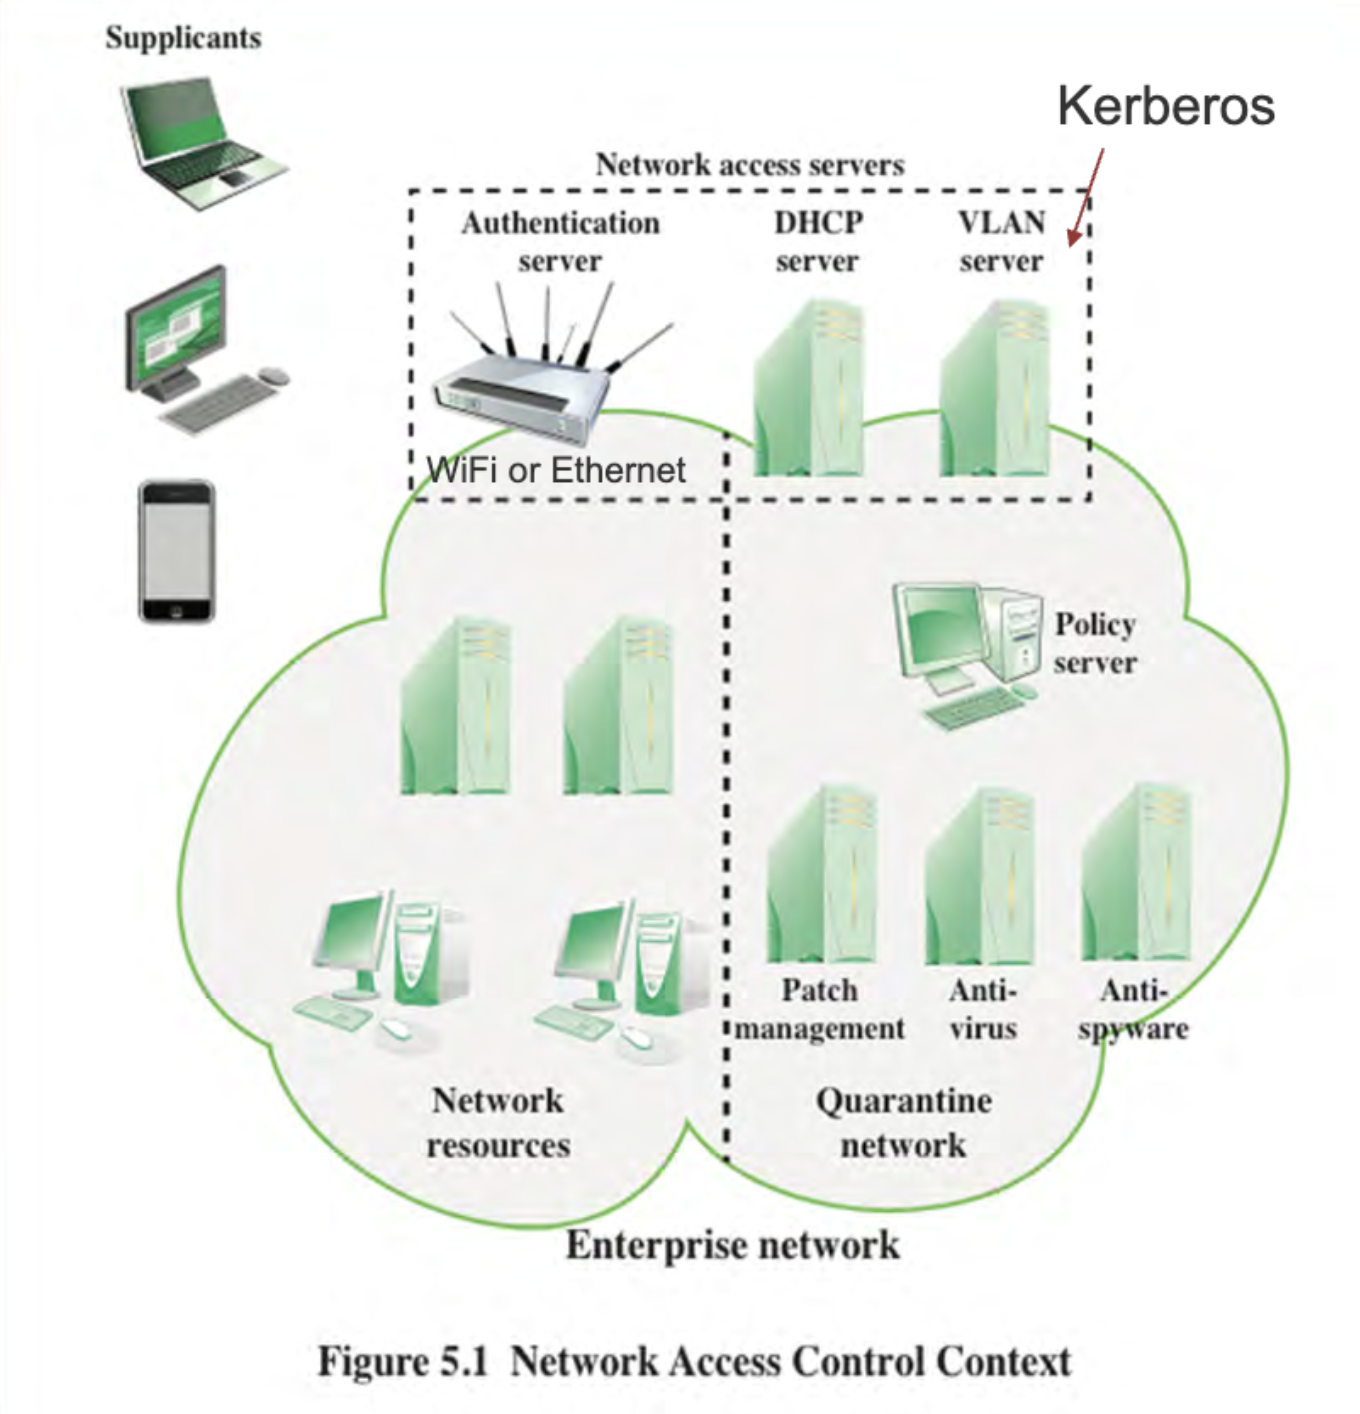
- The policy server decides if a requestor is allowed to enter the network
- It could contain an authentication service
- It is often common to see Wi-Fi access points to also contain a sort of authentication service
Network Access Enforcement Methods
- The actions that are applied to supplicants to regulate access to the enterprise network
- Many vendors support multiple enforcement methods simultaneously, allowing the customer to tailor the configuration by using one or a combination of method
Common NAC enforcement methods:
- IEEE 802.1X (EAP)
- Virtual local area networks (VLANs)
- Firewall policies
- DHCP management
Notes:
- For example firewall policies are the ones that decide if you are allowed to access the wi-fi or a service
- It can be a combination of these features that decides this
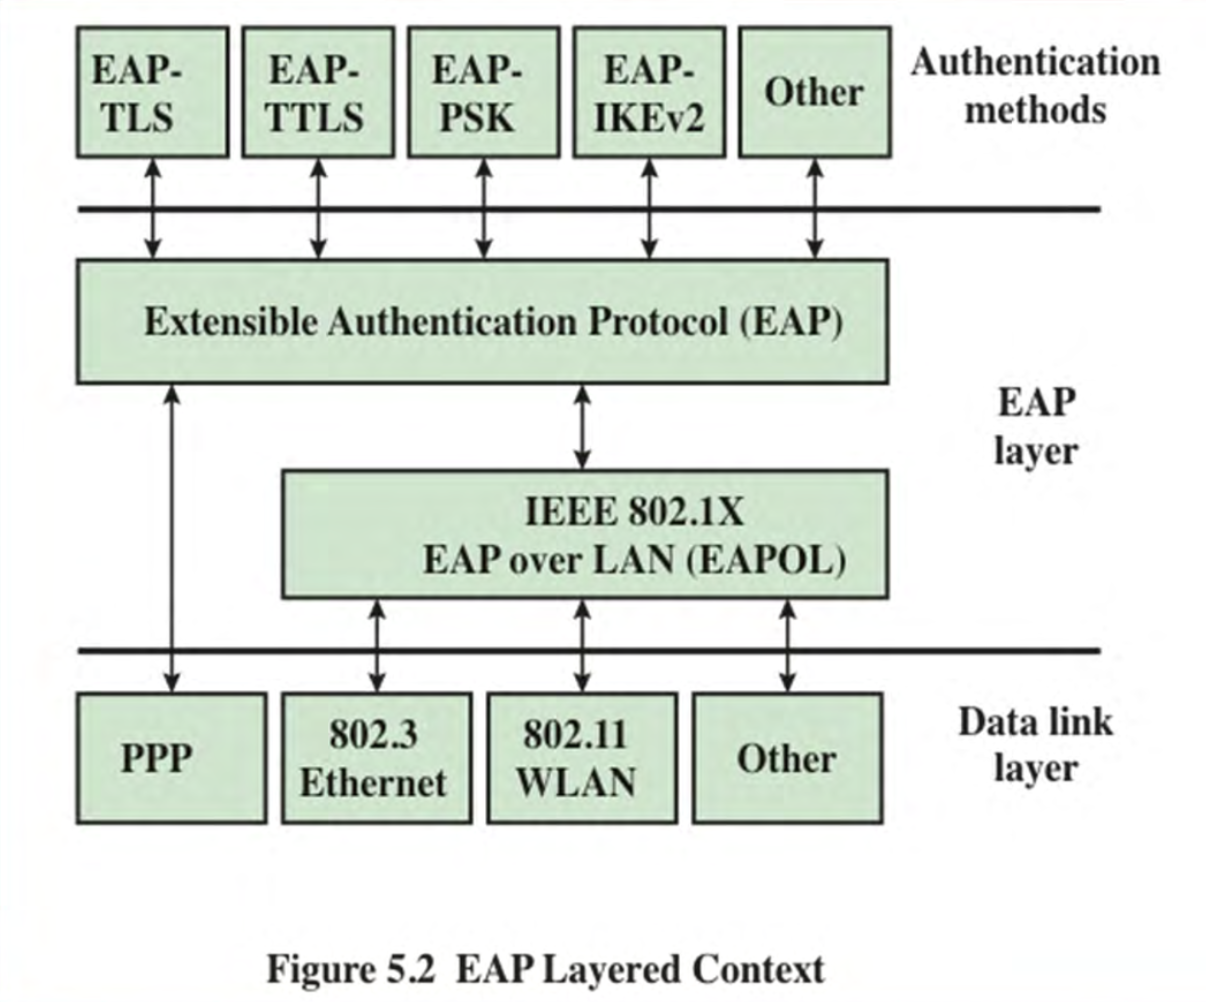
- Extensible Authentication Protocol (EAP)
- It is called extensible because you can use a number of different authentication methods
- 802.1X is the actual standard defining messages for implementing the EAP.
- PPP = Point-to-point protocol (not commonly used anymore)
- Maybe we could have Bluetooth as well and stuff like that
- Note at the top we have things within the Transport Layer
- After you have received an IP address
- At the bottom you have the Data link layer, which is where physical communication protocols work
Authentication Methods
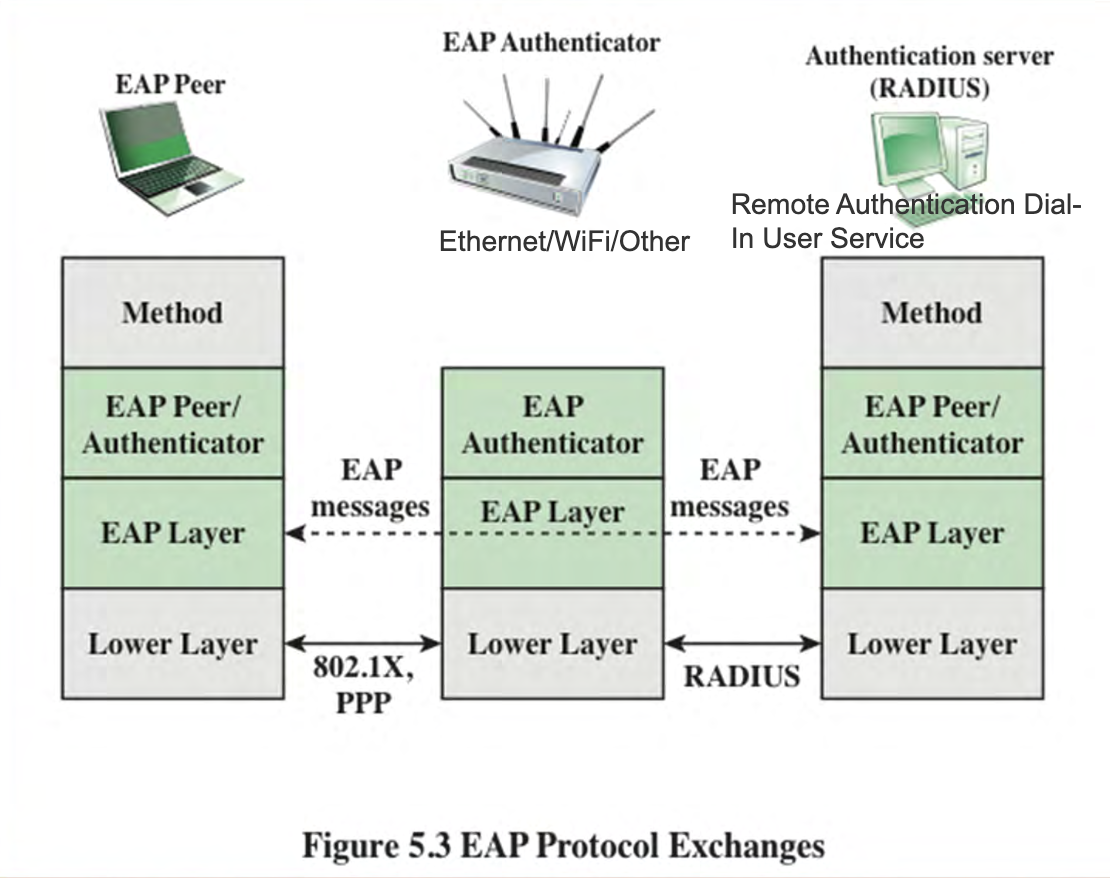
- EAP provides a generic transport service for the exchange of authentication information between a client system and an authentication server
- The basic EAP transport service is extended by using a specific authentication protocol that is installed in both the EAP client and the authentication serve
Commonly supported EAP methods:
- EAP Transport Layer Security, RFC 5216
- EAP Tunneled TLS, RFC 5281 (only cert. at server)
- EAP Generalized Pre-Shared Key, RFC 5433
- EAP-IKEv2, RFC 5106
Notes I:
- EAP Transport Layer Security
- Running the same authentication as TLS
- EAP Tunneled TLS
- There is a certificate at the server
- This is an automatic authentication, we are not allowed to do anything
- Your machine will forward the certificate itself
- Something more will be required to authenticate the client, a password!
- Typed or stored in the client side
- EAP Generalized Pre-Shared Key
- Very simple authentication protocol
- A key is installed on both sides and it stays there
- Client has its key
- Server has its key
- It is risky to share that key
- This is what you see in old Wi-Fi configurations
- EAP-IKEv2
- There is a Key Exchange method based on Diffie Hellman
Notes II:
- RADIUS is the most commonly used in these cases
- It is old but still being used a lot for both Wi-Fi and Ethernet
Notes III:
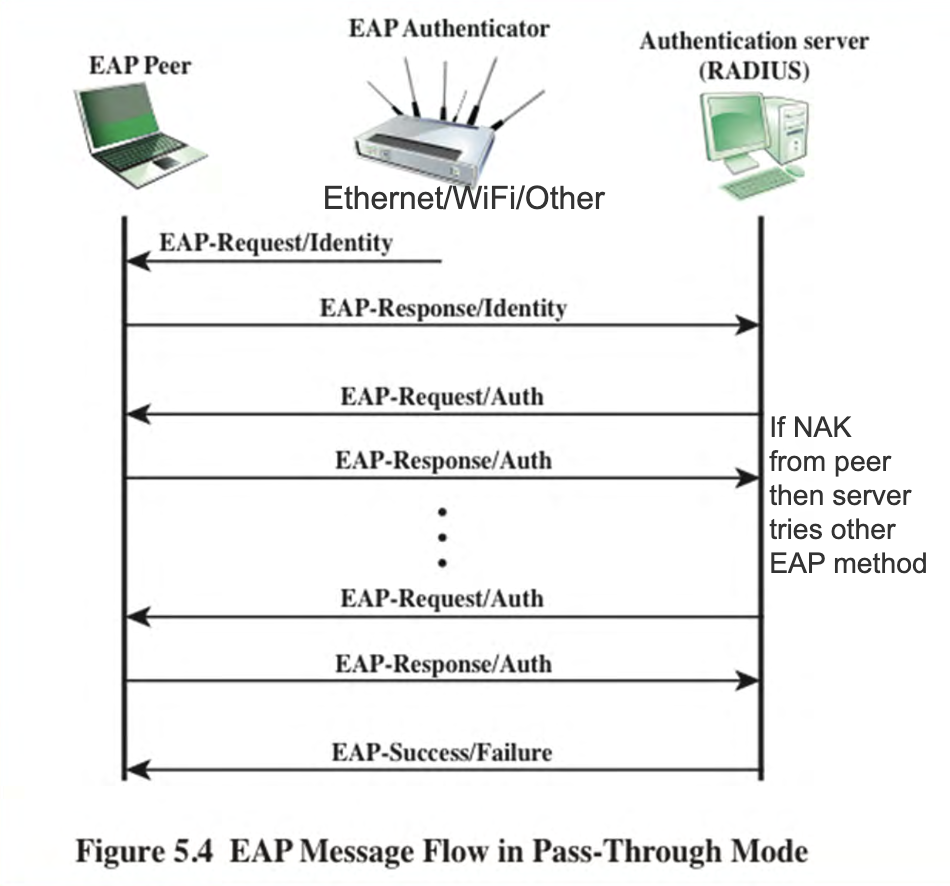
- Note the EAP router is not actually the authentication server, the authentication server is RADIUS
- So an attacker that targets this EAP router will only know the IPs which is not that significant compared to authentication information
- NAK = No Acknowledgement
- The router can try different authentication methods if any fails
EAP Message Content
- Code
- Type of message (Request, Response, Success, Failure)
- Identifier
- To match Responses with Requests
- Length
- Total length in number of bytes
- Data
- Information related to authentication (not in Success, Failure)
Terminology Related to IEEE 802.1X
Authenticator
- An entity at one end of a point-to-point LAN segment that facilities authentication of the entity to the other end of the link.
Authentication exchange
- The two-party conversation between systems performing an authentication process.
Authentication process
- The cryptographic operations and supporting data frames that perform the actual authentication.
Authentication server (AS)
- An entity that provides an authentication service to an authenticator. This service determines, from the credentials provided by supplicant, whether the supplicant is authorized to access the services provided by the system in which the authenticator resides.
Authentication transport
- The datagram session that actively transfers the authentication exchange between two systems.
Bridge port
- A port of an IEEE 802.1D or 802.1Q bridge. (Bridge = switch)
Edge port
- A bridge port attached to a LAN that has no other bridges attached to it.
Network access port
- A point of attachment of a system to a LAN. It can be a physical port, such as a single LAN MAC attached to a physical LAN segment, or a logical port, for example, an IEEE 802.11 association between a station and an access point.
Port access entity (PAE)
- The protocol entity associated with a port. It can support the protocol functionality associated with the authenticator, the supplicant, or both.
Supplicant
- An entity at one end of a point-to-point LAN segment that seeks to be authenticated by an authenticator attached to the other end of that link.
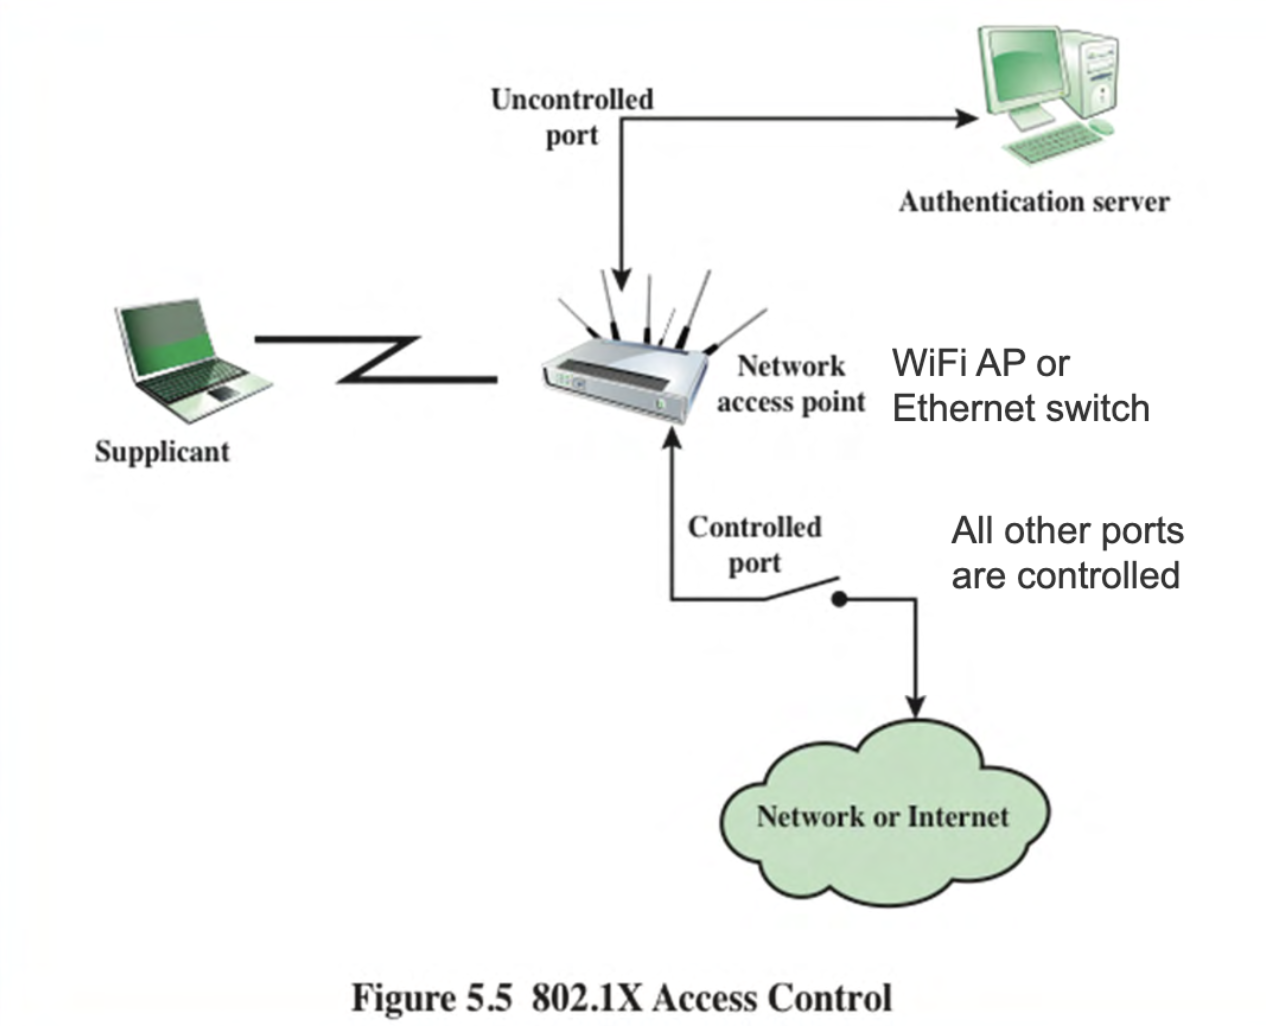
Notes:
- The whole idea is the concept of controlled ports
- If a port is closed, then there is no further access
- If a port is open, then there is access
Common EAPOL Frame Types
EAPOL-EAP and EAPOL-Key caries EAP message
| Frame Type | Definition |
|---|---|
| EAPOL-EAP | Contains an encapsulated EAP packet. |
| EAPOL-Start | A supplicant can issue this packet instead of waiting for a challenge from the authenticator. |
| EAPOL-Logoff | Used to return the state of the port to unauthorized when the supplicant if finished using the network. |
| EAPOL-Key | Used to exchange cryptographic keying information. |
EAPOL MSG Content
- Protocol version
- Version of EAPOL
- Packet type
- Start, EAP, Key, Logoff, etc.
- Body length
- Length in bytes of body
- Packet body
- Payload, e.g., an EAP packe
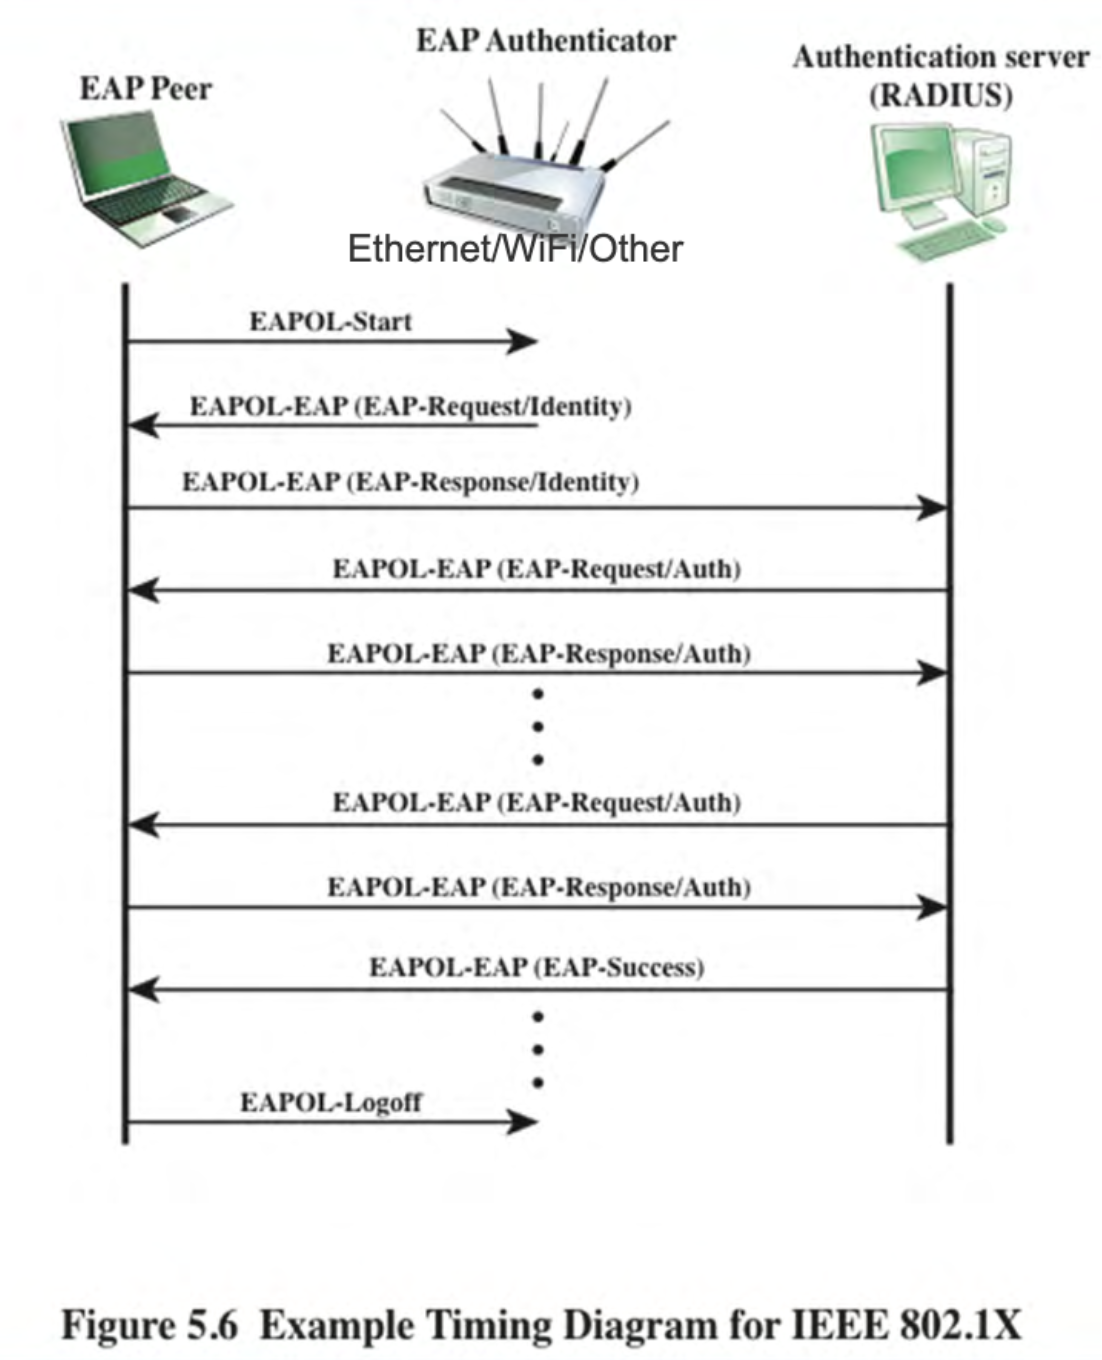
EAP & Radius Messages
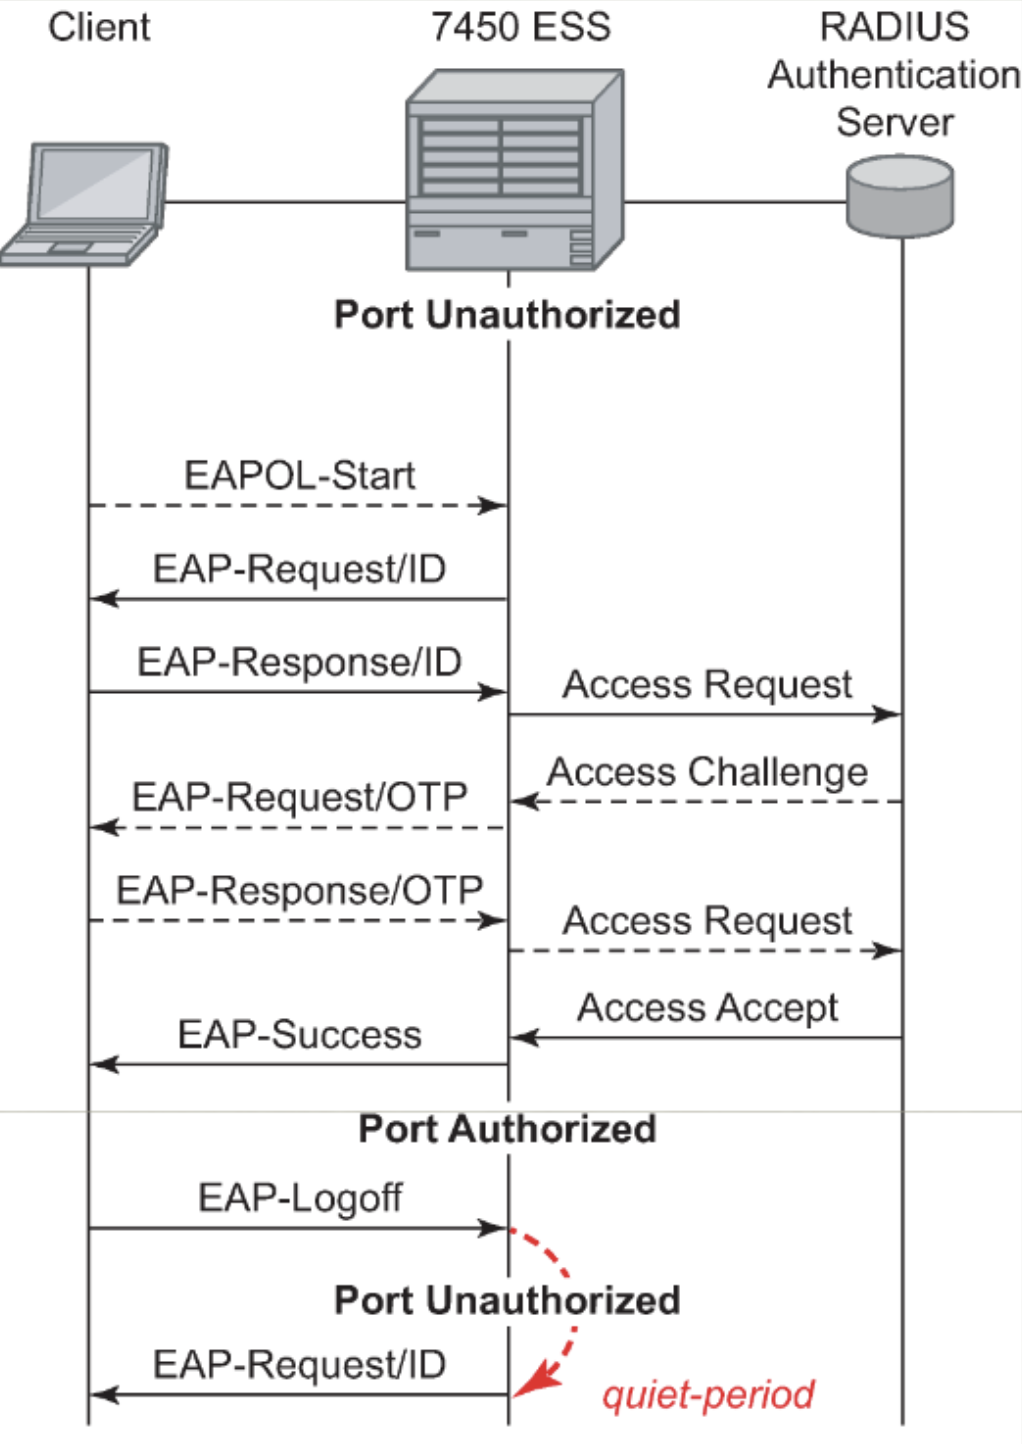
- EEE 802.1X with further details
- 7450 ESS is an Ethernet switch from Nokia
- EAPOL-Start is optional
- Other dashed arrows depend on EAP authentication method
Cloud Computing
- NIST defines cloud computing, in NIST SP-800-145 (The NIST Definition of Cloud Computing ), as follows:
"A model for enabling ubiquitous, convenient, on-demand network access to a shared pool of configurable computing resources (e.g., networks, servers, storage, applications, and services) that can be rapidly provisioned and released with minimal management effort or service provider interaction. This cloud model promotes availability and is composed of five essential characteristics, three service models, and four deployment models."
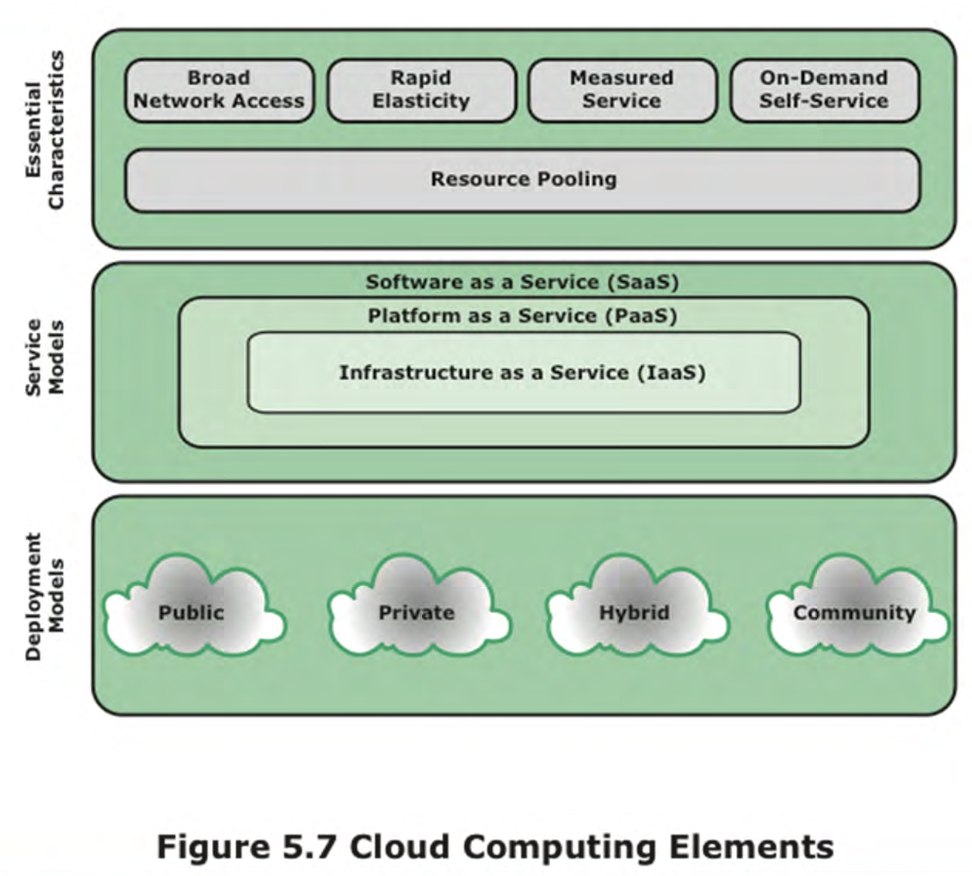
Notes:
- IaaS is providing metal (cpus, network equipment, etc) or virtual machines
- You would manage everything else yourself (software, services, etc)
- PaaS provides the tools and interfaces to create services
- "complete development and deployment environment in the cloud, with resources that enable you to deliver everything from simple cloud-based apps to sophisticated, cloud-enabled enterprise applications."
- SaaS is a product sold as a whole, e.g. Linux, Google services, etc.
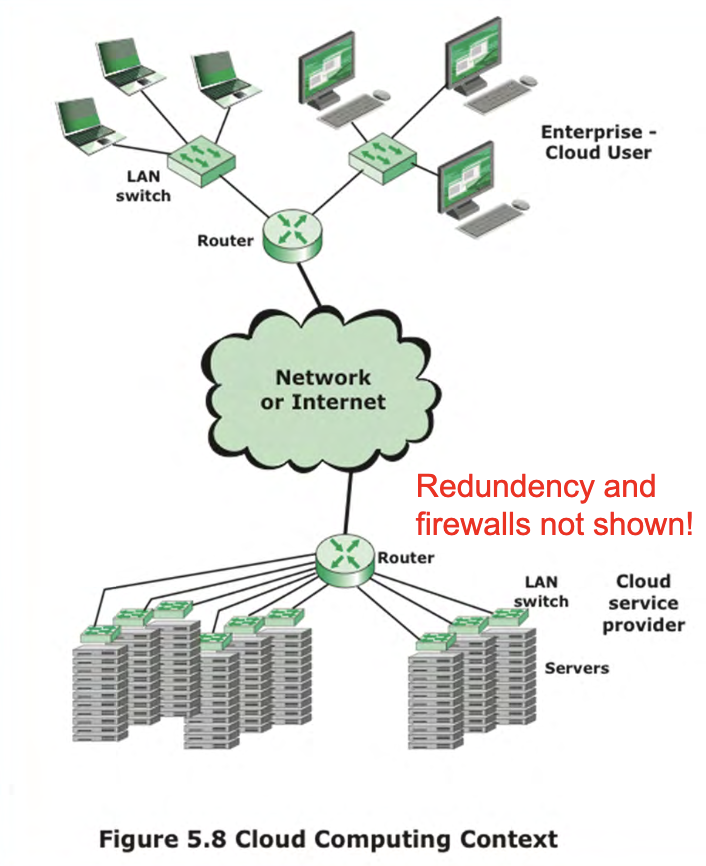
Notes:
- Is this enough?
- No! we miss security (firewalls) and redundancy (secure availability)
Cloud Computing Reference Architecture
- NIST SP 500-292 (NIST Cloud Computing Reference Architecture ) establishes a reference architecture, described as follows:
"The NIST cloud computing reference architecture focuses
on the requirements of “what” cloud services provide, not a
“how to” design solution and implementation. The
reference architecture is intended to facilitate the
understanding of the operational intricacies in cloud
computing. It does not represent the system architecture of
a specific cloud computing system; instead, it is a tool for
describing, discussing, and developing a system-specific
architecture using a common framework of reference."
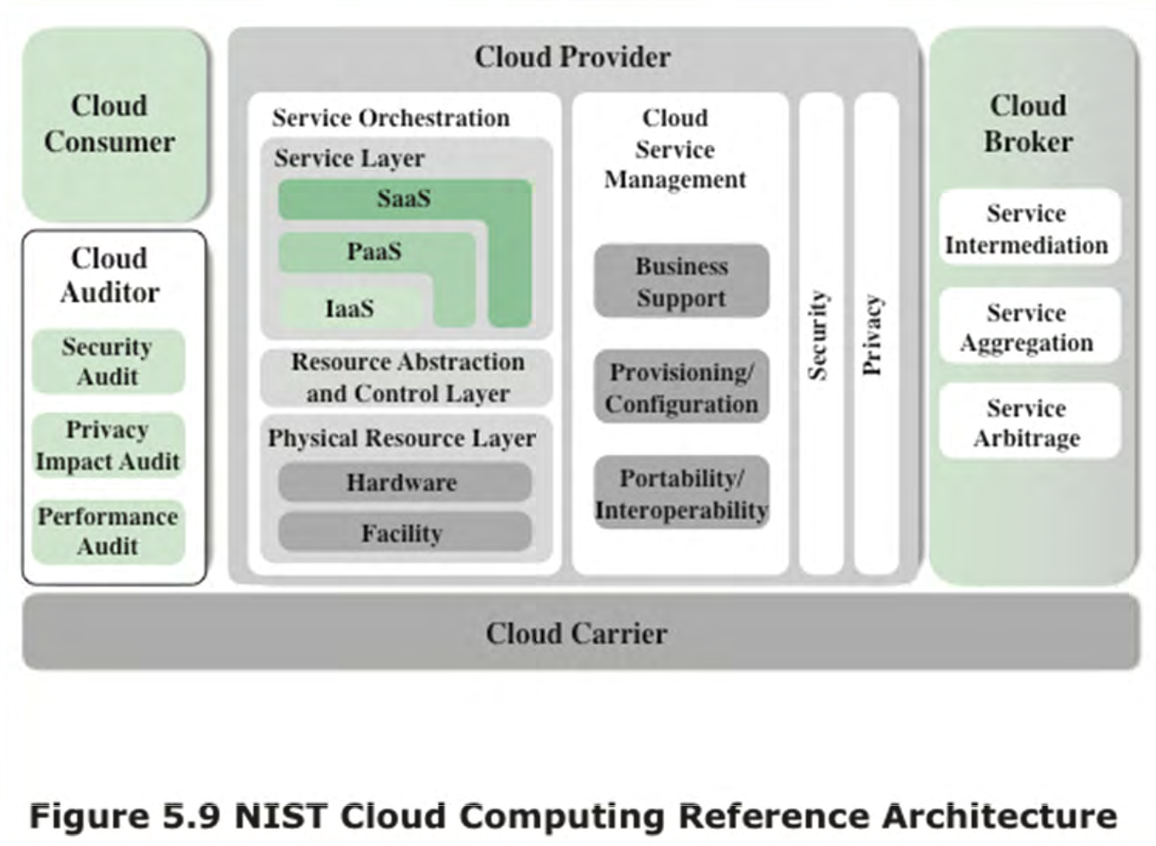
Notes:
- Broker services are services that lie on top of what the cloud provider serves
- e.g. Dropbox builds something on top to authenticate their users to the Cloud Provider
- They have their own cloud infrastructure but also uses AWS
Cloud Provider
Cloud Provider (CP)
- For each of the three service models (SaaS, PaaS, IaaS) CP wants to offer, the CP provides the storage and processing facilities needed to support that service model, together with a cloud interface for cloud service consumers
- For SaaS, the CP deploys, configures, maintains, and updates the operation of the software applications on a cloud infrastructure so that the services are provisioned at the expected service levels to cloud consumers
- For PaaS, the CP manages the computing infrastructure for the platform and runs the cloud software that provides the components of the platform, such as runtime software execution stack, databases, and other middleware component
- For IaaS, the CP acquires the physical computing resources underlying the service, including the servers, networks, storage, and hosting infrastructur
Cloud Security Risks and Countermeasures
- The Cloud Security Alliance
[CSA10]lists the following as the top cloud specific security threats, together with suggested countermeasures:
Abuse and criminal use of cloud computing:
- Countermeasures: stricter initial registration and validation processes; enhanced credit card fraud monitoring and coordination; comprehensive introspection of customer network traffic; monitoring public blacklists for one’s own network blocks
Malicious insiders
- Countermeasures: enforce strict supply chain management and conduct a comprehensive supplier assessment; specify human resource requirements as part of legal contract; require transparency into overall information security and management practices, as well as compliance reporting; determine security breach notification processes
Insecure interfaces and APIs
- Countermeasures: analyzing the security model of CP interfaces; ensuring that strong authentication and access controls are implemented in concert with encryption machines; understanding the dependency chain associated with the API
Shared technology issues
- Countermeasures: implement security best practices for installation/configuration; monitor environment for unauthorized changes/activity; promote strong authentication and access control for administrative access and operations; enforce SLAs for patching and vulnerability remediation; conduct vulnerability scanning and configuration audits
Data loss or leakage
- Countermeasures: implement strong API access control; encrypt and protect integrity of data in transit; analyze data protection at both design and run time; implement strong key generation, storage and management, and destruction practices; backup of data; storage at more location.
- GDPR compliance?
- Would a service be compliant if it made sure that the data is stored in encrypted form? not necessary, GDPR requires a bit more
Account or service hijacking
- Countermeasures: prohibit the sharing of account credentials between users and services; leverage strong two-factor authentication techniques where possible; employ proactive monitoring to detect unauthorized activity; understand CP security policies and SLAs
Unknown risk profile
- Countermeasures: disclosure (make available) of applicable logs and data; partial/full disclosure of infrastructure details; monitoring and alerting on necessary information
Data Protection in the Cloud
- The threat of data compromise increases in the cloud
- Database environments used in cloud computing can vary significantly
Multi-instance mode:
- Provides a unique DBMS running on a virtual machine instance for each cloud subscriber
- This gives the subscriber complete control over role definition, user authorization, and other administrative tasks related to security
Multi-tenant model:
-
Provides a predefined environment for the cloud subscriber that is shared with other tenants, typically through tagging data with a subscriber identifier
-
Tagging gives the appearance of exclusive use of the instance, but relies on the CP to establish and maintain a sound secure database environment
-
Data must be secured while at rest, in transit, and in use, and access to the data must be controlled
- The client can employ encryption to protect data in transit and data stored in database, though this involves key management responsibilities for the CP
- HW solutions exist for decryption when data is loaded by CPU
-
A straightforward solution to the security problem is to encrypt the entire database and not provide the keys to the service provider
- The user has little ability to access individual data items based on searches or indexing on key parameters
- The user might have to download entire tables from the database, decrypt the tables, and work with the results (see next slides)
- To provide more flexibility it must be possible to work with the database in its encrypted form; this is possible with Homomorphic encryption
Notes:
- The main issue here is that the keys are stored by the Cloud Provider
- The key needs to come from somewhere managed by the Cloud Provider
- Another solution is to encrypt keys inside a database in the client side
- Makes the client responsible for encryption and decryption
- Makes things bit complicated in all senses
- If you want to read from an encrypted database but do not want to encrypt it in the cloud then you have to manage it yourself
- Problems if we deal with gigabyte-long tables
- Homomorphic encryption:
- Encryption algorithms that allow for encrypting data and afterwards run some calculations on them
- Example: if you encrypt an integer and encrypt another integer, then you can perform operations with these integers in the encrypted form and decrypt the result at the end.
- This can help perform operations while still dealing with the encryption form
- It is very heavy, and requires a lot of CPU power and memory because we are dealing with a lot of data
Privacy and Security For Storage Services
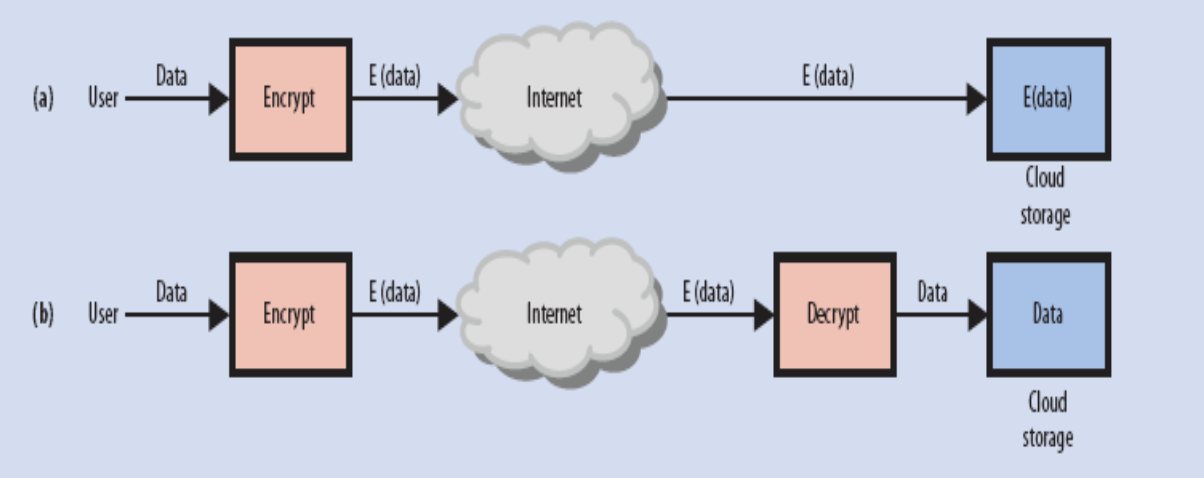
Two encryption scenarios for cloud computing.
- (a) Data remain decrypted at the cloud storage site, preventing unauthorized access through the internet; the cloud vendor cannot access the data either.
- (b) Data are decrypted by the cloud vendor to enable necessary operations on the data.
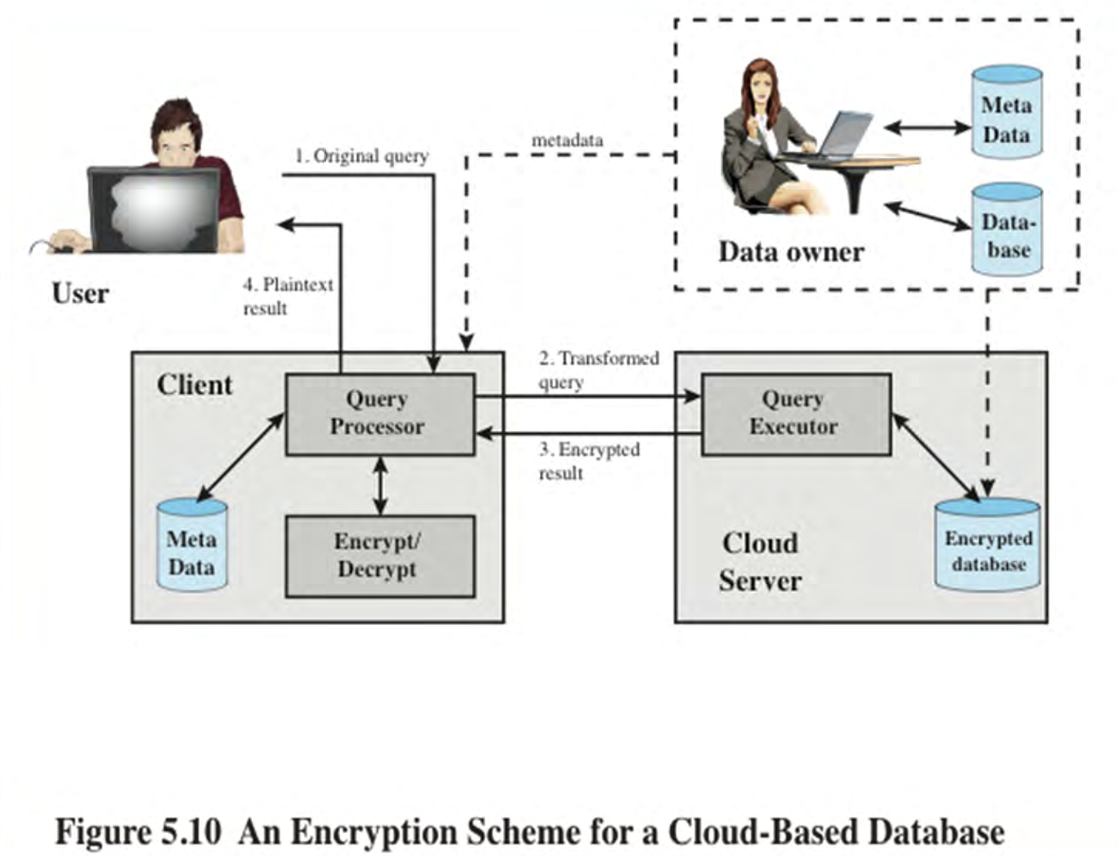
- Ideal is to only decrypt at the client side
Cloud Security As a Service (SECAAS)
- The Cloud Security Alliance defines SecaaS as the provision of security applications and services via the cloud either to cloud-based infrastructure and software or from the cloud to the customers’ on- premise systems
- The Cloud Security Alliance has identified the following SecaaS categories of service:
- Identity and access management
- Data loss prevention
- Web security
- E-mail security
- Security assessments
- Intrusion management
- Security information and event management
- Encryption
- Business continuity and disaster recovery
- Network security
Notes:
- "With no security is like we are purchasing a car without brakes"
Native Hypervisor
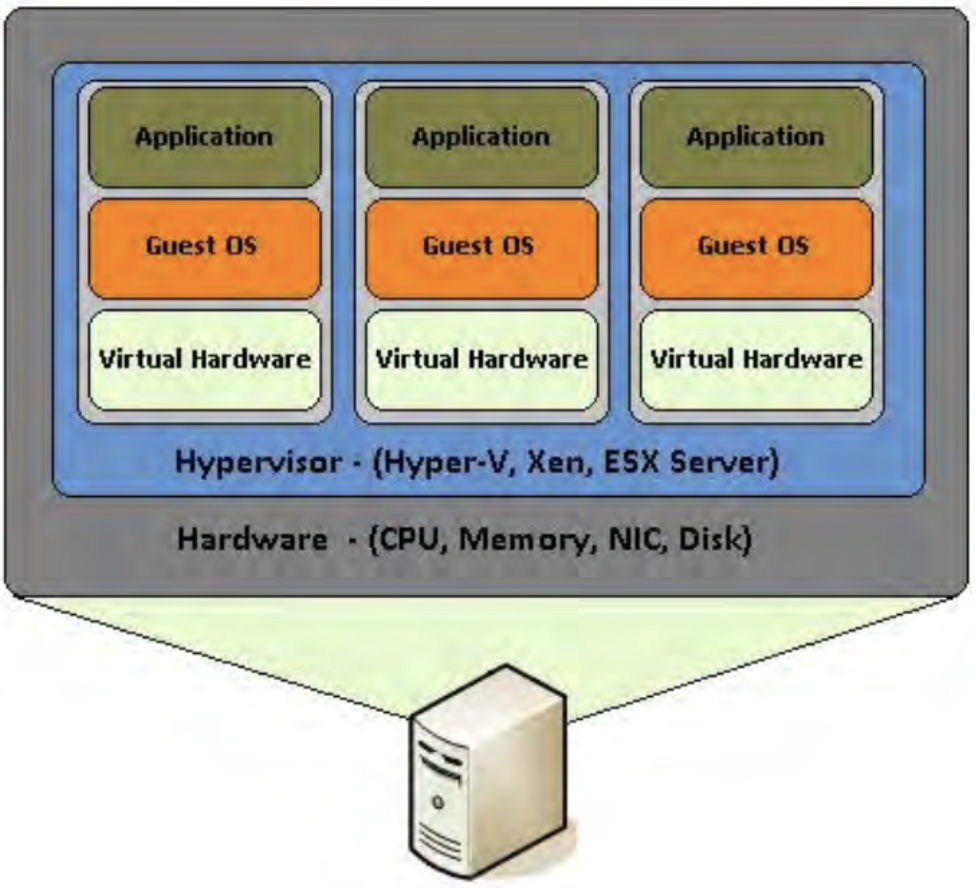
How many people can shared a single CPU?
- ~100 to ~1000 depending on the task
Main Cloud Security Approaches
- Virtual machine segmentation
- Hypervisor much efficiently protect VMs against each other, including all resources allocated to them
- Perhaps memory (and file) encryption
- Database segmentation (multi-instance, multi-tenant)
- Secure authentication and authorization to protect database owners against each other
- Perhaps encryption of databases
- VM introspection
- Hypervisor service which examines the internal states of VMs (malware detection, etc.)
- Denial of Service protection
- In general more resources (e.g., bandwidth) and advanced firewalls & intrusion detection systems
Summary
-
Network access control
- Elements of a network access control system
- Network access enforcement methods
-
Extensible authentication protocol
- Authentication methods
- EAP exchanges
-
Cloud security as a service
-
IEEE 802.1X port-based network access control
-
Cloud computing
- Elements
- Reference architecture
-
Cloud security risks and countermeasures
-
Data protection in the cloud
-
Addressing cloud computing security concerns