Introduction to Lab (API Attacks)
As we progress through the module, we will practice identifying and exploiting each of the OWASP API Top 10 Security Risks using a RESTful web API to fully understand these vulnerabilities.
Inlanefreight E-Commerce Marketplace
Our loyal customer, Inlanefreight, has ventured into the world of e-commerce marketplaces with Inlanefreight E-Commerce Marketplace. The marketplace's business model enables customers to browse and purchase products offered by suppliers. Each supplier is associated with a specific company. The marketplace generates revenue by charging a fee for each product a customer purchases from a supplier.
To operate the marketplace and facilitate transactions between customers and suppliers, Inlanefreight has developed a multi-tenant web API that employs Role-based Access Control (RBAC) as its access control policy. Throughout the sections, we will interact with the API using different users with varying roles. Credentials associated with the pentestercompany.com domain represent supplier accounts, while those with hackthebox.com are identified as customer accounts.
For each user that we authenticate, they will have pre-assigned roles determined by the admin of Inlanefreight E-Commerce Marketplace. The admin has adopted a straightforward naming convention for roles: the roles share the same name as the endpoints to which they provide access to. For example, if a user has the role Suppliers_GetAll, it implies that the user is authorized to interact with the endpoint that retrieves all supplier records (which, in this case, is /api/v1/suppliers).
Our objective is to report any vulnerabilities found to the admin of Inlanefreight E-Commerce Marketplace. A detailed report of all discovered vulnerabilities will assist the admin in taking appropriate actions to secure the API. Each vulnerability will be mapped to its relevant CWE weakness.
Swagger API User Interface
Despite the frontend of Inlanefreight E-Commerce Marketplace still being in active development, the web API can be accessed via a Swagger UI at the /swagger path (make sure to include it after the port of the spawned target machine). We will use this interface throughout the module to explore and assess the security of the marketplace's API, which includes over 60 endpoints:
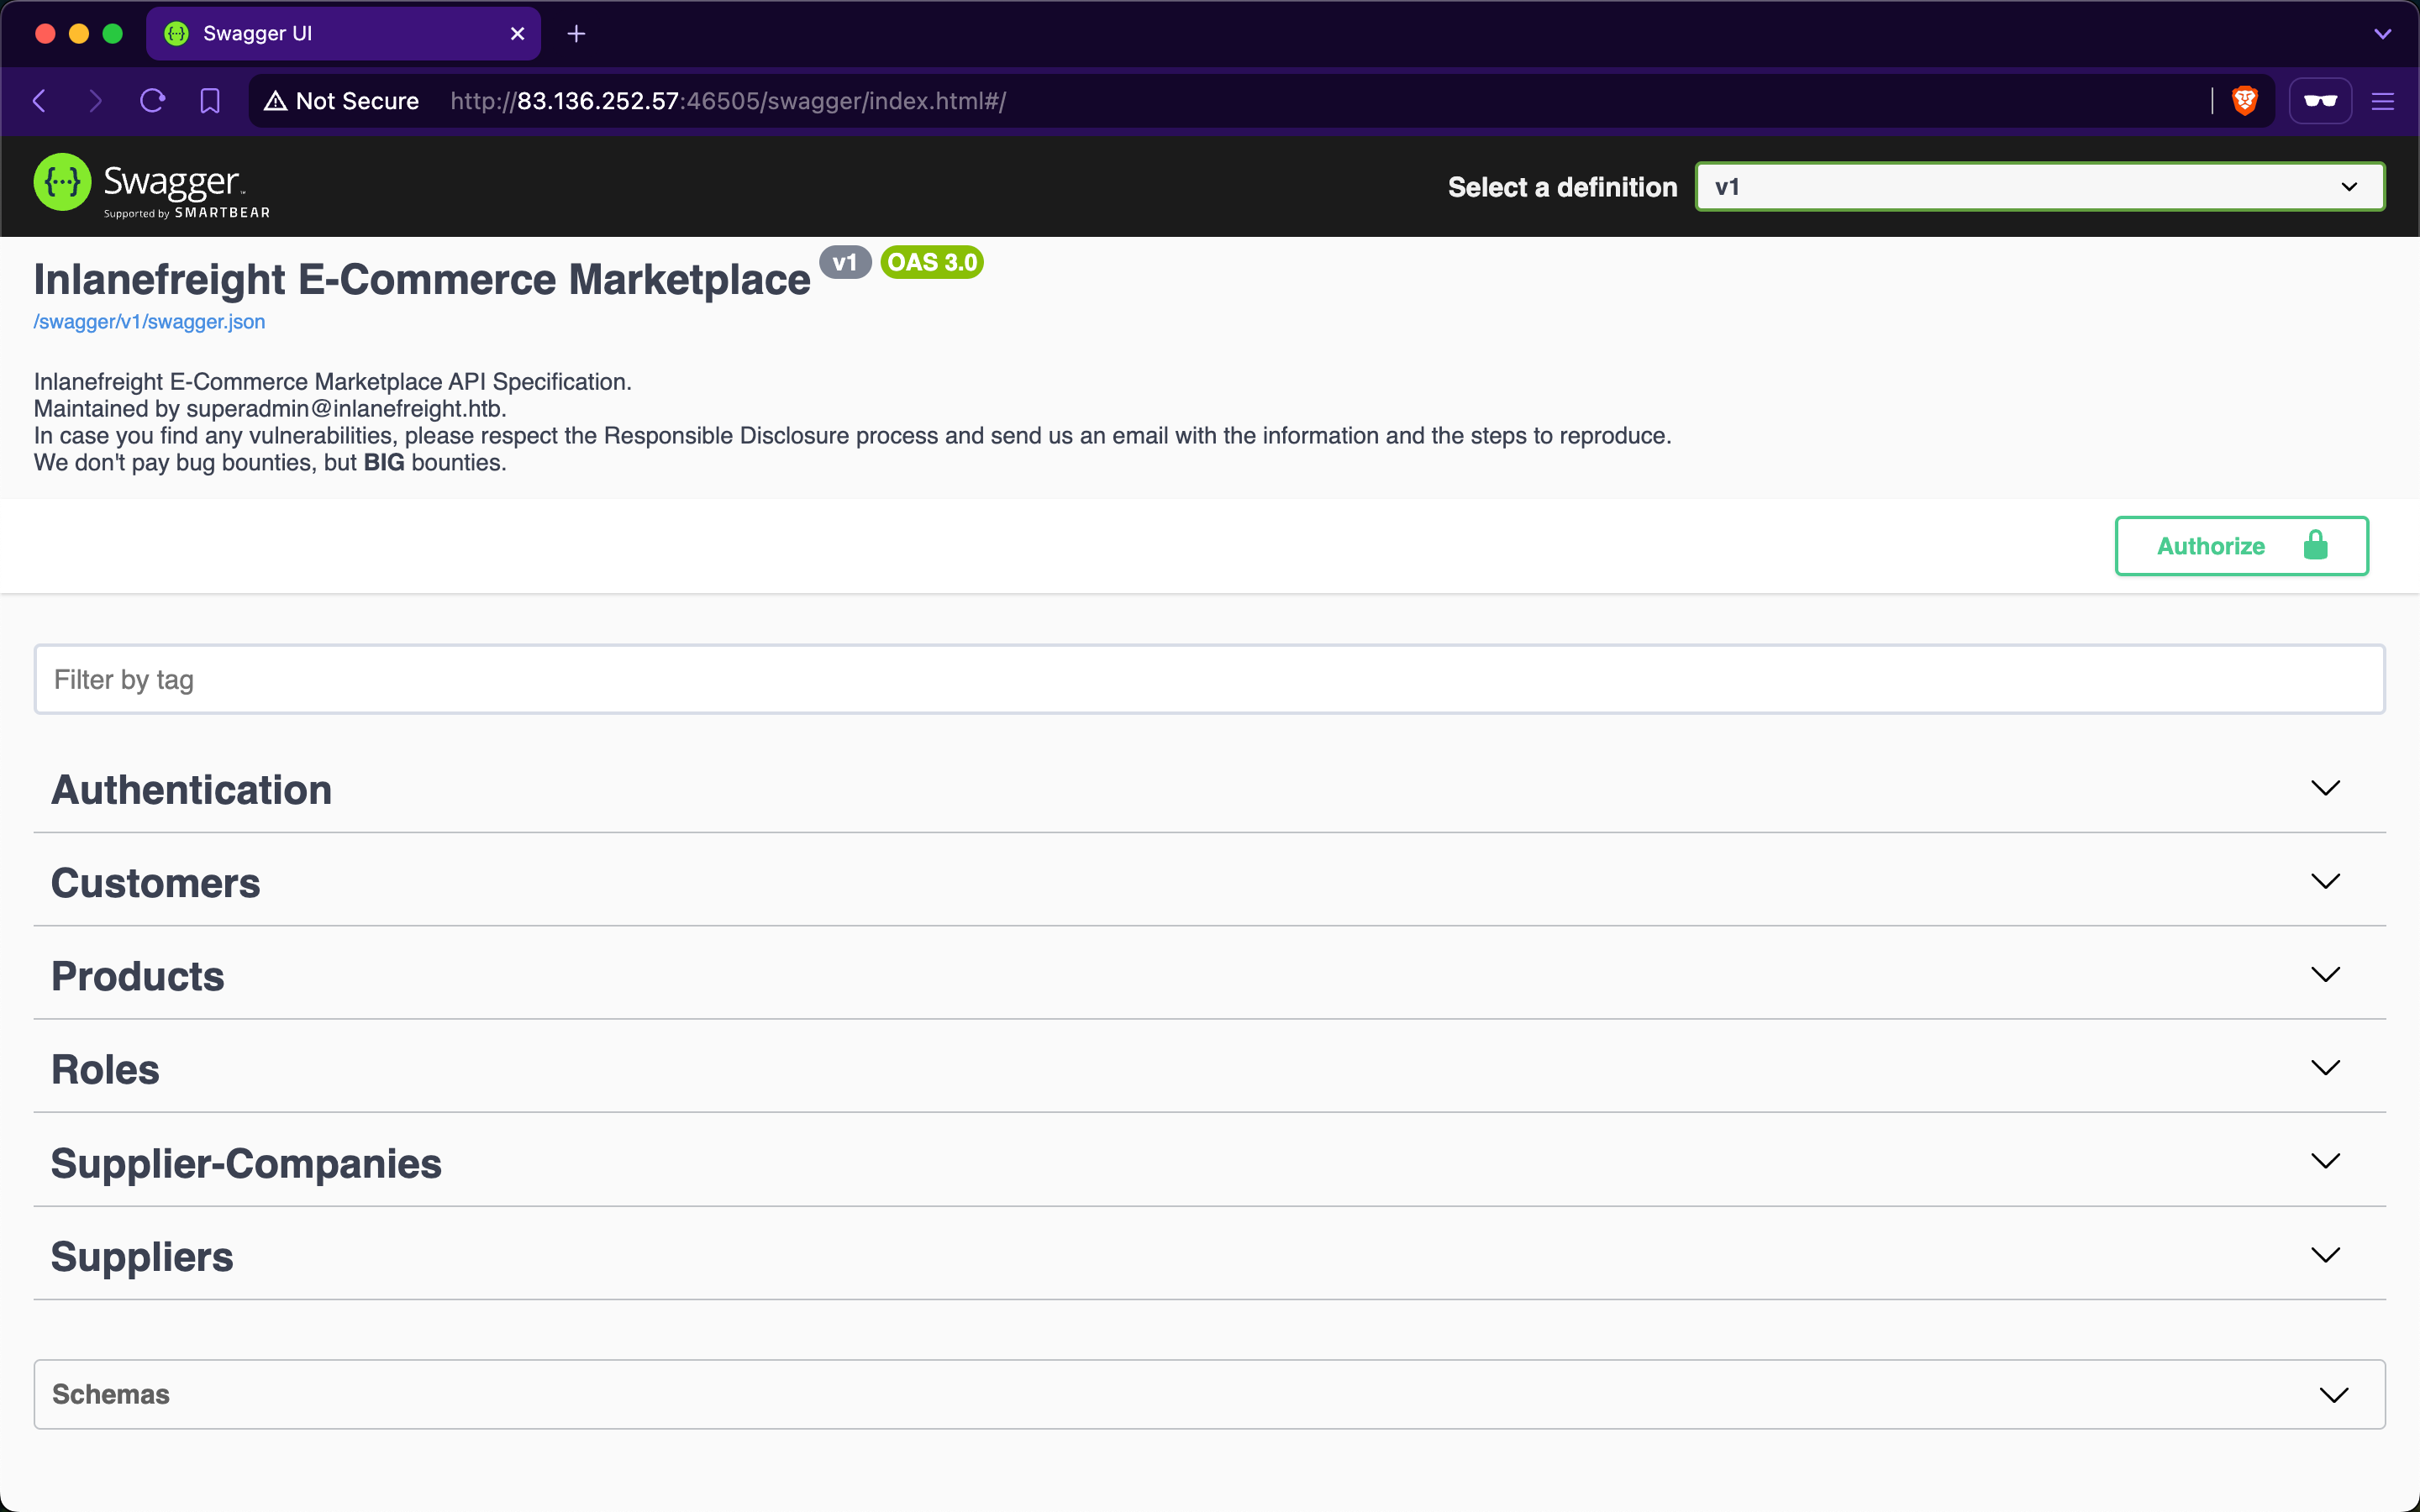
The key entities that the marketplace encompasses include Customers, Products, Supplier-Companies, and Suppliers. We will also interact with other entities as we progress through the sections.
Exercise
TARGET: 154.57.164.73:32630
Challenge 1
Interact with any endpoint and inspect the response headers; what is the name of the server that the web API uses?
First of course we need to visit 154.57.164.73:32630/swagger on a browser:
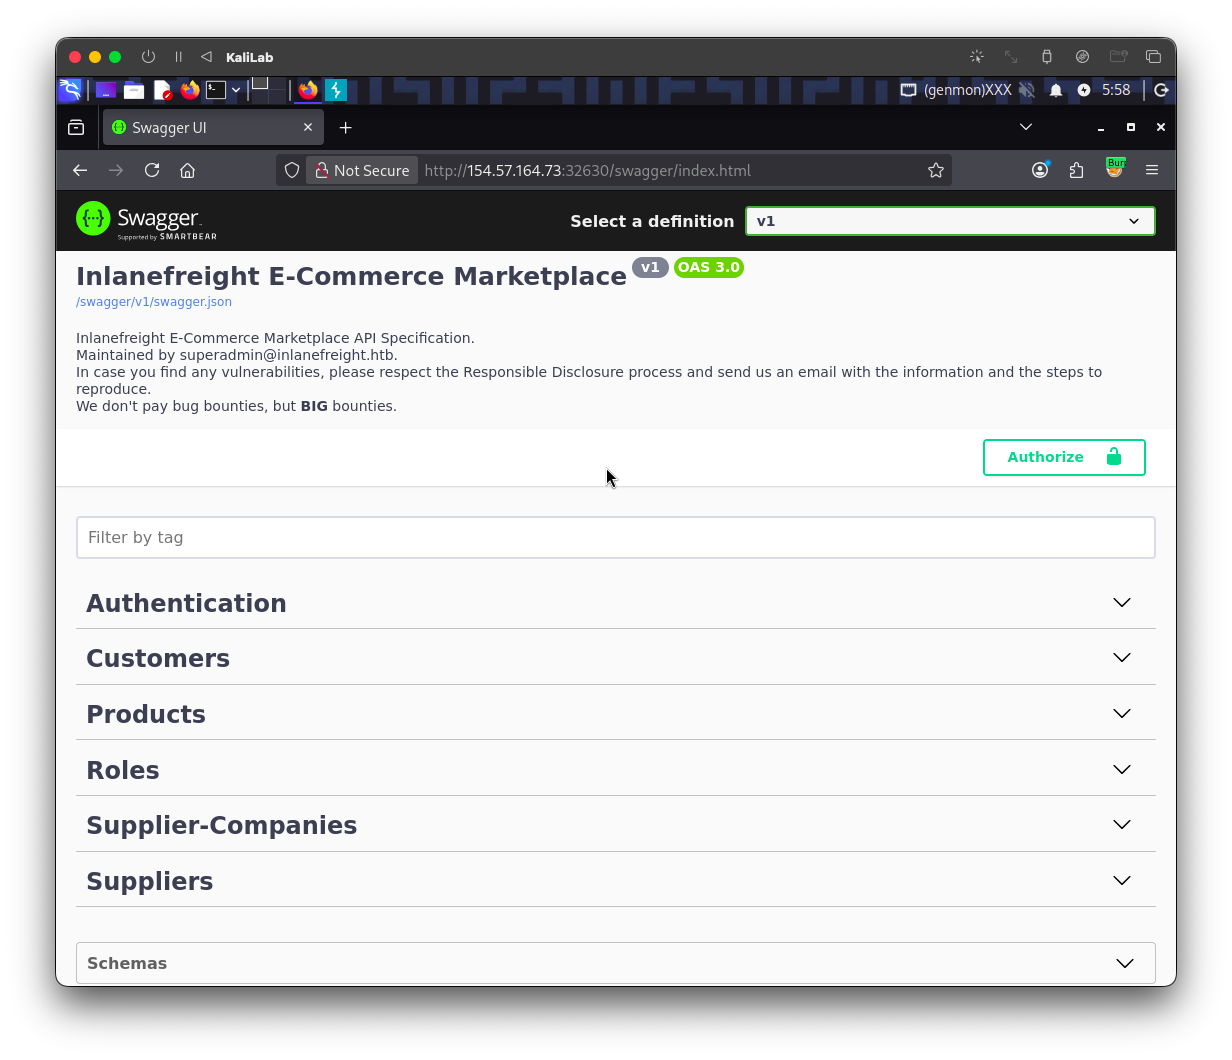
In this case I will be interacting with the Suppliers endpoint:
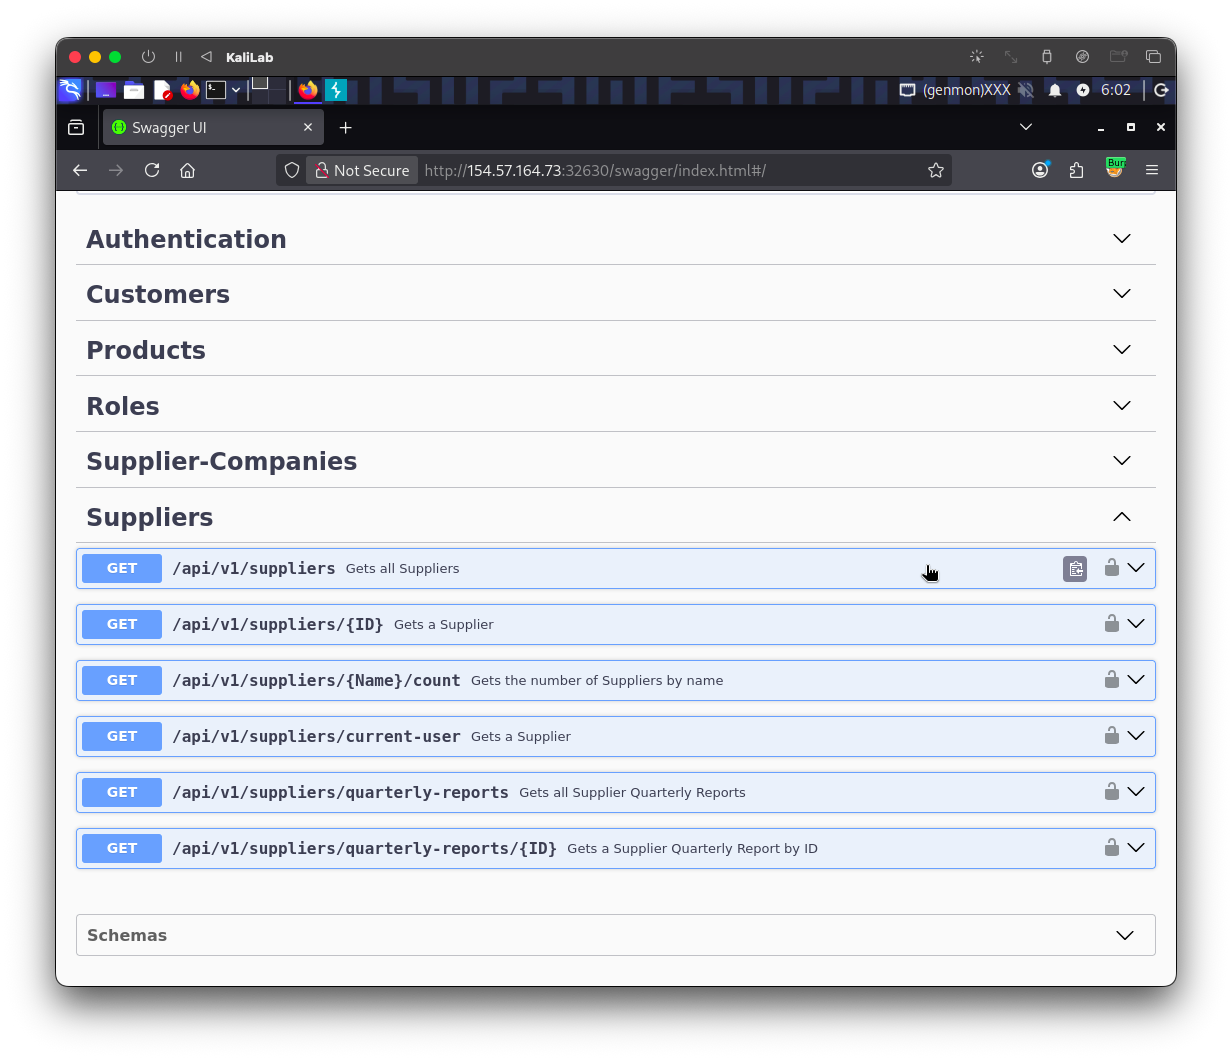
Now I will execute the first api call: /api/v1/suppliers and see the response headers:
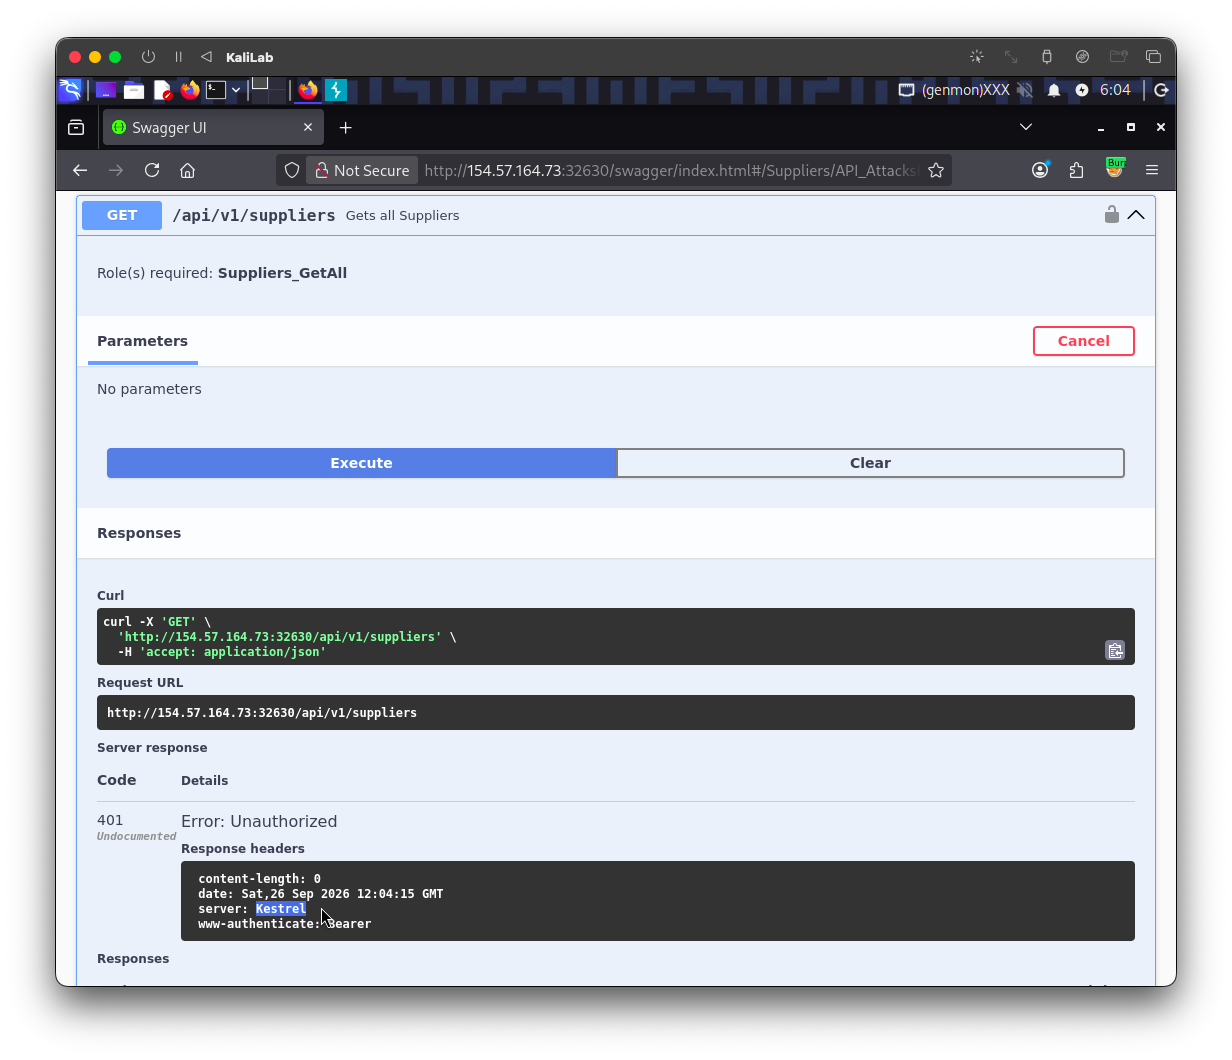
- The response header contains the name of the server:
Kestrel
flag: Kestrel
Challenge 2
There is only one endpoint belonging to the Roles group. Submit its path.
For this we just need to check the Roles group and see the list of available api endpoints:
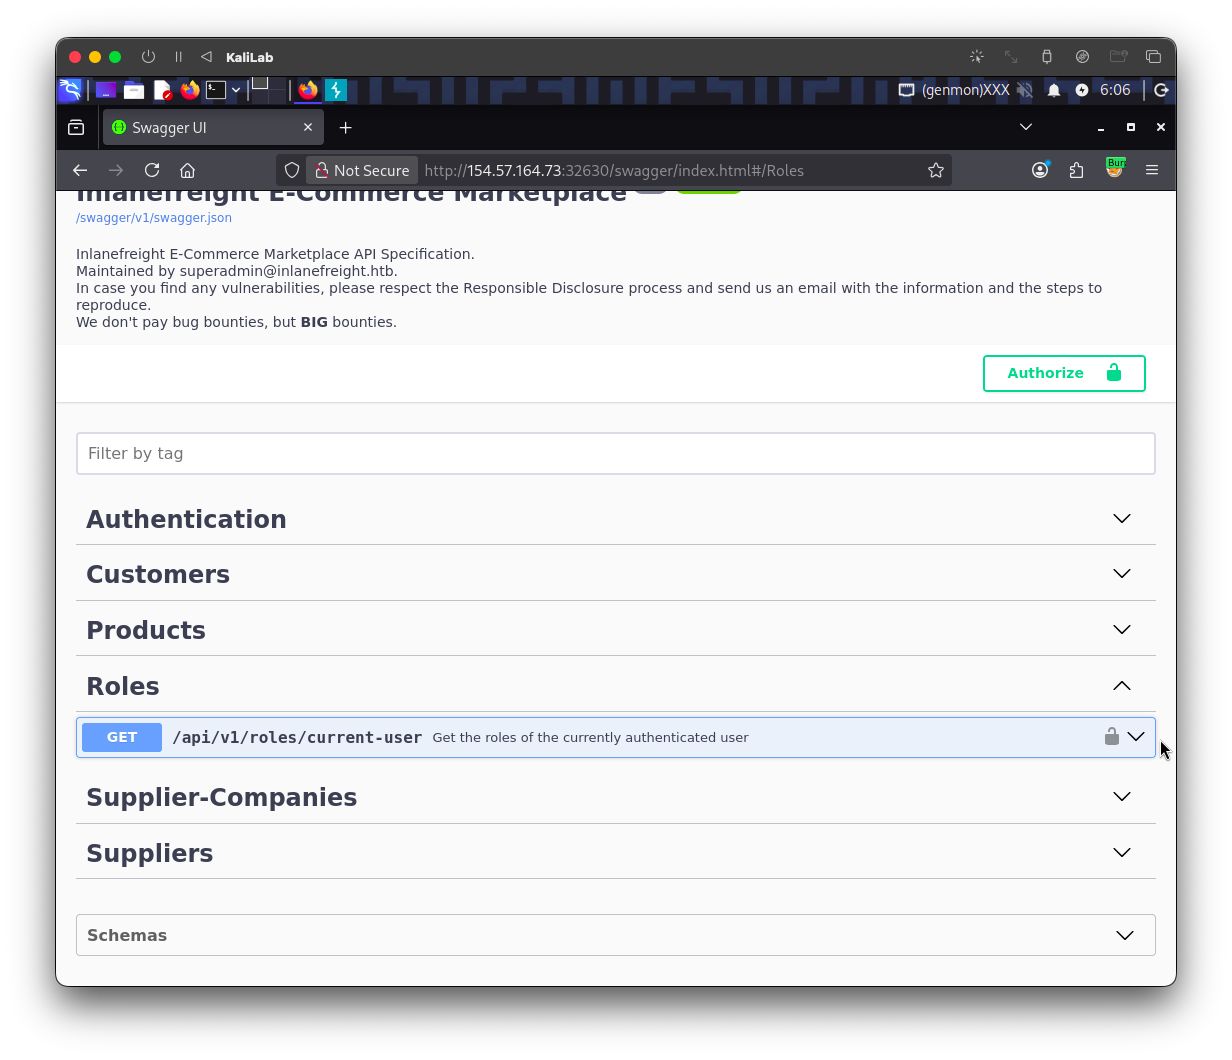
flag: /api/v1/roles/current-user